


AWS HIPAA Eligible Services: RDS, S3, Lambda, Bedrock 2026
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/aws-hipaa-eligible-services
Last updated: October 20, 2026
AWS HIPAA eligible services are the AWS products that Amazon will cover under its Business Associate Addendum (BAA). Only those services may store, process, or send protected health information (PHI). The list is the gate. AWS lists 174 HIPAA eligible services as of its October 15, 2026 update. The list changes often. The everyday building blocks are all on it: EC2, S3, RDS, Aurora, Lambda, DynamoDB, and Amazon Bedrock. But eligible does not mean compliant. AWS HIPAA eligible services CAN hold PHI once your BAA is signed and your settings are right. This guide shows how to read the list. It answers the common service questions. And it covers what stays your job.
TL;DR: Quick answer
AWS HIPAA eligible services are the ones the AWS BAA covers. You accept the BAA in AWS Artifact. PHI must stay inside that list (45 CFR § 164.308(b)).
AWS lists 174 HIPAA eligible services as of its October 15, 2026 update. RDS, Aurora, S3, EC2, Lambda, DynamoDB, EBS, KMS, CloudTrail, CloudFront, SES, HealthLake, and Bedrock are all on it.
Eligible is not compliant. You still set up encryption, access, and logging for every service you use.
About a dozen entries carry limits in brackets. The CloudFront entry excludes delivery through Embedded Points of Presence, and the RDS entry names six database engines.
The list changes. Check AWS's own page before you send PHI to a new service. A popular service can still be off the list.
Rather not run it yourself? Our managed hosting runs on single-tenant AWS from $229 a month, with a BAA signed within 24 hours of signup.
What does "HIPAA eligible" actually mean?
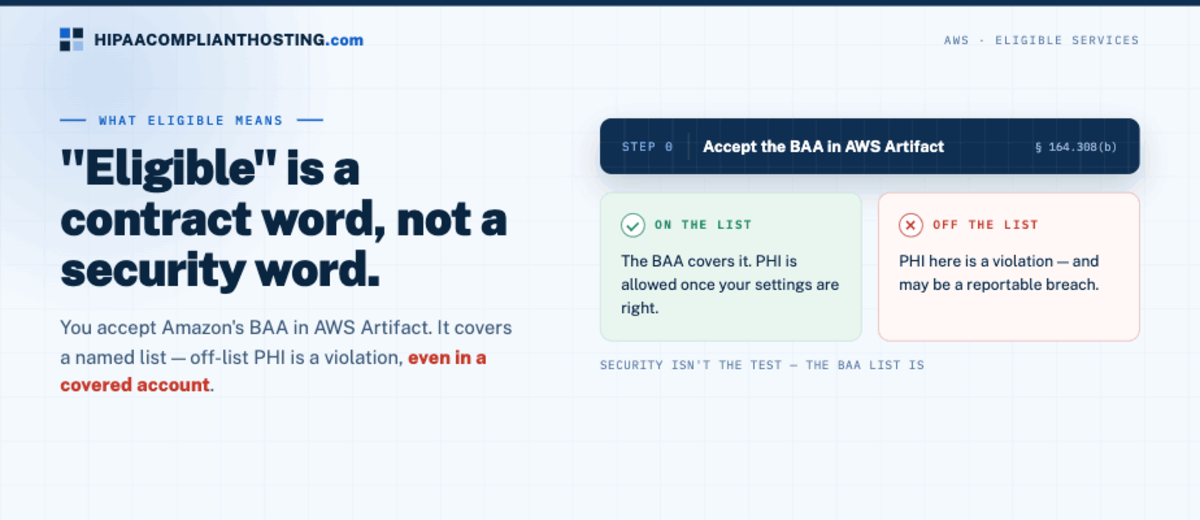
HIPAA requires a signed Business Associate Agreement before a vendor holds PHI for you. Amazon meets this with its Business Associate Addendum. You accept it in AWS Artifact. The BAA does not cover everything AWS sells. It covers a named list. That is what "eligible" means. AWS says it has demonstrated HIPAA compliance for each listed service, subject to the shared responsibility model. Use an off-list service for PHI and you are in violation, even in a covered account. The wider verdict on the platform is in is AWS HIPAA compliant. This guide zooms in on the list itself.
How to read the AWS HIPAA eligible services list
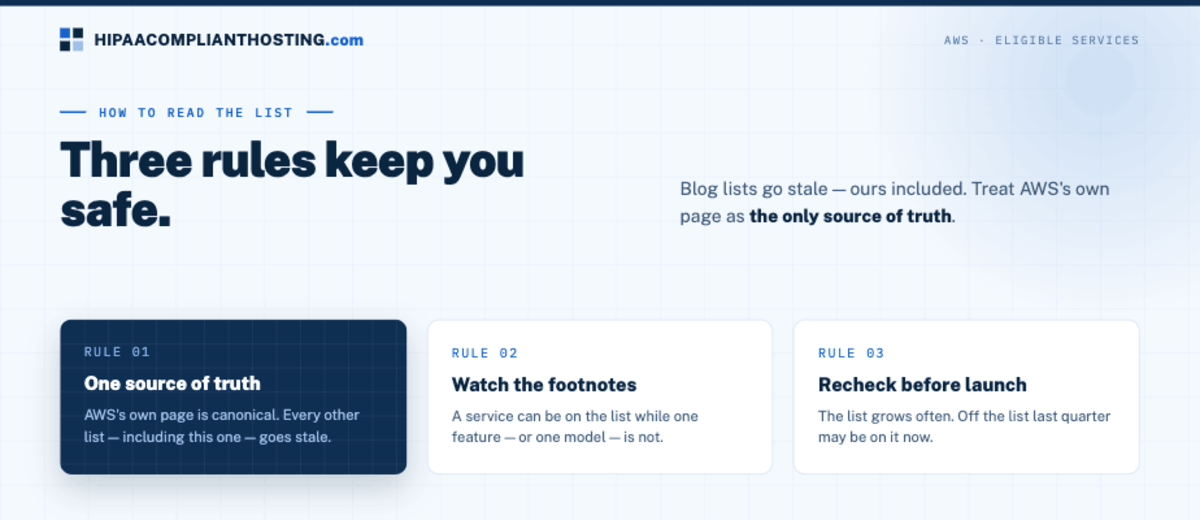
Amazon publishes the official list and updates it through the year. Three rules keep you safe. First, treat AWS's page as the only source of truth. Blog lists go stale, ours included. Second, read the brackets. AWS says every feature of a listed service is eligible unless the entry notes otherwise. About a dozen entries do. The Amazon CloudFront entry excludes delivery through CloudFront Embedded Points of Presence. The AWS Directory Service entry excludes Simple AD. Third, recheck before each new launch. The AWS HIPAA eligible services list grows often. A service that was off the list last quarter may be on it now.
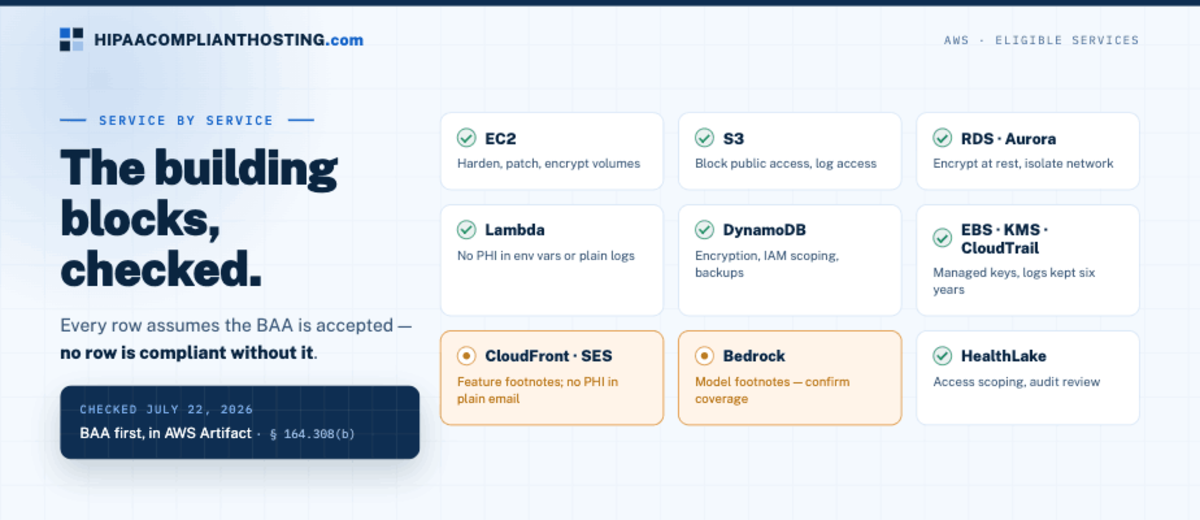
The building blocks, checked October 20, 2026
Service | Eligible? | What you still set up |
|---|---|---|
Amazon EC2 (servers) | Yes | OS hardening, patching, encrypted volumes, restricted access |
Amazon S3 (object storage) | Yes | Block public access, encrypt buckets, log access |
Amazon RDS and Aurora (databases) | Yes. The RDS entry names six engines: SQL Server, MySQL, Oracle, PostgreSQL, Db2, and MariaDB. Aurora has its own entry. | Encryption at rest, network isolation, least-privilege users |
AWS Lambda (serverless code) | Yes | Keep PHI out of environment variables and plain logs |
Amazon DynamoDB (NoSQL) | Yes | Encryption, IAM scoping, backup policy |
Amazon EBS, AWS KMS, AWS CloudTrail | Yes | Encrypted disks, managed keys, and a log retention period you choose. HIPAA sets none for logs; many organizations keep six years. |
Amazon CloudFront (CDN) | Yes, except delivery through CloudFront Embedded Points of Presence | TLS to viewers and to your origin; do not opt PHI traffic into Embedded Points of Presence |
Amazon SES (email) | Yes | Set your configuration set's TLS policy to Require. By default, SES sends unencrypted if TLS fails. |
AWS WAF, AWS Backup, Amazon CloudWatch Logs | Yes | Rules on login and form pages, tested restores, and tight access to any log that holds PHI |
Amazon Bedrock (AI models) | Yes | Check each model's data retention mode; note AI use in your risk analysis |
AWS HealthLake (health data) | Yes | Access scoping and audit review, like any PHI store |
Every row assumes the BAA is already accepted in AWS Artifact. No row is compliant without that step. For the terms to look for in the agreement, see what a hosting BAA should cover.
On log retention, HIPAA's audit controls standard (45 CFR § 164.312(b)) requires systems that record and examine activity. It sets no retention period for the logs themselves. The documentation rule is different (45 CFR § 164.316(b)(2)(i)). HIPAA requires you to keep Security Rule documentation for six years from when it was created or last in effect, whichever is later. Many organizations keep logs for six years to line up with that rule. Our guide to HIPAA audit logs covers what to record, how long to keep it, and who holds each log.
The questions teams actually ask
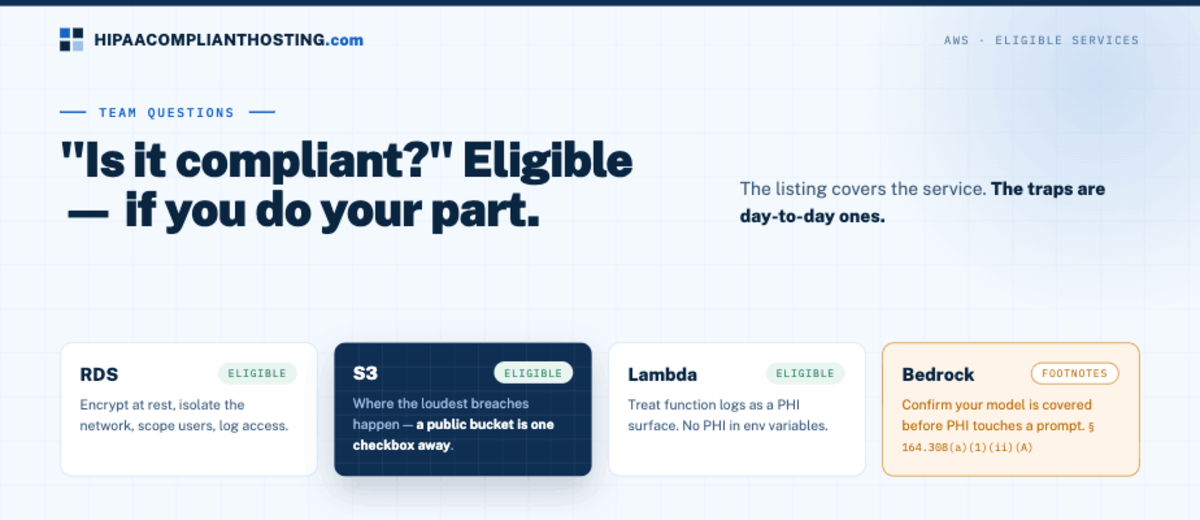
Is RDS HIPAA compliant? RDS is eligible, and so is Aurora. Turn on encryption at rest. Isolate the network. Scope the database users and log access. Then it can be part of a compliant system. The database tier has its own guide: HIPAA compliant database hosting. The RDS-specific verdict, engine by engine, is in is Amazon RDS HIPAA compliant.
Is Lambda HIPAA compliant? Lambda is eligible. The traps are day-to-day ones. PHI pasted into environment variables. PHI logged in plain text to CloudWatch. Treat function logs as a PHI surface. The full serverless checklist is in is AWS Lambda HIPAA compliant.
Is Bedrock HIPAA compliant? Amazon Bedrock is on the list with no bracketed limit, and so is Amazon Bedrock AgentCore. Retention is the detail to check. Bedrock lets you set a data retention mode. For some models, AWS keeps inputs and outputs for up to 30 days for abuse detection, and it does not share them with the model provider. AI workloads also belong in your risk analysis under 45 CFR § 164.308(a)(1)(ii)(A). The hosting around the model needs a BAA too, as our guide to HIPAA compliant AI hosting explains.
Is S3 HIPAA compliant? S3 is eligible. The risk to watch is a bucket someone opens to the public. New buckets block public access by default, but a policy change can still open one. Turn on S3 Block Public Access at the account level, since it overrides those policies. S3 has encrypted new uploads by default since January 5, 2023. Use AWS KMS keys if you want control over who can use the key, and alert on policy changes.
Eligible parts, compliant systems
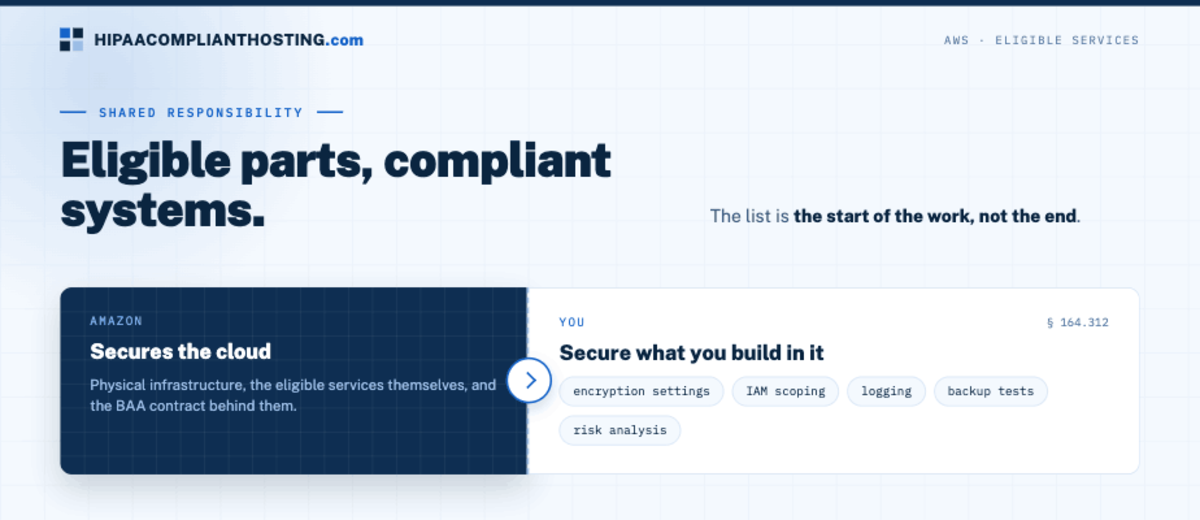
Amazon secures the cloud. You secure what you build in it. That is the shared responsibility model. It is why the AWS HIPAA eligible services list is the start of the work, not the end. Teams that sit a layer above AWS, on Heroku, Vercel, Render, or Supabase, face the same gate one level up. Which of those platforms will sign a BAA at all is covered in our guide to HIPAA compliant app hosting. Encryption settings, IAM scoping, and logging are on your side under 45 CFR § 164.312. So are backup tests and the risk analysis, under 45 CFR § 164.308. The full setup walkthrough is in our guide to what HIPAA compliant cloud hosting requires. Software teams that build on these services have their own checklist in HIPAA compliant hosting for healthcare SaaS.
If you would rather not run this yourself
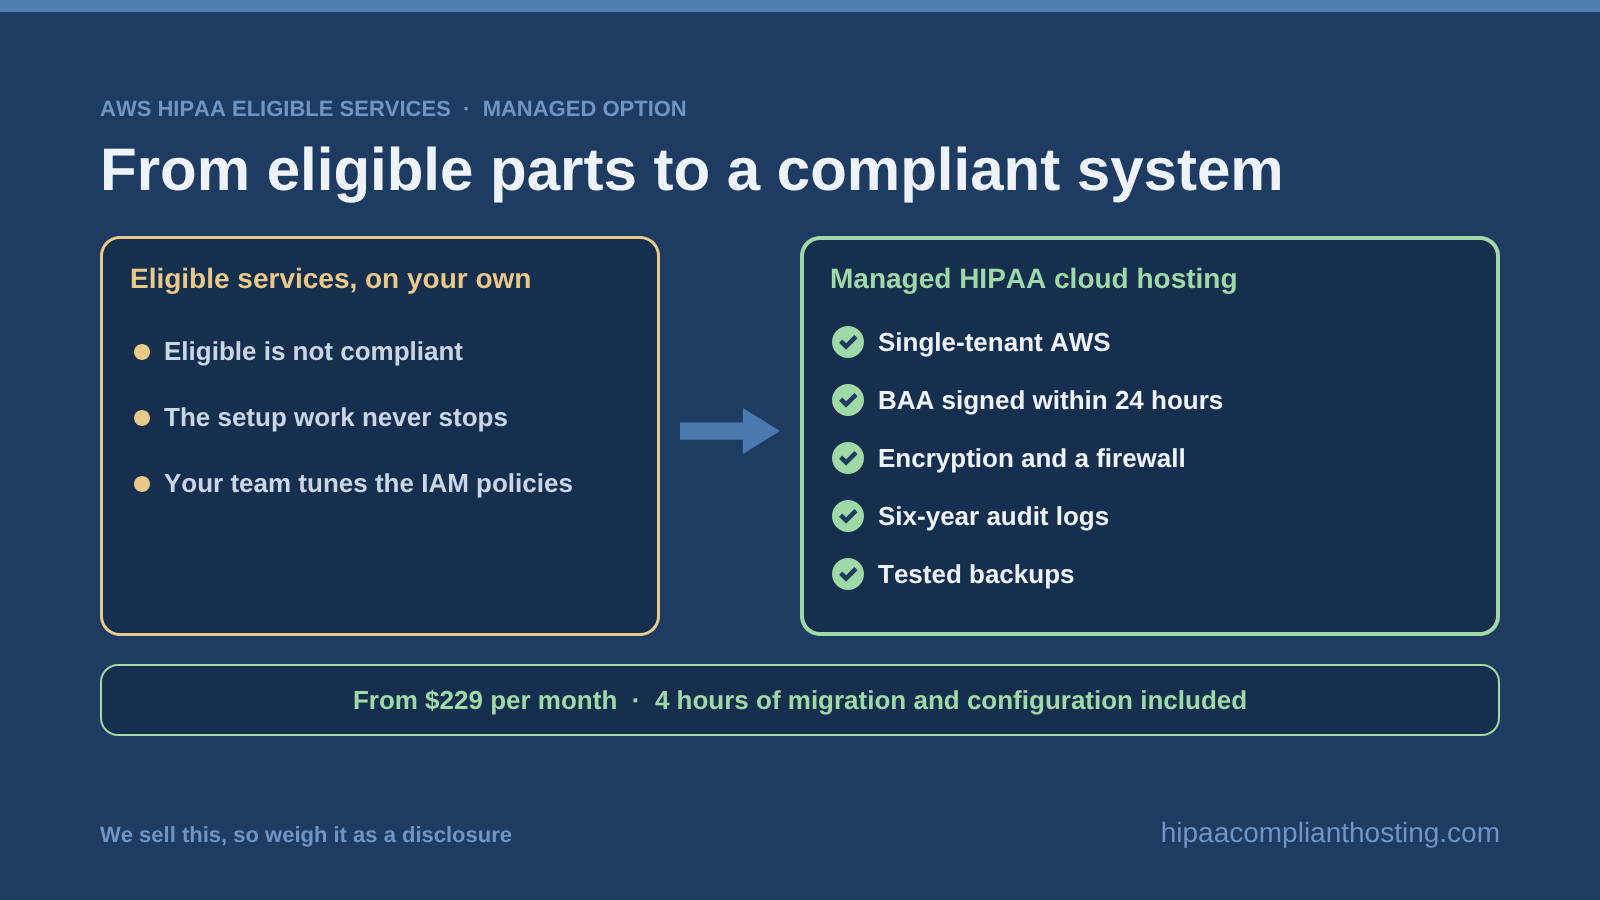
The gap between eligible and compliant is setup work, and it never stops. Maybe your team would rather ship product than tune IAM policies. Our managed HIPAA cloud hosting runs each plan on single-tenant AWS. Every plan includes CloudFront CDN, a web application firewall, and EBS storage with 7-day snapshot retention. The CDN and the storage run on Amazon CloudFront and Amazon EBS, and both are AWS HIPAA eligible services.
Encryption at rest and in transit, six-year audit logging, and tested encrypted backups are included too. We sign the BAA within 24 hours of signup, before patient data moves. Our BAA covers the servers and services we run. Your email, texting, EHR, and AI model vendors need their own BAAs.
Plans start at $229 a month. The Performance tier for n8n, Drupal, Strapi, Docker, and Phalcon starts at $259 a month. Monthly plans have no long-term contract. Your first month comes with 4 hours of migration and configuration included. After that, it is $175 an hour, quoted before work starts.
Know the limits before you choose. Each plan is one server in one AWS availability zone, and a multi-zone design is quoted separately. Root access comes only through an Enterprise engagement. We sell this, so weigh our view with that in mind. Either way, tell us what you are building and you will get a straight answer.
Frequently asked questions
How many AWS HIPAA eligible services are there?
AWS lists 174 HIPAA eligible services as of its October 15, 2026 update. AWS adds services based on customer demand, so the count changes. Check AWS's own page before you use a new service for PHI.
Is Amazon RDS HIPAA eligible?
Yes. The RDS entry covers six engines: SQL Server, MySQL, Oracle, PostgreSQL, Db2, and MariaDB. Amazon Aurora has its own entry. You still set up encryption, network isolation, scoped users, and logging before patient data arrives.
Is Amazon Bedrock HIPAA eligible?
Yes, with no bracketed limit on the list. Check the data retention mode, though. For some models, AWS keeps inputs and outputs for up to 30 days for abuse detection. If you set the mode to none, Bedrock blocks models that require retention. Note the AI workload in your risk analysis.
Is Amazon CloudFront HIPAA eligible?
Yes, with one exclusion. AWS excludes content delivery through CloudFront Embedded Points of Presence. Those sit inside internet provider networks, are opt-in, and are built for large-scale video streams and game downloads. Standard CloudFront delivery stays on the list of AWS HIPAA eligible services.
Does using only eligible services make my app HIPAA compliant?
No. AWS HIPAA eligible services plus a signed BAA are needed, not enough. Your settings, access choices, logging, and documented risk analysis decide compliance.
What happens if PHI lands in a non-eligible service?
That is a violation of 45 CFR § 164.308(b), even in a covered account. It may also be a reportable breach. Send PHI only through listed services, and audit where your data really flows.
Recap: AWS HIPAA eligible services
To recap, AWS HIPAA eligible services are the products the AWS BAA covers. AWS lists 174 of them as of its October 15, 2026 update. RDS, S3, EC2, Lambda, DynamoDB, and Bedrock are all on the list. About a dozen entries carry limits in brackets, such as CloudFront's Embedded Points of Presence exclusion. Sign the BAA in AWS Artifact first. Keep PHI inside listed services only. Then do your side of the work: encryption, access scoping, logging, and a written risk analysis. Eligible parts, set up right, are what a compliant system is made of.
This article is general information, not legal advice. The AWS HIPAA Eligible Services Reference changes frequently; the details here reflect the October 15, 2026 version. Confirm the current list with AWS, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
45 CFR § 164.308 (administrative safeguards, BAA requirement): ecfr.gov
45 CFR § 164.312 (technical safeguards): ecfr.gov
45 CFR § 164.316 (documentation, six-year retention): law.cornell.edu
AWS: Amazon Bedrock data retention and Amazon Bedrock abuse detection