


Is CakePHP HIPAA Compliant? CakePHP 5, the Authentication Plugin, and 2026 Settings
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-cakephp-hipaa-compliant
Last updated: October 22, 2026
CakePHP is not HIPAA compliant on its own, and no framework is. HIPAA regulates the organizations that handle patient data, not the code they use. A CakePHP app becomes part of a compliant system when a host signs a Business Associate Agreement (BAA). The app must also use CakePHP's security tools well, and your team must do the paperwork. So a CakePHP HIPAA compliant app is a question of layers and owners. CakePHP 5 gives you more built-in security than many PHP frameworks. It still has no two-factor login, no encrypted database column type, and no audit log. And CakePHP 4.x stopped getting security fixes on September 10, 2026. This guide covers what CakePHP gives you, what to add, and what to patch. CakePHP facts were checked against CakePHP's docs and GitHub on October 20, 2026, and PHP release facts against php.net on October 22, 2026.
TL;DR: Quick answer
CakePHP 5 includes CSRF protection in its app skeleton, a rate limit middleware added in 5.3, and AES-256 encryption with an HMAC checksum.
The first-party Authentication plugin hashes passwords with bcrypt and renews session IDs at login and logout. It documents no two-factor login.
CakePHP 4.x security support ended on September 10, 2026. CakePHP 5.2 through 5.4 are supported, and the latest release, 5.4.3, shipped on October 3, 2026. On older branches, run at least 5.3.7 or 5.2.15 to close two SQL injection flaws that GitHub's advisory database rates Critical.
A Critical advisory rated 10.0, CVE-2026-77337, hit the Authentication plugin's cookie login on August 21, 2026. Update the plugin and encrypt the cookie.
CakePHP has no official hosting product that we could find, so no CakePHP vendor signs a BAA. Your host must.
Is CakePHP HIPAA compliant? The three-layer answer
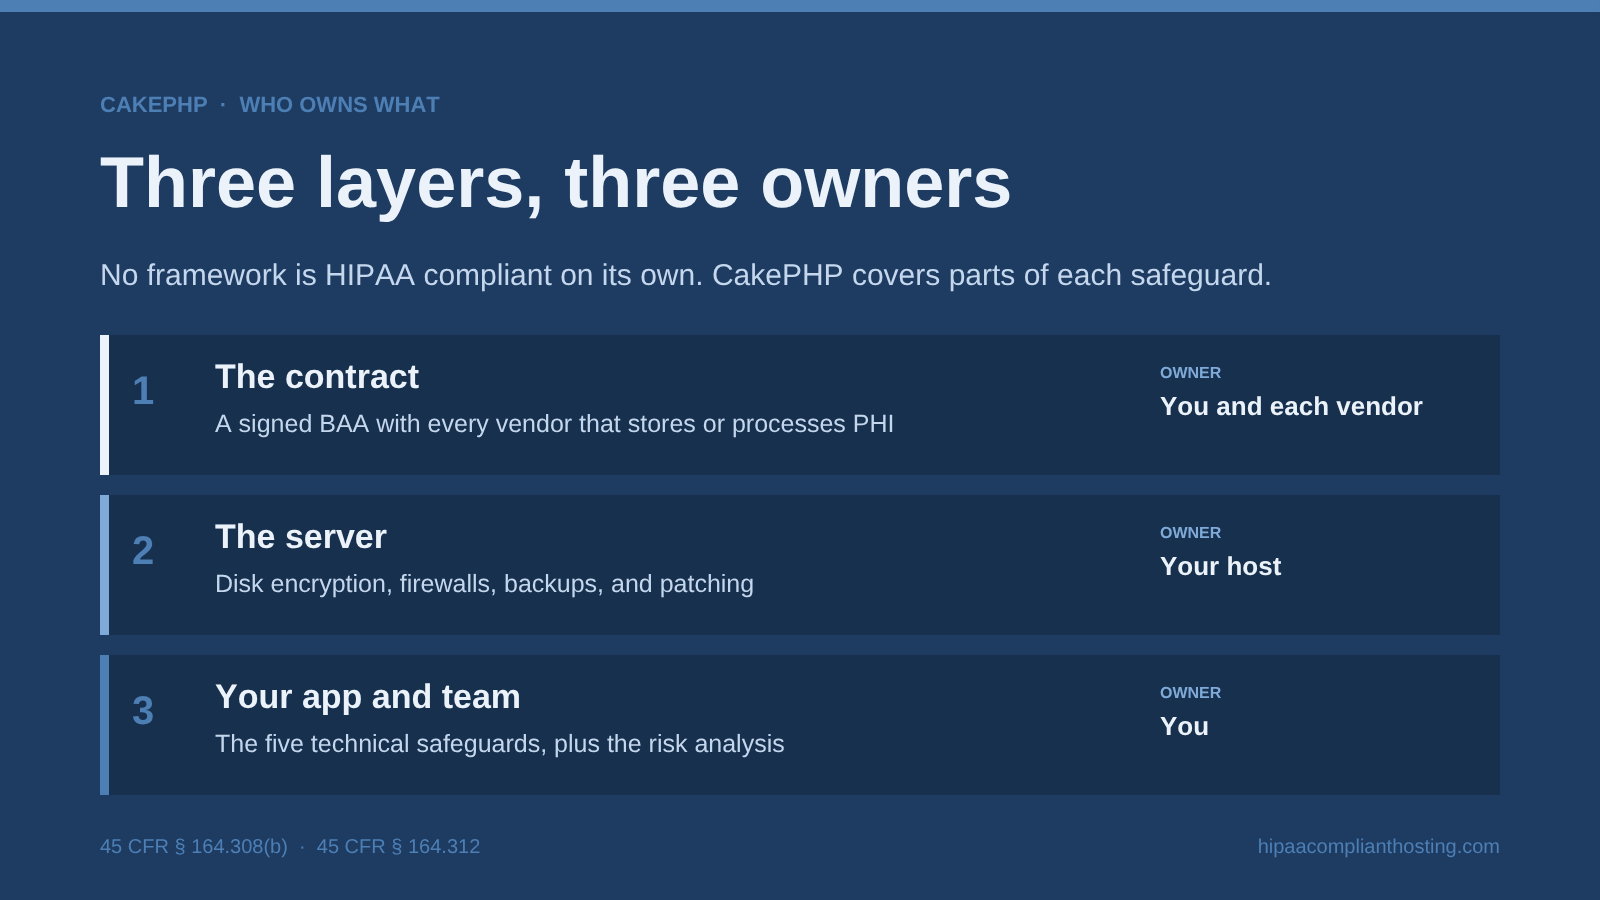
A CakePHP HIPAA compliant system has three layers, and each one needs an owner. The first is the contract. Any vendor that stores or processes protected health information (PHI) for a covered entity is a business associate under 45 CFR § 160.103. Under 45 CFR § 164.308(b), you need a signed BAA with that vendor first. Our HIPAA business associate agreement guide explains what it must cover. The second layer is the server: physical safeguards, disk encryption, firewalls, backups, and patching. Your host runs this layer or splits it with you, so get that split in writing. The third layer is your app and your team. The HIPAA Security Rule lists five technical safeguards in 45 CFR § 164.312. They are access control, audit controls, integrity, person or entity authentication, and transmission security. CakePHP covers parts of each, with plugins filling the gaps. Coverage is thinnest for audit controls, because CakePHP's general logging does not track who viewed or changed patient data. You also run a risk analysis under 45 CFR § 164.308(a)(1). If your patient portal has run on CakePHP for years, the CakePHP HIPAA compliant question usually starts with a version check.
What does CakePHP 5 give you for the HIPAA technical safeguards?
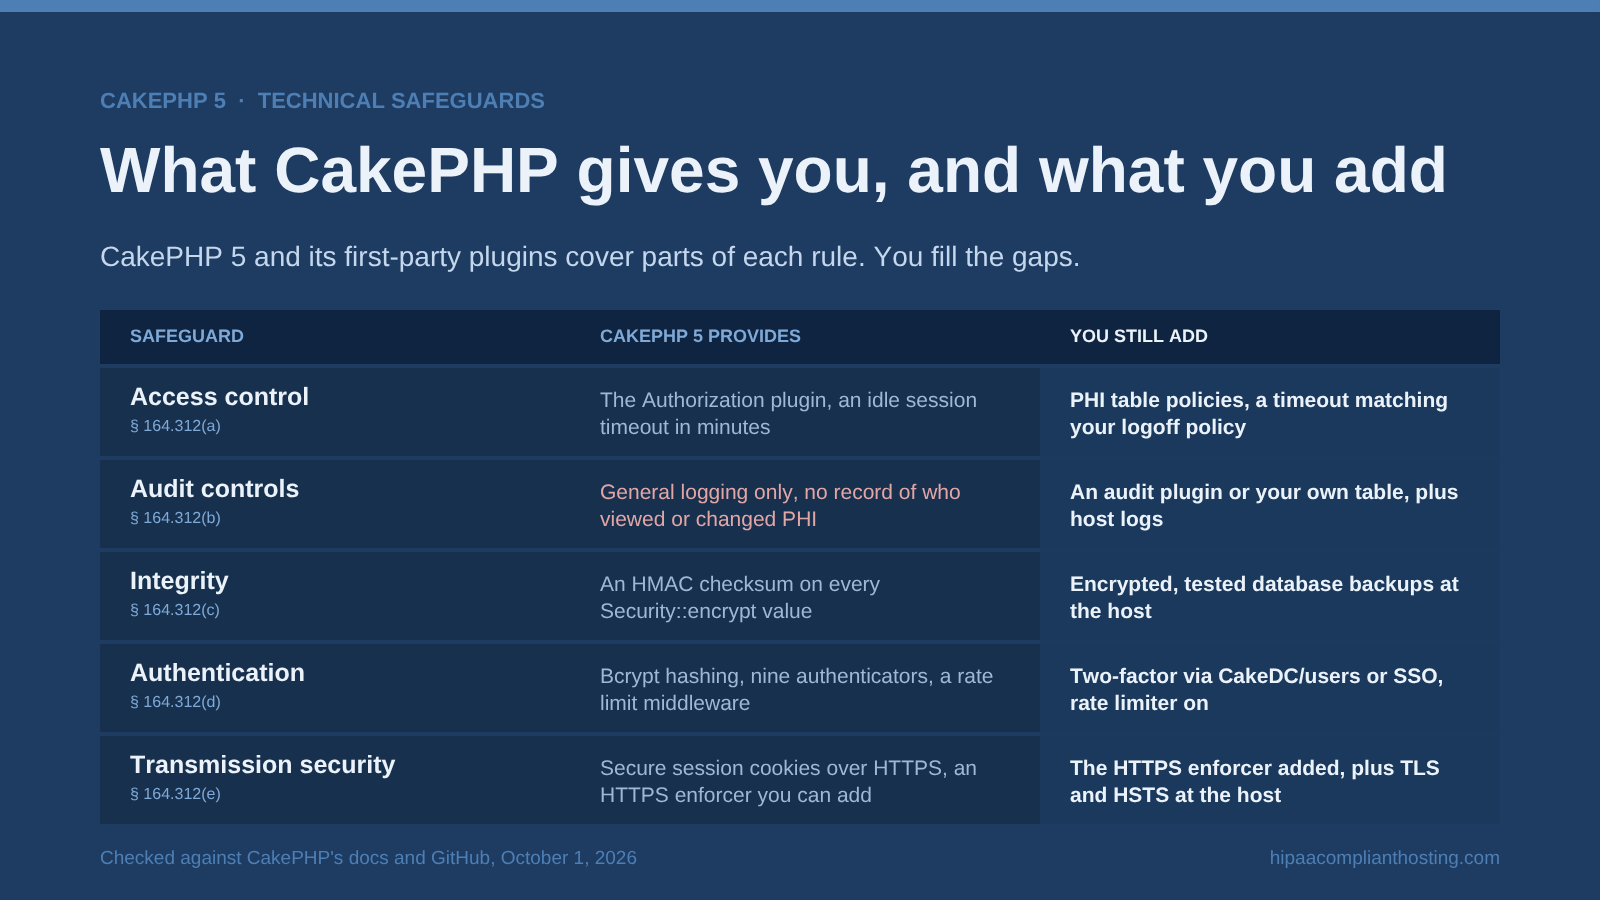
Here is how CakePHP 5 and its first-party plugins map to each rule in 45 CFR § 164.312. The last column is what a CakePHP HIPAA compliant app still needs from you or your host.
Safeguard (45 CFR § 164.312) | What CakePHP 5 provides | What you still add |
|---|---|---|
Access control, (a) | The Authorization plugin; an idle session timeout setting in minutes | Policies for every PHI table, and a timeout that matches your logoff policy |
Audit controls, (b) | General logging only; no record of who viewed or changed PHI | An audit plugin or your own table, plus server and database logs from the host |
Integrity, (c) | An HMAC checksum on every value encrypted with Security::encrypt | Encrypted, tested database backups at the host |
Person or entity authentication, (d) | Bcrypt password hashing with rehash on login; nine authenticators; a rate limit middleware | Two-factor login through CakeDC/users or SSO, and the rate limiter turned on |
Transmission security, (e) | Secure session cookies over HTTPS; SameSite set to Lax; an HTTPS enforcer middleware you can add | The HTTPS enforcer added, plus TLS and HSTS at the host |
Encryption needs care in any CakePHP HIPAA compliant build. CakePHP's Security::encrypt uses AES-256 and returns the result with an HMAC checksum. The docs say it should never be used for passwords, and passwords go through the bcrypt hasher instead. There is no encrypted column type in the ORM. So your code must encrypt each PHI field before saving and decrypt it after reading. That app-level work sits at the center of a CakePHP HIPAA compliant data model. Our glossary entry on access control covers the matching rule for who may read those fields. Laravel's Eloquent ORM, unlike CakePHP's, has encrypted casts that encrypt each marked field before saving. Those casts have limits, such as values you cannot search, and our guide to Laravel HIPAA compliant apps explains them.
Which CakePHP defaults need changing?
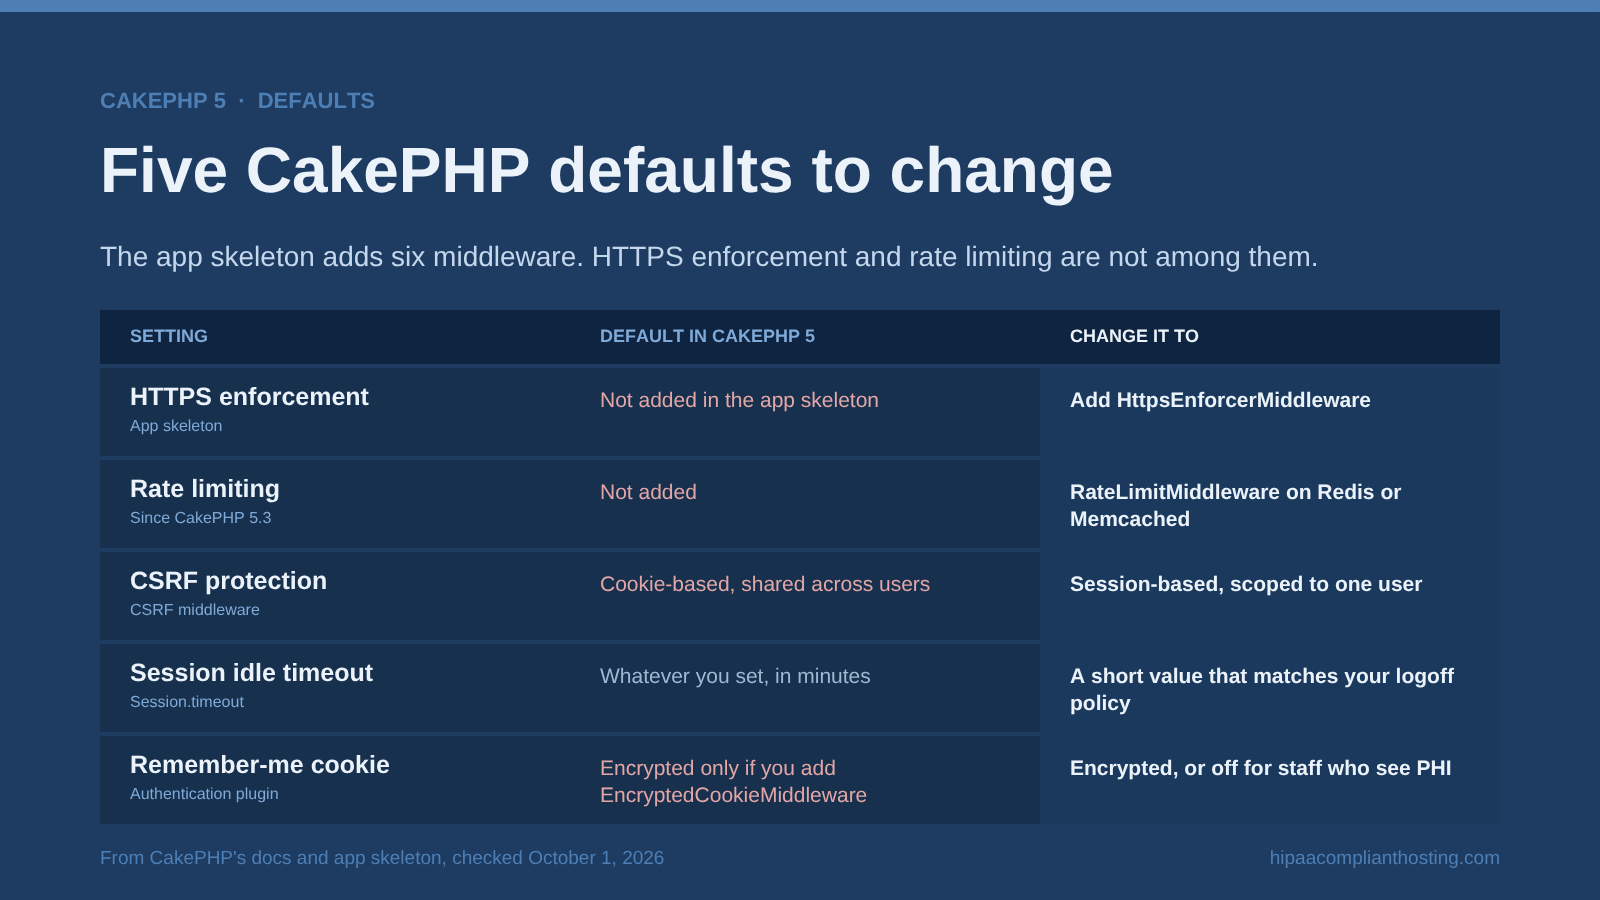
A handful, and each one is quick. The CakePHP 5 app skeleton adds six middleware out of the box. They are error handling, host header checks, assets, routing, body parsing, and cookie-based CSRF protection. HTTPS enforcement and rate limiting are not in that list. A CakePHP HIPAA compliant app needs both added.
Setting | Default in CakePHP 5 | Change it to |
|---|---|---|
HTTPS enforcement | Not added in the app skeleton | Add HttpsEnforcerMiddleware |
Rate limiting | Not added; available since CakePHP 5.3 | Add RateLimitMiddleware with a Redis or Memcached cache |
CSRF protection | Cookie-based, shared across users | Session-based, scoped to one user; use only one of the two |
Session idle timeout | Whatever Session.timeout you set, in minutes | A short value that matches your logoff policy |
Remember-me cookie | Encrypted only if you add EncryptedCookieMiddleware first | Encrypted, or turned off for staff who see PHI |
The last row matters most for CakePHP HIPAA compliant apps in 2026. The Critical advisory from August hit unencrypted cookie logins, as covered below. The session timeout row ties to the rule in HIPAA automatic logoff. And the rate limiter docs warn that the File cache engine is not recommended in production.
Which CakePHP versions are safe to run?
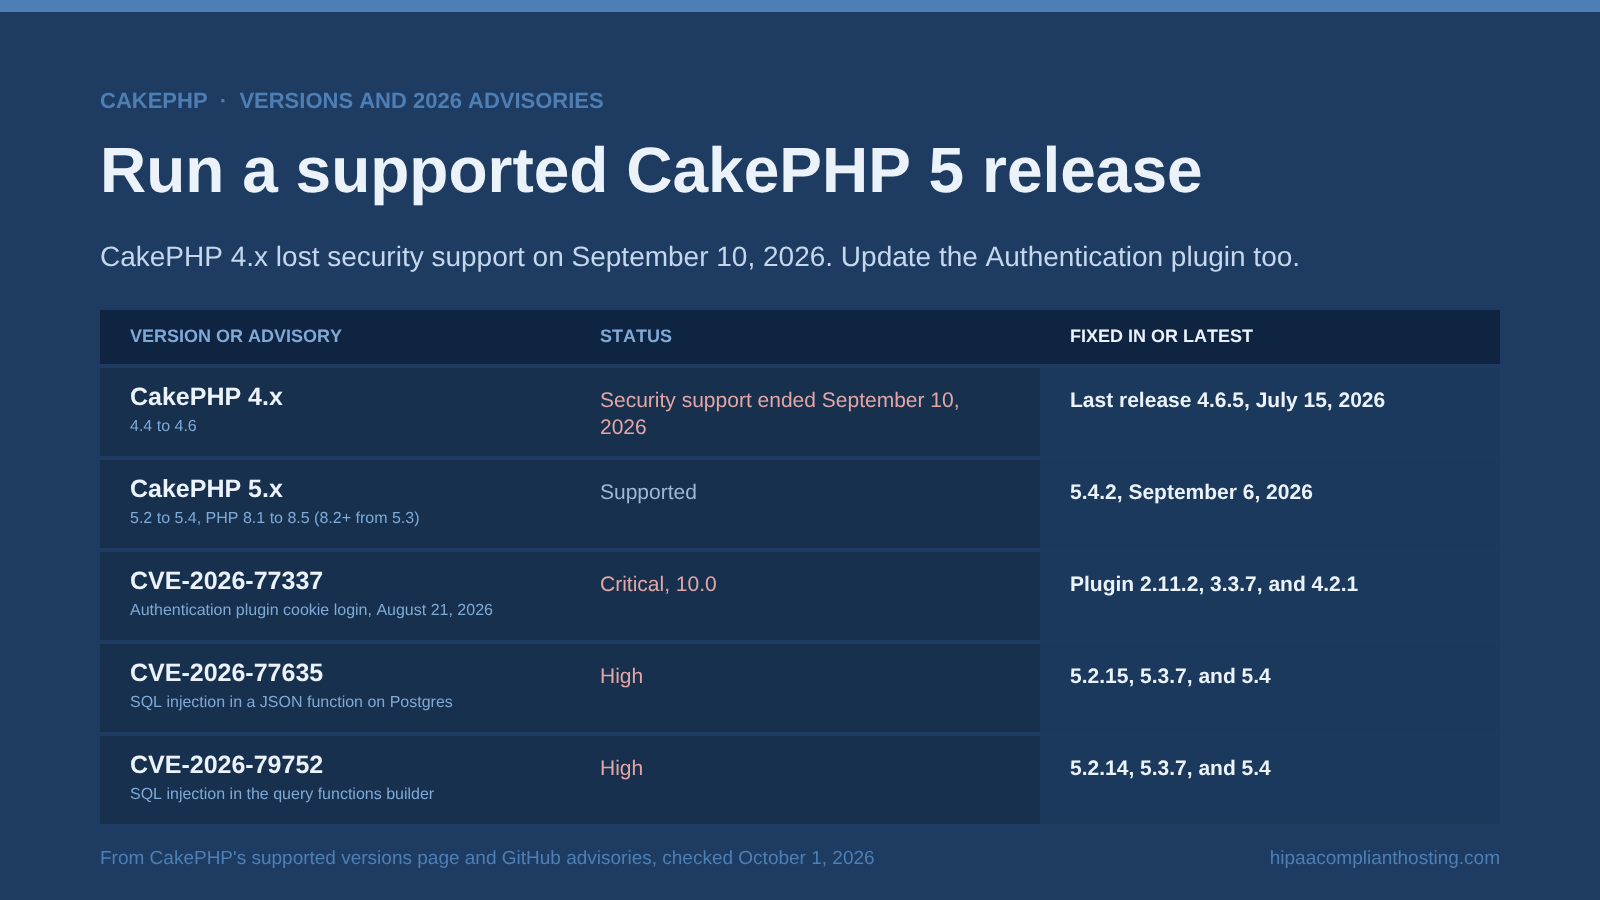
CakePHP 5.4.2 or later, or at least 5.3.7 on 5.3 or 5.2.15 on 5.2, with current plugins. CakePHP gives each major version 24 months of active support and 36 months of security support after the next major ships. CakePHP 5.0 shipped September 10, 2023. So CakePHP 4.x lost security support on September 10, 2026. A CakePHP HIPAA compliant app on 4.x now carries unpatched risk. Yii 2 apps have more time, since Yii 2.0.50 and later keep security fixes until November 23, 2027. Our Yii HIPAA compliant guide weighs staying on Yii 2 against moving to Yii 3.
Version | Status on October 20, 2026 | Latest release |
|---|---|---|
CakePHP 4.x (4.4 to 4.6) | Security support ended September 10, 2026 | 4.6.5, July 15, 2026 |
CakePHP 5.x (5.2 to 5.4) | Supported; PHP 8.1 to 8.5, with 8.2 or later on 5.3 and 5.4 | 5.4.3, October 3, 2026 |
The PHP runtime must also be on a patched release, because CakePHP and plugin updates do not cover flaws in PHP itself. On October 21, 2026, the PHP project released PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to fix two critical flaws, CVE-2026-109618 and CVE-2026-109619. The PHP project says both can allow unauthenticated remote code execution, and that updating is the only safe choice. According to php.net, PHP 8.1 and older no longer receive updates from the PHP project. If your CakePHP 5.2 app runs on PHP 8.1, move to 8.2 or later, or ask your distribution or LTS vendor about backported fixes. PHP 8.2 itself reaches end of life on December 31, 2026. Check which PHP version your server runs, and confirm in writing whether you or your host applies PHP updates.
August 2026 was busy for anyone running CakePHP HIPAA compliant apps. On August 21, the Authentication plugin disclosed CVE-2026-77337, rated Critical at 10.0. If the cookie login was not encrypted, attackers could bypass authentication with forged tokens. The plugin flaw is fixed in versions 2.11.2, 3.3.7, and 4.2.1. The same day, CVE-2026-77635 disclosed a SQL injection in a JSON function on Postgres. On August 27, CVE-2026-79752 disclosed more SQL injection in the query functions builder. CakePHP rated both High, and GitHub's advisory database now rates both Critical, at 9.2 on CVSS 4.0. Both core flaws are fixed in 5.3.7 and 5.2.15, and 5.4 shipped with the fixes. Record your versions and patch cadence in your HIPAA risk analysis.
The 8 settings that make a CakePHP app HIPAA-ready
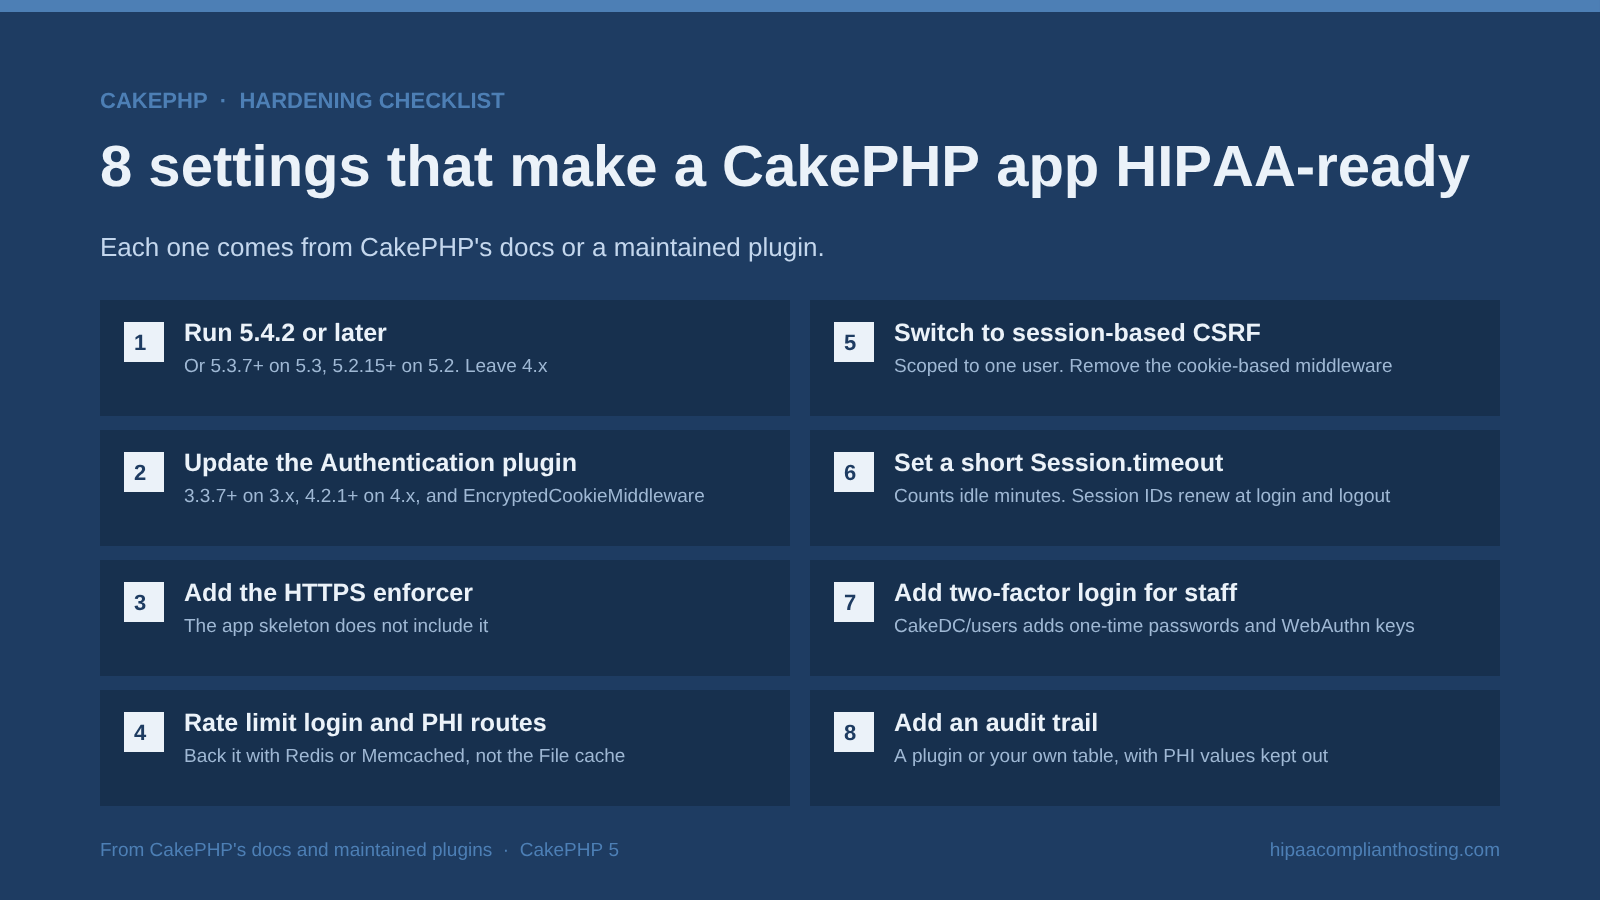
Start with these eight settings in any CakePHP HIPAA compliant review. Each one comes from CakePHP's docs or a maintained plugin.
Run CakePHP 5.4.2 or later. On an older branch, use 5.3.7 or later on 5.3, or 5.2.15 or later on 5.2. CakePHP 5.3 and 5.4 need PHP 8.2 or later. Run a patched PHP build too: at least 8.2.35, 8.3.36, 8.4.27, or 8.5.12 on your branch, or your Linux distribution's updated package. Leave 4.x, which no longer gets security fixes.
Update the Authentication plugin. Use plugin 3.3.7 or later on its 3.x line, or 4.2.1 or later on its 4.x line. Both plugin lines run on CakePHP 5. Add EncryptedCookieMiddleware before the Authentication middleware if you use cookie login.
Add the HTTPS enforcer. The app skeleton does not include it.
Add the rate limiter to login and PHI routes. The sliding window strategy is the default. Back it with Redis or Memcached, not the File cache.
Switch to session-based CSRF tokens. They are scoped to one user. Remove the cookie-based middleware, because the two cannot run together.
Set a short Session.timeout. It counts idle minutes. The Authentication plugin already renews the session ID at login and logout.
Add two-factor login for staff. CakeDC/users, with about 520 GitHub stars, adds one-time passwords and WebAuthn keys on CakePHP 5.3 and later. It requires the Authentication plugin's 3.x line, so pair it with 3.3.7 or later.
Add an audit trail. dereuromark/cakephp-audit-stash is one option, though it has only about 9 stars. Many teams write their own audit table. Keep PHI values out of it.
Item 7 ties to the rules in HIPAA MFA requirements. Item 8 maps to the audit controls rule, explained in our glossary entry on audit logging. With all eight in place, most CakePHP HIPAA compliant work inside the app is done.
Where do CakePHP apps leak PHI?
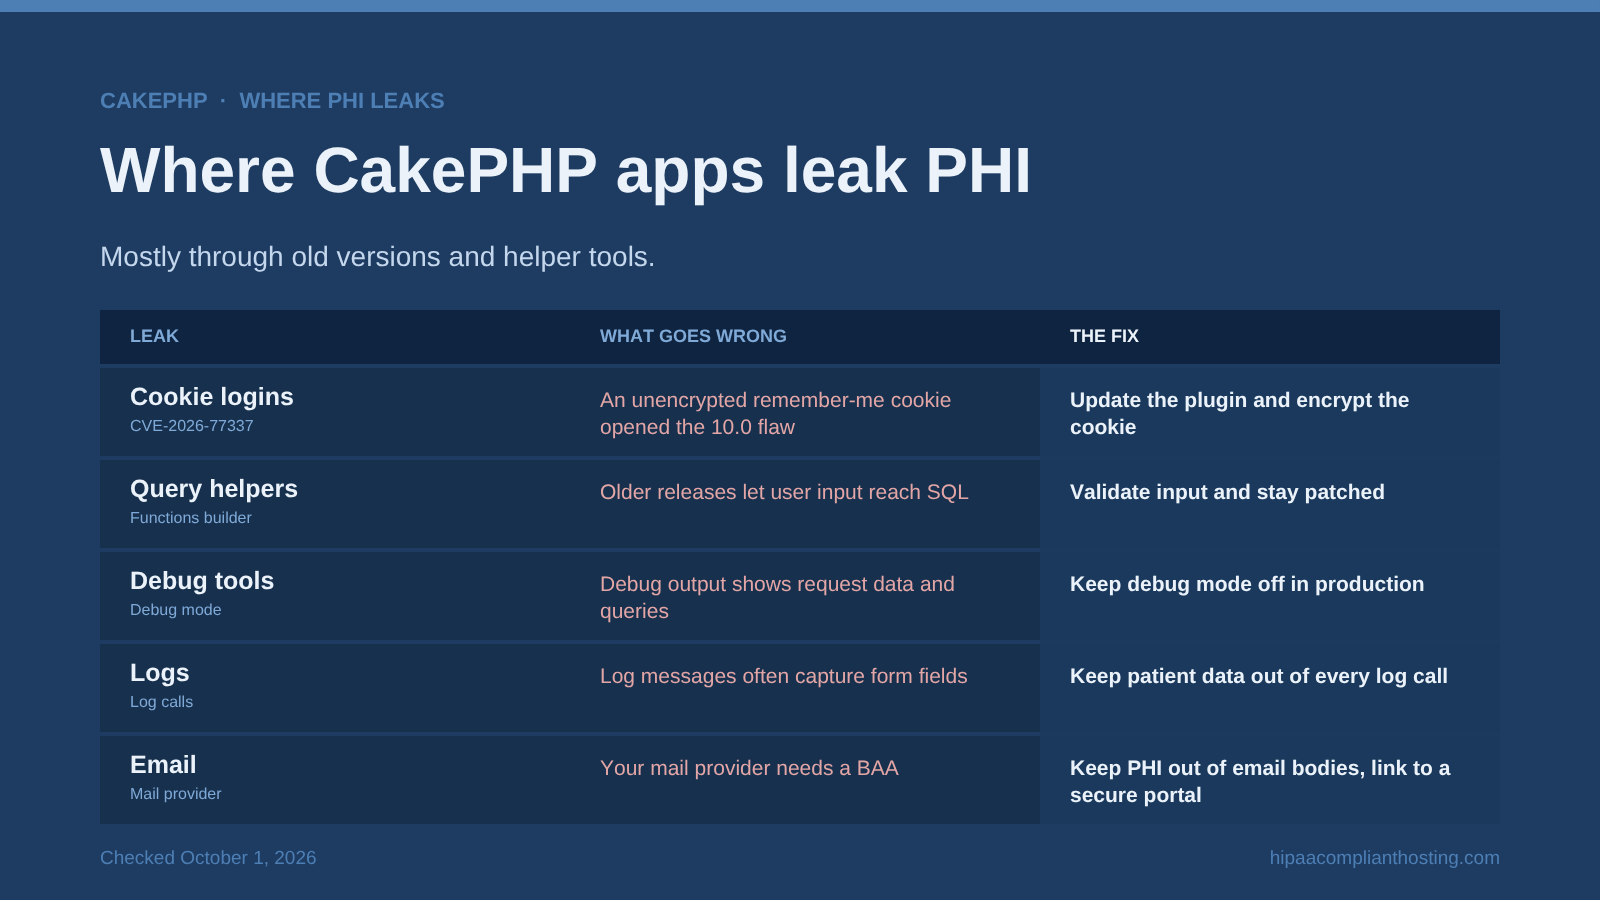
Mostly through old versions and helper tools. Check these five paths in any CakePHP HIPAA compliant review.
Cookie logins. An unencrypted remember-me cookie was the path for the 10.0 flaw in August 2026.
Query helpers. Older releases let user input reach SQL through the functions builder. Validate input and stay patched.
Debug tools. Debug output shows request data and queries. Keep debug mode off in production.
Logs. Log messages often capture form fields. Keep patient data out of every log call. Query logs splice bound values back into the SQL, so keep query logging off in production, as CakePHP's docs advise.
Email. Your mail provider needs a BAA. Keep PHI out of email bodies and link to a secure portal instead.
The developers who maintain these apps share this duty. The basics are in HIPAA training for web developers.
Who signs the BAA for a CakePHP app, and what does it cost?
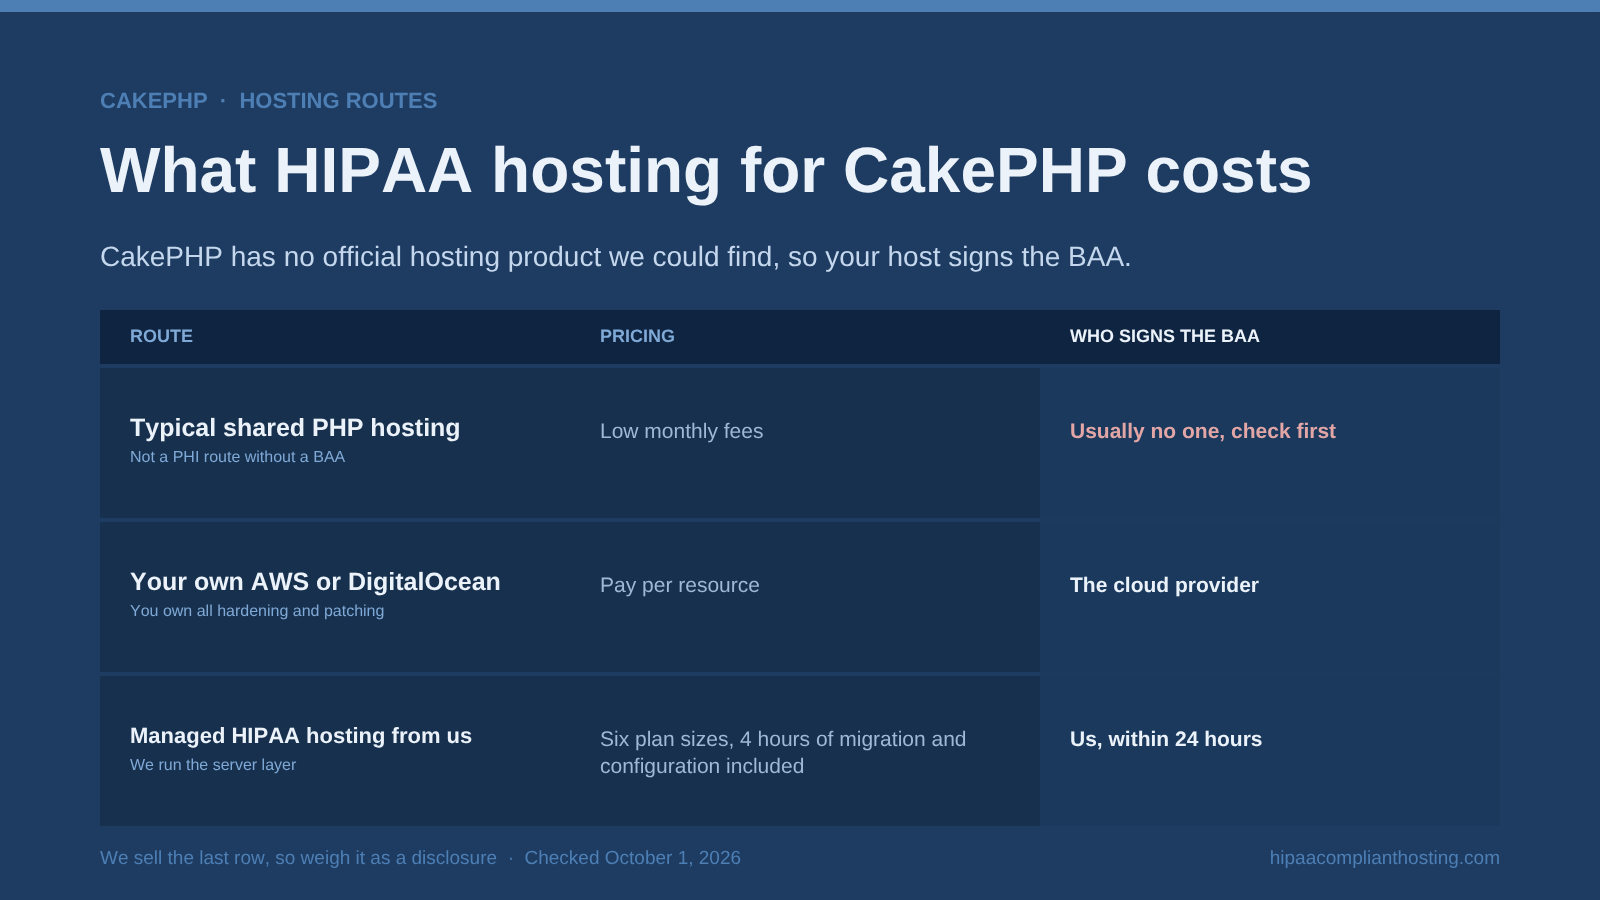
Your host does. CakePHP has no official hosting product that we could find, so no CakePHP vendor signs a BAA. A CakePHP HIPAA compliant budget starts with a host that will. As of October 20, 2026, AWS signs its BAA in AWS Artifact, and DigitalOcean signs one on request through its sales or support team. The full platform list is in HIPAA compliant app hosting. A cloud BAA covers the provider's infrastructure, not the server you configure or the code you run on it. That split is called the shared responsibility model, and the last column below lists your side.
Route | Pricing | Who signs the BAA | What you still own |
|---|---|---|---|
Typical shared PHP hosting | Low monthly fees | Usually no one; check first | Not a PHI route without a BAA |
Your own AWS or DigitalOcean server | Pay per resource | The cloud provider | All hardening, PHP and database patching, logs, backups, and the engineer's hours |
Managed HIPAA hosting from us | From $229 per month in six plan sizes, month to month with no long-term contract; 4 hours of migration and configuration included, then $175 an hour, quoted before work starts | Us, within 24 hours | App settings, plugin updates, risk analysis, other vendors' BAAs, and any task our scope of support page leaves to you |
We sell the last row, so weigh it as a disclosure. Of the two routes that come with a BAA, your own server can look cheaper until you add the engineer's hours it needs each month. Your database needs the same care, as covered in HIPAA compliant database hosting.
If you would rather not run the server layer yourself
Your team may want to spend its time on the portal, not on servers. Our HIPAA compliant CakePHP hosting runs your app on single-tenant AWS servers we manage. Every plan includes a web application firewall, the CloudFront CDN, and encryption at rest and in transit. It also includes six-year audit logging, tested encrypted backups, and EBS storage with 7-day snapshot retention. You keep CakePHP, your code, and your plugin updates. The BAA is signed within 24 hours of signup, before any patient data moves to us. It covers the servers and services we run. Outside services that receive patient data, such as a mail relay or an SMS provider, need their own BAAs. Plans start from $229 per month in six sizes, from Starter to Network, and run month to month with no long-term contract. You get 4 hours of migration and configuration included in the first month, then $175 an hour, quoted before work starts. Our CakePHP hosting page lists current prices, and our 8-step migration plan covers the move. If you have containerized the app, we also run HIPAA compliant Docker hosting on our Performance tier, from $259 a month. We sell both services, so weigh this section as a disclosure.
Here is the honest inverse. If your CakePHP app never stores or sends PHI for a covered entity, HIPAA does not apply, and you do not need us. If your team runs AWS under AWS's BAA with an engineer who owns patching and logs, that works. It can cost less if that engineer's time is already paid for. And if your app is still on CakePHP 4.x, new hosting alone will not fix it; plan the upgrade too. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your app does and get a straight answer.
Frequently asked questions
Is CakePHP HIPAA compliant?
No framework is HIPAA compliant by itself. A CakePHP HIPAA compliant app needs a host that signs a BAA. It also needs HTTPS enforcement, rate limiting, session CSRF tokens, two-factor login, encrypted PHI fields, and an audit trail. CakePHP 5 provides some of these, and plugins add the rest.
Is CakePHP 4 end of life?
Yes, for security fixes. CakePHP's supported versions page lists September 10, 2026 as the end of security support for 4.x. Its last release was 4.6.5, on July 15, 2026. Move PHI apps to a supported CakePHP 5 release.
Does CakePHP support two-factor authentication?
Not in core or the Authentication plugin docs. The CakeDC/users plugin adds one-time password two-factor login and WebAuthn keys such as YubiKeys. Its current branch supports CakePHP 5.3 and later. SSO with multi-factor login is another option.
Does CakePHP have an audit log?
No. CakePHP has general logging but no record of who viewed or changed PHI. Community plugins such as dereuromark/cakephp-audit-stash exist but are small. Many teams build an audit table and pair it with host-level logs. Our guide to HIPAA audit logs covers what to record and how long to keep it.
Which versions fix the August 2026 CakePHP advisories?
The Authentication plugin's Critical cookie flaw is fixed in 2.11.2, 3.3.7, and 4.2.1. The core SQL injection flaws are fixed in CakePHP 5.3.7 and 5.2.15, and 5.4 shipped with the fixes. CakePHP 5.4.3, released October 3, 2026, is the latest release as of October 20, 2026.
Recap: CakePHP HIPAA compliant
To recap, a CakePHP HIPAA compliant app needs a host that signs a BAA, a hardened server, and a configured app. CakePHP 5 gives you CSRF protection, a rate limiter, AES-256 encryption helpers, bcrypt hashing, and session renewal at login. You add the HTTPS enforcer, the rate limiter, session CSRF tokens, two-factor login, field encryption, and an audit trail. Leave CakePHP 4.x, update the Authentication plugin, encrypt cookie logins, and keep PHI out of logs and email.
This article is general information, not legal advice. Versions, defaults, and support dates change often. The details here reflect CakePHP's documentation, its GitHub repositories and advisories, and the CakeDC/users plugin as read on October 20, 2026. Hosting details were checked the same day. PHP release details reflect php.net as read on October 22, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
CakePHP: Supported versions and Release tags.
CakePHP docs: Security utility, CSRF protection, Sessions, Rate limit middleware.
CakePHP Authentication plugin: Authenticators and Password hashers.
CakePHP app skeleton: Default middleware.
GitHub advisories: CVE-2026-77337, CVE-2026-79752, and CVE-2026-77635.
GitHub Advisory Database ratings: CVE-2026-77635 and CVE-2026-79752.
PHP: October 21, 2026 security advisory and PHP 8.2.35 release announcement.
Yii: Release cycle.
Cloud BAAs: AWS HIPAA compliance and DigitalOcean HIPAA.
Plugins: CakeDC/users and dereuromark/cakephp-audit-stash.
45 CFR § 164.312 (technical safeguards): law.cornell.edu.
45 CFR § 164.308 (administrative safeguards, BAA requirement): ecfr.gov.
45 CFR § 160.103 (definitions): ecfr.gov.