


Is Laravel HIPAA Compliant? Laravel Cloud's BAA, Encrypted Casts, and the 8 Settings (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-laravel-hipaa-compliant
Last updated: October 22, 2026
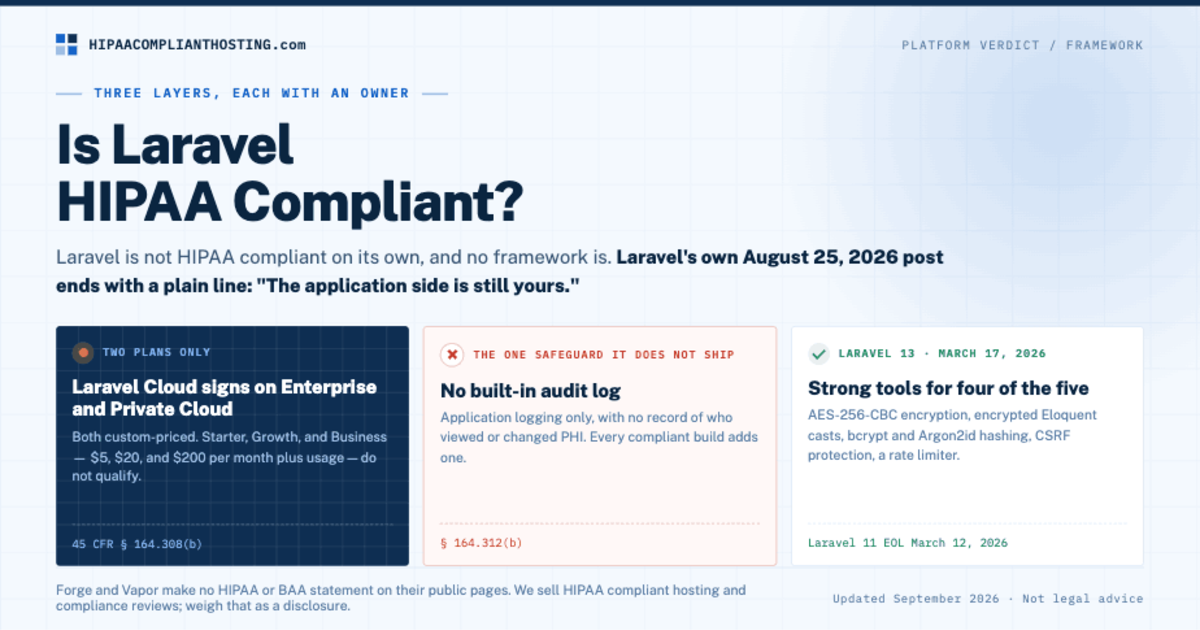
Laravel is not HIPAA compliant on its own, and no framework is. HIPAA regulates the organizations that handle patient data, not the code they write. A Laravel app becomes part of a compliant system when three things hold. A host signs a Business Associate Agreement (BAA). The app uses Laravel's security features correctly. And your team does the required paperwork. So the real question behind "is Laravel HIPAA compliant" is who owns each layer. Laravel's own team says the same thing. Its August 25, 2026 post on Private Cloud says it plainly: "The application side is still yours." This guide covers both sides. Every plan, price, and setting below was checked against Laravel's docs and pricing pages on October 20, 2026.
TL;DR: Quick answer
Laravel 13, released March 17, 2026, ships AES-256-CBC encryption, encrypted Eloquent casts, bcrypt and Argon2id hashing, CSRF protection, and a rate limiter. It has no built-in audit log, which every Laravel HIPAA compliant app needs.
Laravel Cloud supports HIPAA only on its Enterprise and Private Cloud plans, through a signed BAA. Enterprise is custom-priced, and Private Cloud starts at a platform fee of about $2,500 per month plus compute and database. Starter, Growth, and Business ($5, $20, and $200 per month plus usage) do not qualify.
Laravel Forge and Laravel Vapor make no HIPAA or BAA statement on their public pages as of October 20, 2026. Vapor no longer accepts new signups.
Laravel Fortify adds TOTP two-factor authentication and passkeys. Laravel Sanctum API tokens never expire unless you set an expiration.
Laravel 11 reached end of life on March 12, 2026. Laravel 12 gets security fixes only, until February 24, 2027. Versions 13.30.0 and 12.69.0 or later include every fix in Laravel's published framework advisories as of October 20, 2026. Also run at least the October 21, 2026 PHP security release for your branch: 8.2.35, 8.3.36, 8.4.27, or 8.5.12.
Our HIPAA compliant Laravel hosting runs the server layer for you from $229 a month, with a BAA signed within 24 hours of signup. We sell it, so weigh it as a disclosure.
Is Laravel HIPAA compliant? The three-layer answer
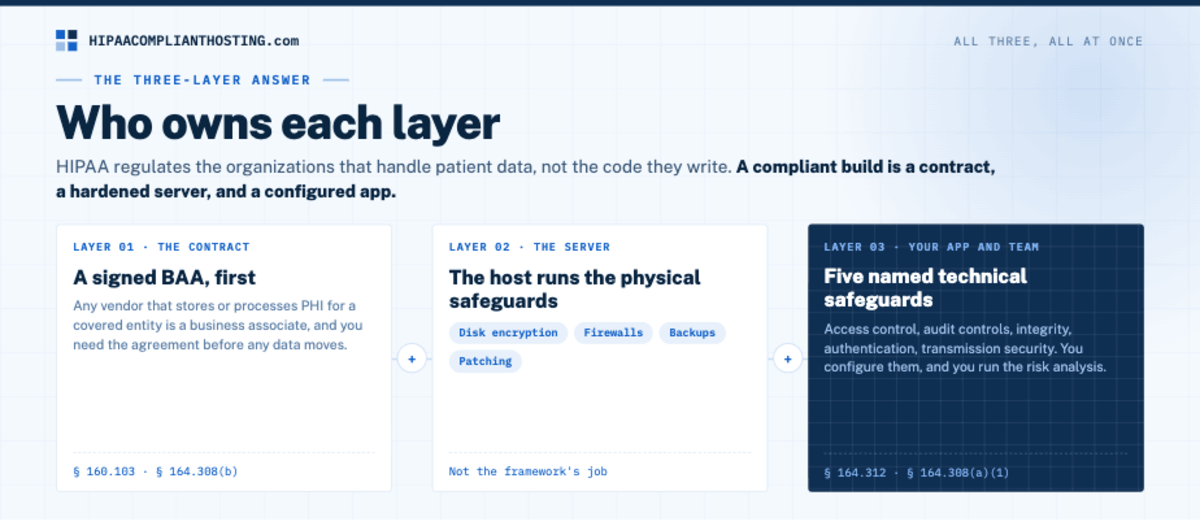
A Laravel HIPAA compliant system has three layers, and each one needs an owner. The first layer is the contract. Any vendor that stores or processes protected health information (PHI) for a covered entity is a business associate under 45 CFR § 160.103. Under 45 CFR § 164.308(b), you need a signed BAA with that vendor first. Our HIPAA business associate agreement guide explains what that contract must say. The second layer is the server, run by your host or your own team. It covers the physical safeguards, disk encryption, firewalls, and backups. Who patches the operating system depends on the plan, so get it in writing. The third layer is your app and your team. The HIPAA Security Rule names five technical safeguards in 45 CFR § 164.312: access control, audit controls, integrity, person or entity authentication, and transmission security. Laravel gives you strong tools for four of the five. You still configure them, and you still run a risk analysis under 45 CFR § 164.308(a)(1). If you sell software to clinics, the full chain of duties is in HIPAA compliant hosting for healthcare SaaS. The short version is simple. A Laravel HIPAA compliant build is a contract, a hardened server, and a configured app, all at once.
What does Laravel give you for the HIPAA technical safeguards?
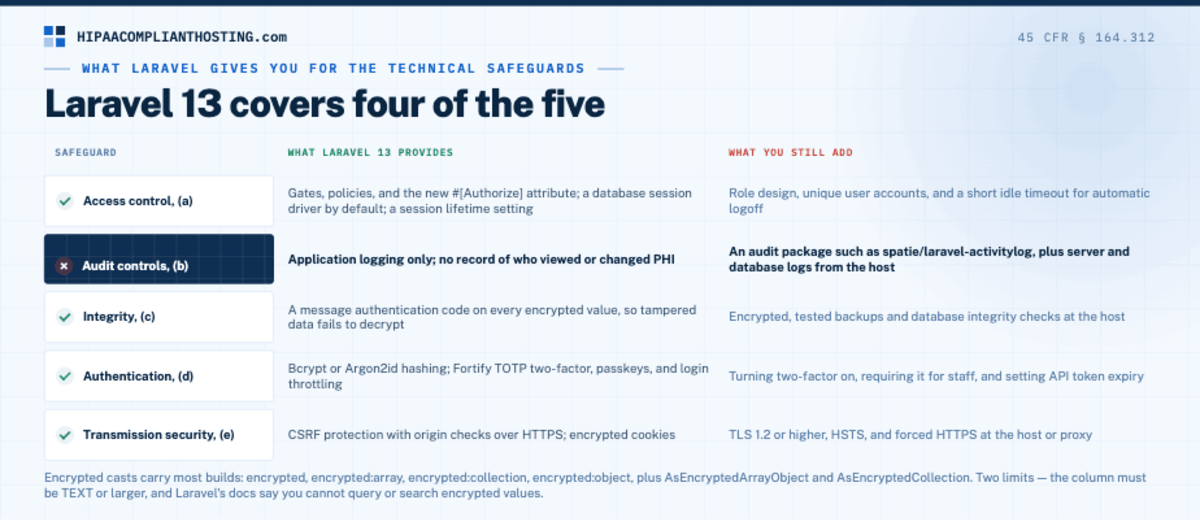
Here is how Laravel 13 maps to each rule in 45 CFR § 164.312. The middle column is what ships in the framework or its first-party packages. The last column is what a Laravel HIPAA compliant app still needs from you or your host.
Safeguard (45 CFR § 164.312) | What Laravel 13 provides | What you still add |
|---|---|---|
Access control, (a) | Gates, policies, and the new #[Authorize] attribute; a database session driver by default; a session lifetime setting | Role design, unique user accounts, and a short idle timeout for automatic logoff |
Audit controls, (b) | Application logging only; no record of who viewed or changed PHI | An audit package such as spatie/laravel-activitylog, plus server and database logs from the host |
Integrity, (c) | A message authentication code on every encrypted value, so tampered data fails to decrypt | Encrypted, tested backups and database integrity checks at the host |
Person or entity authentication, (d) | Bcrypt or Argon2id hashing; Fortify TOTP two-factor, passkeys, and login throttling | Turning two-factor on, requiring it for staff, and setting API token expiry |
Transmission security, (e) | CSRF protection with origin checks over HTTPS; encrypted cookies | TLS 1.2 or higher, HSTS, and forced HTTPS at the host or proxy |
Encrypted casts are the feature most Laravel HIPAA compliant apps lean on. Laravel offers the encrypted, encrypted:array, encrypted:collection, and encrypted:object casts, plus AsEncryptedArrayObject and AsEncryptedCollection. Each one encrypts the attribute with your APP_KEY before it reaches the database. That is app-level encryption at rest and in transit on top of the host's disk encryption. Two limits come with it. The column must be TEXT or larger. And Laravel's docs say you cannot query or search encrypted values. So plan your search fields before you encrypt a patient table. That one design choice decides how Laravel HIPAA compliant data models look in practice. CakePHP's ORM has no equivalent to Laravel's encrypted casts. In a CakePHP HIPAA compliant app, your code encrypts each PHI field with Security::encrypt before saving and decrypts it after reading.
Does Laravel Cloud sign a BAA?
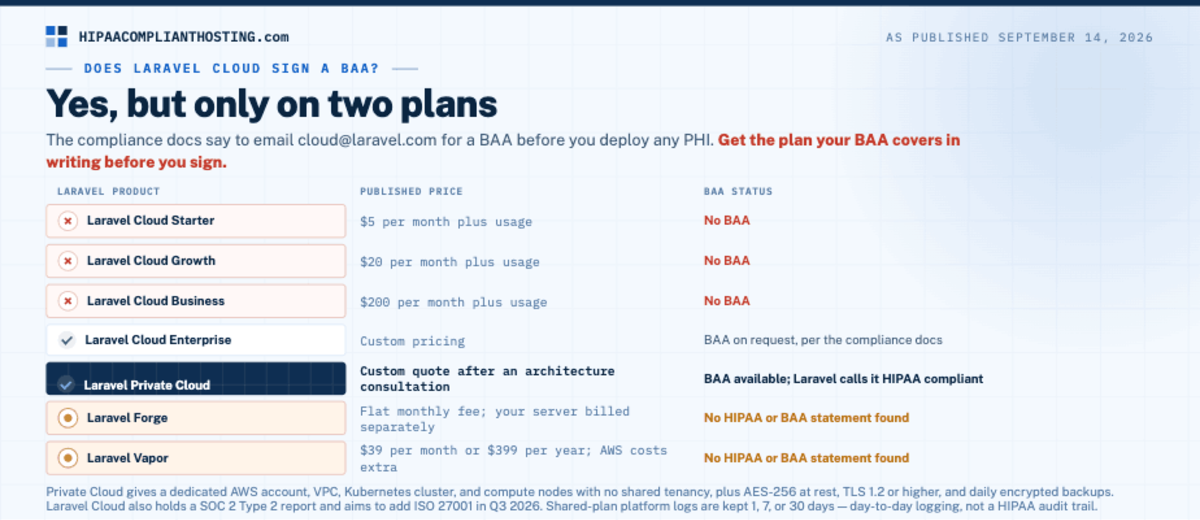
Yes, but only on two plans. For most teams, that is the first Laravel HIPAA compliant decision. Laravel's compliance docs say Laravel Cloud supports HIPAA for customers on its Enterprise and Private Cloud plans, through a signed BAA. The docs tell you to email [email protected] for a BAA before you deploy any PHI. Laravel's August 25, 2026 blog post is narrower. It says the HIPAA coverage is for Private Cloud customers, not shared plans such as Starter or Growth. Get the plan your BAA covers in writing before you sign. Here is the Laravel product line as published on October 20, 2026.
Laravel product | Published price | BAA status |
|---|---|---|
Laravel Cloud Starter | $5 per month plus usage | No BAA |
Laravel Cloud Growth | $20 per month plus usage | No BAA |
Laravel Cloud Business | $200 per month plus usage | No BAA |
Laravel Cloud Enterprise | Custom pricing | BAA on request, per the compliance docs |
Laravel Private Cloud | Platform fee from about $2,500 per month, plus compute and a managed database; custom quote after an architecture consultation | BAA available; Laravel calls it HIPAA compliant |
Laravel Forge | Flat monthly fee; your server is billed separately | No HIPAA or BAA statement found |
Laravel Vapor | $39 per month or $399 per year; AWS costs extra | No HIPAA or BAA statement found; closed to new signups |
Private Cloud is a serious product. It gives you a dedicated AWS account, VPC, Kubernetes cluster, and compute nodes, with no shared tenancy. For a team that wants Laravel HIPAA compliant hosting from the framework's own company, it is the direct route. Laravel lists AES-256 encryption at rest, TLS 1.2 or higher in transit, and daily encrypted backups. Laravel Cloud also holds a SOC 2 Type 2 attestation. Its compliance page now says it has achieved ISO 27001 certification. The shared plans are a different story. Their platform logs are kept for 1, 7, or 30 days depending on plan. That is day-to-day logging, not the audit logging HIPAA requires.
Forge and Vapor work differently. Forge manages servers you own on a provider you pick, so the BAA that matters comes from that provider. A Laravel HIPAA compliant setup on Forge starts with that contract. Ask counsel whether Forge's own server access needs a BAA too. Forge also offers Laravel VPS, its own server option. Forge's pages make no HIPAA or BAA statement for it, so keep PHI off it unless Laravel signs a BAA. Vapor runs your app on AWS Lambda in an AWS account you pay for. As of October 20, 2026, Vapor no longer accepts new signups, and Laravel points teams to Laravel Cloud instead. For PHI, that means the Enterprise or Private Cloud plan. For existing Vapor apps, Lambda is on AWS's eligible list. The settings are in our guide to whether AWS Lambda HIPAA compliant setups are possible. One more Laravel product needs a warning. Laravel Nightwatch's terms, effective June 16, 2025, bar sending PHI or HIPAA-covered data to the service without Laravel's prior written approval.
Which Laravel versions are still safe for PHI?
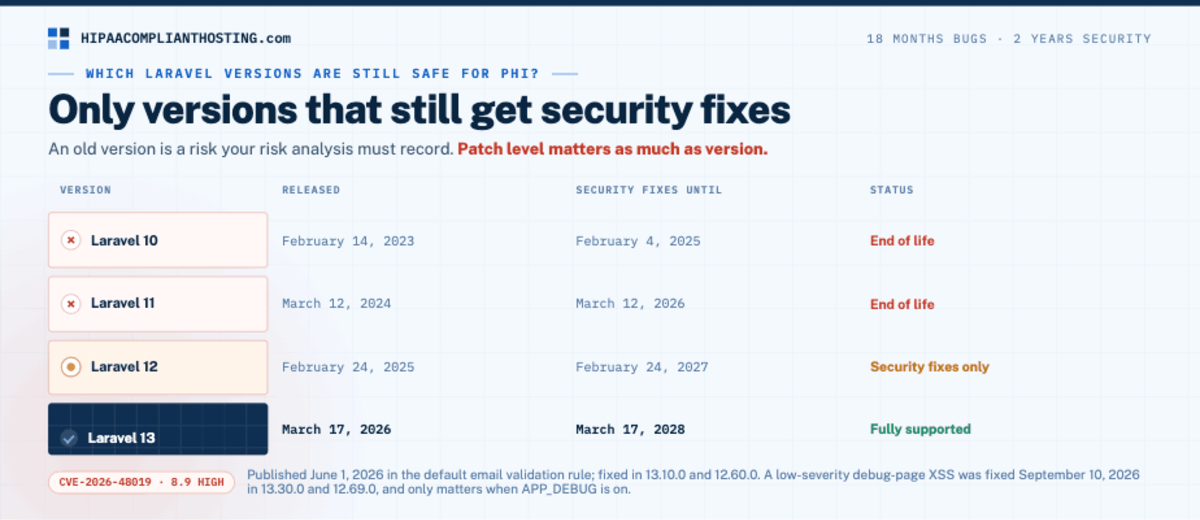
Only versions that still get security fixes. An unsupported version cannot stay part of a Laravel HIPAA compliant system for long. Laravel gives every major release 18 months of bug fixes and 2 years of security fixes. An old version is a risk your risk analysis must record. Here is the official support table as of October 20, 2026.
Version | Released | Security fixes until | Status |
|---|---|---|---|
Laravel 10 | February 14, 2023 | February 4, 2025 | End of life |
Laravel 11 | March 12, 2024 | March 12, 2026 | End of life |
Laravel 12 | February 24, 2025 | February 24, 2027 | Security fixes only |
Laravel 13 | March 17, 2026 | March 17, 2028 | Fully supported |
Patch level matters as much as version. On June 1, 2026, Laravel published a High-severity flaw in the default email validation rule, CVE-2026-48019, rated 8.9. It is fixed in Laravel 13.10.0 and 12.60.0. On September 10, 2026, a low-severity XSS in the debug page was fixed in 13.30.0 and 12.69.0. That one only matters when APP_DEBUG is on. On October 19, 2026, Laravel disclosed a Critical flaw in its built-in token API guard, CVE-2026-114509, rated 9.2. On some MySQL or MariaDB setups, an attacker could sign in as any existing user without that user's API token. The fix shipped in 13.29.0 and 12.68.0. As of October 20, 2026, versions 13.30.0 and 12.69.0 or later include every fix in Laravel's published framework advisories. Write your version and patch cadence into your HIPAA risk analysis. Keeping a Laravel HIPAA compliant app patched is a monthly job, not a launch task.
PHP itself needs patching too. On October 21, 2026, PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 fixed two critical flaws, CVE-2026-109618 and CVE-2026-109619, that can allow unauthenticated remote code execution. Confirm that each server running your app has at least the fixed release for its branch, or a vendor package with the fixes. For example, a server on PHP 8.3 needs 8.3.36 or a later 8.3 release. PHP 8.1 and older no longer receive updates from the PHP project. PHP 8.2 reaches end of life on December 31, 2026, so plan a move to PHP 8.3 or later before then. Who applies PHP updates depends on the hosting plan, so get it in writing.
Other PHP frameworks keep their own calendars. A Yii HIPAA compliant app, for example, has two dates to plan around. Yii 2.0.50 and later get only security fixes from November 23, 2026, and reach end of life on November 23, 2027.
The 8 settings that make a Laravel app HIPAA-ready
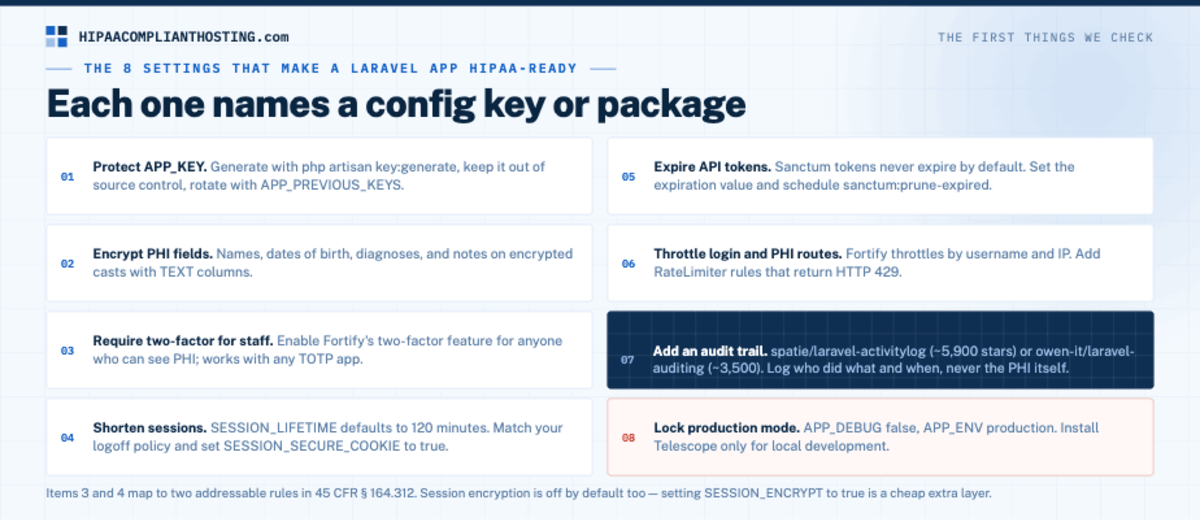
Start with these eight settings in any Laravel HIPAA compliant build. Each one names the config key or package from Laravel's docs.
Protect APP_KEY. Generate it with php artisan key:generate and keep it out of source control. Rotate it with APP_PREVIOUS_KEYS, so old data still decrypts.
Encrypt PHI fields. Put names, dates of birth, diagnoses, and notes on encrypted casts with TEXT columns.
Require two-factor for staff. Enable Fortify's two-factor feature and require it for anyone who can see PHI. It works with any TOTP app, such as Google Authenticator.
Shorten sessions. SESSION_LIFETIME defaults to 120 minutes. Set it to match your logoff policy, and set SESSION_SECURE_COOKIE to true.
Expire API tokens. Sanctum tokens never expire by default. Set the expiration value and schedule sanctum:prune-expired.
Throttle login and PHI routes. Fortify throttles login by username and IP address. Add RateLimiter rules for PHI routes, which return HTTP 429 when exceeded.
Add an audit trail. Install spatie/laravel-activitylog, with about 5,900 GitHub stars, or owen-it/laravel-auditing, with about 3,500. Log who did what and when, never the PHI itself. Our guide to HIPAA audit logs covers what to record and how long to keep it.
Lock production mode. Keep APP_DEBUG false and APP_ENV set to production. Install Telescope only for local development.
Item 4 maps to the addressable automatic logoff rule in 45 CFR § 164.312(a)(2)(iii). Item 3 supports the person or entity authentication standard in § 164.312(d), which does not name a method. The logoff rules are in HIPAA automatic logoff, and how HIPAA treats two-factor login is covered in HIPAA MFA requirements. Session encryption is off by default too. Setting SESSION_ENCRYPT to true is a cheap extra layer. With all eight in place, most of the Laravel HIPAA compliant work inside the app is done.
Where do Laravel apps leak PHI?
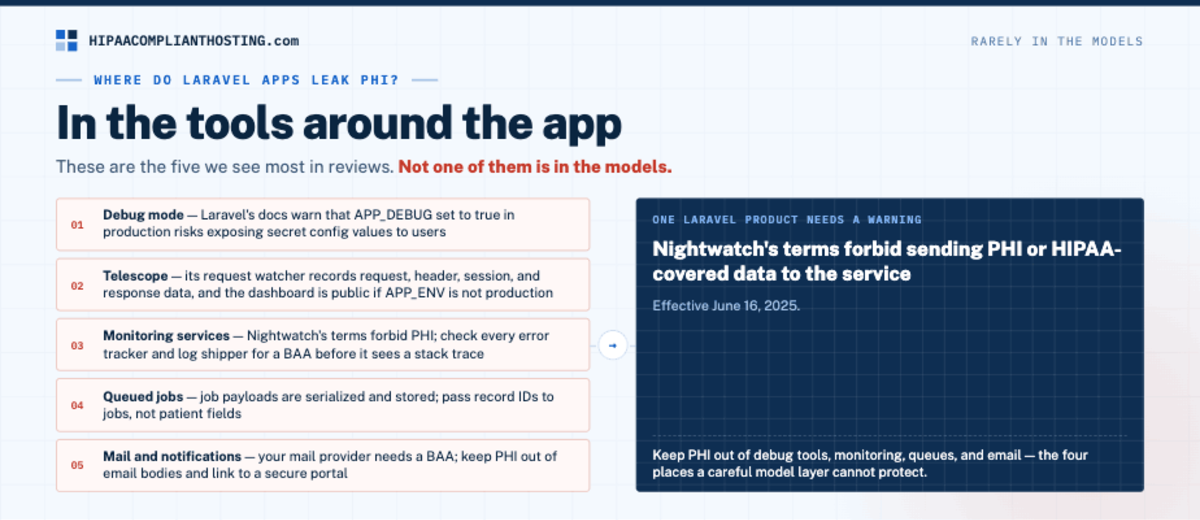
Rarely in the models. Leaks come from the tools around the app. Check these five places in any Laravel HIPAA compliant app.
Debug mode. Laravel's docs warn that APP_DEBUG set to true in production risks exposing secret config values to users.
Telescope. Its request watcher records request, header, session, and response data. The docs say the dashboard is public if APP_ENV is not set to production.
Monitoring services. Nightwatch's terms bar PHI without Laravel's prior written approval. Check every error tracker and log shipper for a BAA before it sees a stack trace.
Queued jobs. Job payloads are serialized and stored. Pass record IDs to jobs, not patient fields.
Mail and notifications. Your mail provider needs a BAA. Keep PHI out of email bodies and link to a secure portal instead. Our best HIPAA compliant email guide lists providers that sign.
AI features add a newer path for PHI. Laravel 13 introduced a first-party AI SDK for text generation, agents, and embeddings. Any model provider that receives PHI through it is a business associate and needs a BAA. Our guide to HIPAA compliant AI hosting shows where those calls can run.
What does HIPAA hosting for Laravel cost in 2026?
A Laravel HIPAA compliant budget starts with routes that can sign a BAA. The cheap Laravel Cloud plans cannot, so they are not in this table. Figures were checked on October 20, 2026.
Route | Published starting point | Who signs the BAA | What you still own |
|---|---|---|---|
Laravel Private Cloud | Platform fee from about $2,500 per month, plus compute and a managed database | Laravel | Laravel and app patches, app settings, app audit trail, risk analysis, other vendors' BAAs |
Laravel Cloud Enterprise | Custom pricing | Laravel, on request | Laravel and app patches, app settings, app audit trail, risk analysis, other vendors' BAAs |
Your own AWS with Forge or Vapor | AWS usage plus the Forge or Vapor fee (Vapor takes no new signups) | AWS, through AWS Artifact | All hardening, patching, logging, backups, and the engineer's hours |
Managed HIPAA cloud hosting from us | From $229 per month, 4 hours of migration and configuration included | Us, within 24 hours | Laravel and app patches, app settings, app audit trail, risk analysis, other vendors' BAAs; confirm who applies OS and PHP updates |
We sell the last row, so weigh it as a disclosure. The DIY row looks cheapest until you price the engineer's hours it lists. If your database runs on AWS, read is Amazon RDS HIPAA compliant for the settings. The wider picture is in HIPAA compliant database hosting.
If you are weighing Heroku, Render, or Vercel instead, we compare them plan by plan in HIPAA compliant app hosting. Symfony teams get the same treatment, including Upsun's priced BAA add-on, in our guide to whether Symfony HIPAA compliant apps are possible. Teams that chose a micro-framework have more to build, with no encryption, sessions, or CSRF in the box. Our guide to whether Flight PHP HIPAA compliant apps are possible works through it.
If you would rather not run the server layer yourself
If your team would rather ship features than run servers, we can carry the server layer. Our HIPAA compliant Laravel hosting runs your Laravel HIPAA compliant app on a single-tenant AWS server, encrypted at rest and in transit. Every plan includes a web application firewall, CloudFront CDN, six-year audit logging, and tested encrypted backups. EBS storage keeps snapshots for 7 days. The BAA is signed within 24 hours of signup, before patient data moves. Our BAA covers the servers and services we run.
Plans start from $229 per month, with 4 hours of migration and configuration included in the first month. After that, work is $175 an hour, quoted before work starts. Monthly plans have no long-term contract. If your Laravel app ships in containers, HIPAA compliant Docker hosting starts from $259 per month. Our guide to whether Docker HIPAA compliant setups are possible covers what that host must get right, from rootless mode to your image registry. You keep Laravel and your code. We carry the server layer and sign for it. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your company already negotiated Laravel Private Cloud, it covers the infrastructure layer, and you do not need us. If your team runs AWS under AWS's BAA and an engineer owns patching, logging, and backups, that path works and costs less in cash. With any managed host, ours included, confirm in writing who applies OS and PHP updates. Each of our plans is one server in one AWS availability zone, and a multi-zone design is quoted separately. Root access comes only through an Enterprise engagement, so teams used to root access on Forge should plan for that. And if your app never touches PHI for a covered entity, HIPAA does not apply at all. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what you are building and get a straight answer.
Frequently asked questions
Is Laravel HIPAA compliant?
No framework is HIPAA compliant by itself. A Laravel HIPAA compliant system needs a host that signs a BAA. The app also needs encrypted casts, two-factor login, short sessions, and an audit log. Your organization completes the risk analysis. Laravel's own August 2026 post says the application side stays with you.
Does Laravel Cloud sign a BAA?
Yes, on the Enterprise and Private Cloud plans only, as of October 20, 2026. Enterprise is custom-priced, and Private Cloud starts at a platform fee of about $2,500 per month plus compute and database. For Laravel HIPAA compliant hosting from Laravel itself, request the BAA at [email protected] before deploying PHI. The Starter, Growth, and Business plans do not include HIPAA support.
Does Laravel encrypt data at rest?
Only the fields you choose. Laravel's encrypted casts encrypt model attributes with AES-256-CBC and a message authentication code before saving them. Encrypted columns must be TEXT or larger and cannot be searched. Disk and backup encryption come from your host.
Does Laravel have an audit log?
No. Laravel has application logging but no built-in record of who viewed or changed PHI. Most teams add spatie/laravel-activitylog or owen-it/laravel-auditing, and pair it with server and database logs from the host.
Are Laravel Forge and Vapor HIPAA compliant?
Neither makes a HIPAA or BAA statement on its public page as of October 20, 2026. A Laravel HIPAA compliant setup on either one depends on the underlying cloud. Forge manages servers you own, so your server provider's BAA matters. Vapor runs on AWS Lambda in your AWS account, which AWS covers under its own BAA when configured correctly. Vapor no longer accepts new signups, so a new project needs another route.
Which Laravel version should a HIPAA app run?
A Laravel HIPAA compliant app should run Laravel 13, or Laravel 12 until its security fixes end on February 24, 2027. Laravel 11 stopped getting security fixes on March 12, 2026. As of October 20, 2026, versions 13.30.0 and 12.69.0 or later include every fix in Laravel's published framework advisories. Also run at least the fixed PHP release for your branch: 8.2.35, 8.3.36, 8.4.27, or 8.5.12. These October 21, 2026 releases fix two critical flaws, and PHP 8.2 gets no security fixes after December 31, 2026. Patch monthly and record the version in your risk analysis.
Recap: Laravel HIPAA compliant
To recap, a Laravel HIPAA compliant app needs three things. It needs a host that signs a BAA, a hardened server, and an app configured for the Security Rule. Laravel 13 gives you encrypted casts, strong hashing, Fortify two-factor and passkeys, CSRF protection, and rate limiting. It does not give you an audit trail, so add one. Laravel Cloud signs a BAA only on Enterprise and Private Cloud. Any other Laravel HIPAA compliant route needs a host that signs. Forge and Vapor leave the BAA to your server provider. Stay on Laravel 12 or 13, patch monthly, and keep PHI out of debug tools, monitoring, queues, and email.
This article is general information, not legal advice. Plans, prices, BAA terms, and support dates change often. The details here reflect Laravel's public docs, pricing, blog, and GitHub advisories as read on October 20, 2026. PHP release details and the CVE IDs reflect php.net and the cited GitHub advisories as read on October 22, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
Laravel: Release notes and support policy.
Laravel Cloud: Compliance and security, Pricing, and Private Cloud.
Laravel blog: Laravel Private Cloud is now HIPAA compliant (August 25, 2026).
Laravel: Forge, Vapor, and Nightwatch Terms of Service (effective June 16, 2025).
Laravel docs: Encryption, Encrypted casting, Hashing.
Laravel docs: Session, CSRF protection, Rate limiting.
Laravel docs: Configuration and debug mode, Telescope.
Laravel skeleton: config/session.php defaults.
GitHub advisories: CVE-2026-48019, XSS in debug page, and Token-based API guard auth bypass (October 19, 2026).
PHP: Security advisory: Critical remote code execution vulnerabilities, update now and PHP 8.2.35 release notes (October 21, 2026).
Audit packages: spatie/laravel-activitylog and owen-it/laravel-auditing.
45 CFR § 164.312 (technical safeguards): law.cornell.edu.
45 CFR § 164.308 (administrative safeguards, BAA requirement): law.cornell.edu.
45 CFR § 160.103 (definitions): law.cornell.edu.
AWS: HIPAA Eligible Services Reference (last updated October 15, 2026).