


Is ChatGPT HIPAA compliant? Which products get a BAA, and what stays with you
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-chatgpt-hipaa-compliant
Last updated: November 20, 2026
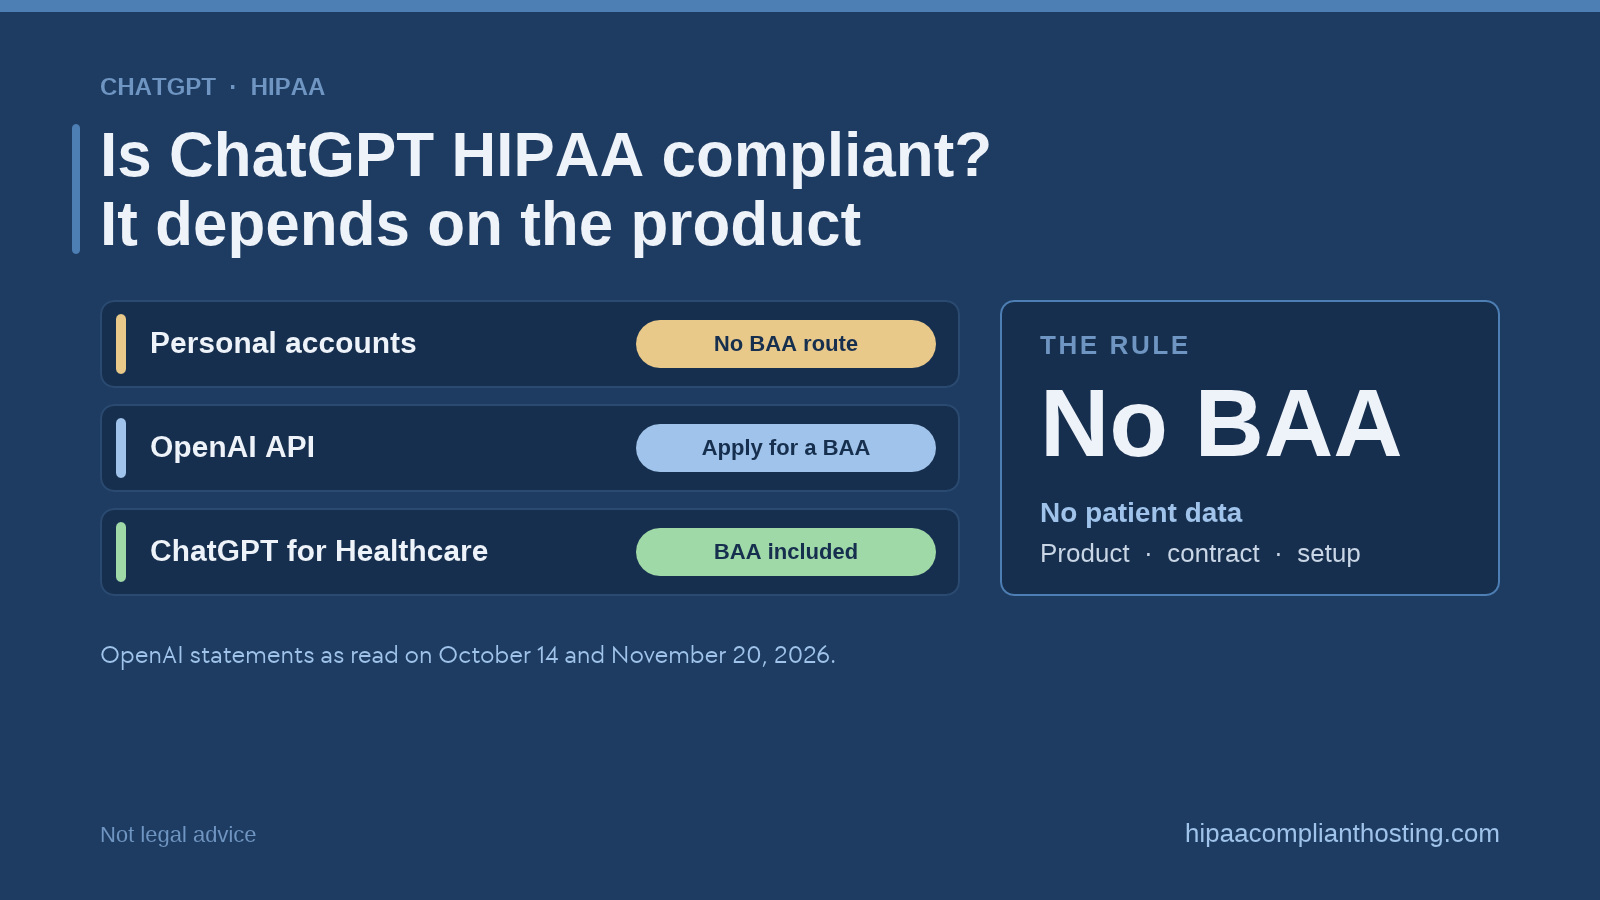
ChatGPT is HIPAA compliant only on the products where OpenAI signs a business associate agreement (BAA) with you. A personal ChatGPT account never qualifies. OpenAI says ChatGPT for Healthcare includes a BAA, and eligible API customers can apply for one. So the answer to "is ChatGPT HIPAA compliant" depends on the product, the contract and your own setup.
This guide is for IT, security and compliance leads at health systems, multi-site groups and healthtech companies. It also fits a small clinic whose staff already use ChatGPT. We are HIPAA Compliant Hosting. We sell managed hosting, not AI tools, so weigh the one marked section about our plans as a disclosure.
TL;DR: Quick answer
No BAA, no PHI. Without a signed BAA from OpenAI, protected health information (PHI) does not belong in ChatGPT.
Personal accounts are out. A personal ChatGPT account has no BAA route, whatever its privacy settings.
Some products qualify. OpenAI says ChatGPT for Healthcare includes a BAA. Its help center also listed regulated Enterprise workspaces and ChatGPT for Clinicians when we read it on October 14, 2026.
The API is separate. PHI through the API needs OpenAI's Business Associate and Healthcare Addendum on file.
The contract is the start. Access limits, staff rules and a risk analysis are still yours.
What makes ChatGPT HIPAA compliant?
A signed BAA with OpenAI, plus your own safeguards. HIPAA does not certify software. It regulates how a covered entity or business associate uses a tool. A vendor that receives PHI on your behalf is a business associate. Under 45 CFR 164.308(b), you need a written contract with that vendor first. Our guide to the HIPAA business associate agreement covers what the contract must say.
So ChatGPT HIPAA compliant use has two parts. OpenAI signs for the product you use. You control who uses it, what goes in and where the output lands.
Which ChatGPT products can get a BAA?
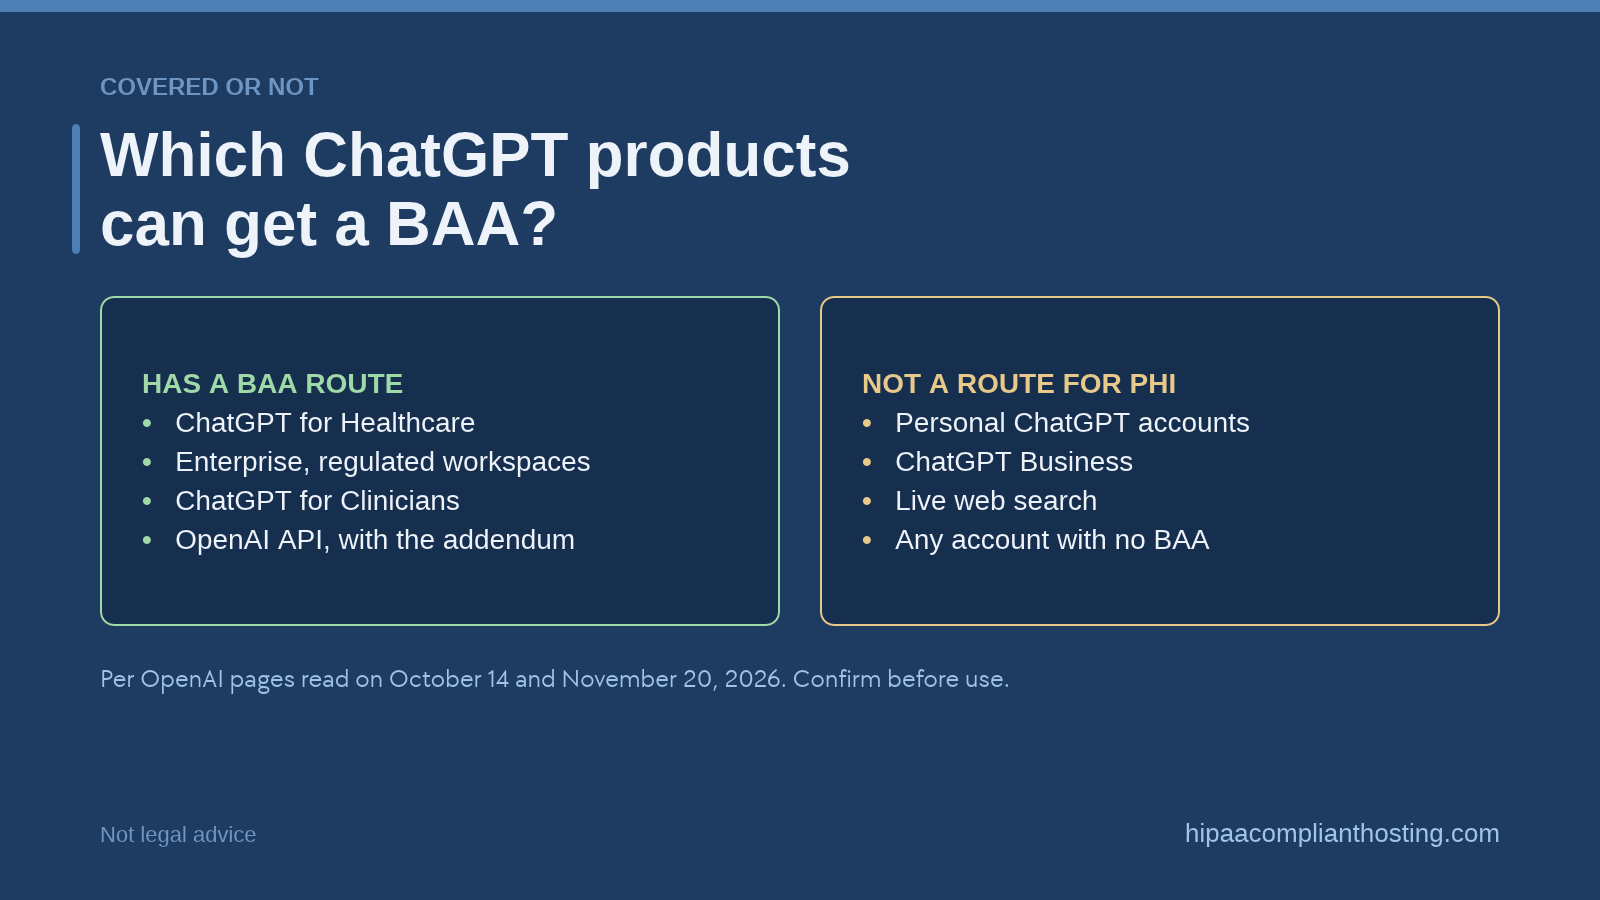
It depends on the exact product. The table shows OpenAI's own statements and the date we read each one.
Product | What OpenAI says | Read on |
|---|---|---|
ChatGPT for Healthcare | Its launch page lists a BAA with OpenAI among the product's data controls | November 20, 2026 |
OpenAI API | Eligible customers can apply for a BAA. PHI needs an executed Business Associate and Healthcare Addendum | November 20, 2026 |
ChatGPT Enterprise, regulated workspaces | Listed by its help center as HIPAA eligible | October 14, 2026 |
ChatGPT for Clinicians | Its help center said verified US clinicians can sign a BAA | October 14, 2026 |
ChatGPT Business | Its help center said it offers no BAA | October 14, 2026 |
Personal ChatGPT accounts | Not on its list of HIPAA eligible products | October 14, 2026 |
We could not reopen OpenAI's help center on November 20, 2026, so four rows carry the earlier date. Product names and terms change often. Confirm each one with OpenAI before you plan ChatGPT HIPAA compliant use around it.
Which ChatGPT accounts are never covered?
Any account with no BAA behind it. That includes the personal accounts staff open with their own email. Privacy settings do not change this. Turning off chat history or model training is not a contract. No setting makes a personal account ChatGPT HIPAA compliant.
This is the common failure. A clinician pastes a patient note into a personal account to get a quick summary. That is a disclosure with no BAA behind it. A written rule and a covered option fix more than a ban does. Our guide to AI patient data privacy covers staff use in detail.
What does the BAA leave out?
Even on a covered product, some parts sit outside the contract.
Live web search. OpenAI's API data page says web search with live internet access is not HIPAA eligible and is not covered by a BAA.
Features outside the covered list. A BAA covers the listed product and functions, not everything OpenAI ships. Check the list before you turn on a new feature.
Third-party connections. An app or connector that receives PHI is its own vendor. It needs its own BAA.
Your own systems. The BAA covers OpenAI's service. It does not cover the app, database or logs where you keep prompts and answers.
Retention is a setting to check too. OpenAI says its API keeps abuse monitoring logs for up to 30 days by default. It says zero data retention needs its prior approval. Record the setting you have in your risk analysis.
How do you make ChatGPT HIPAA compliant in practice?
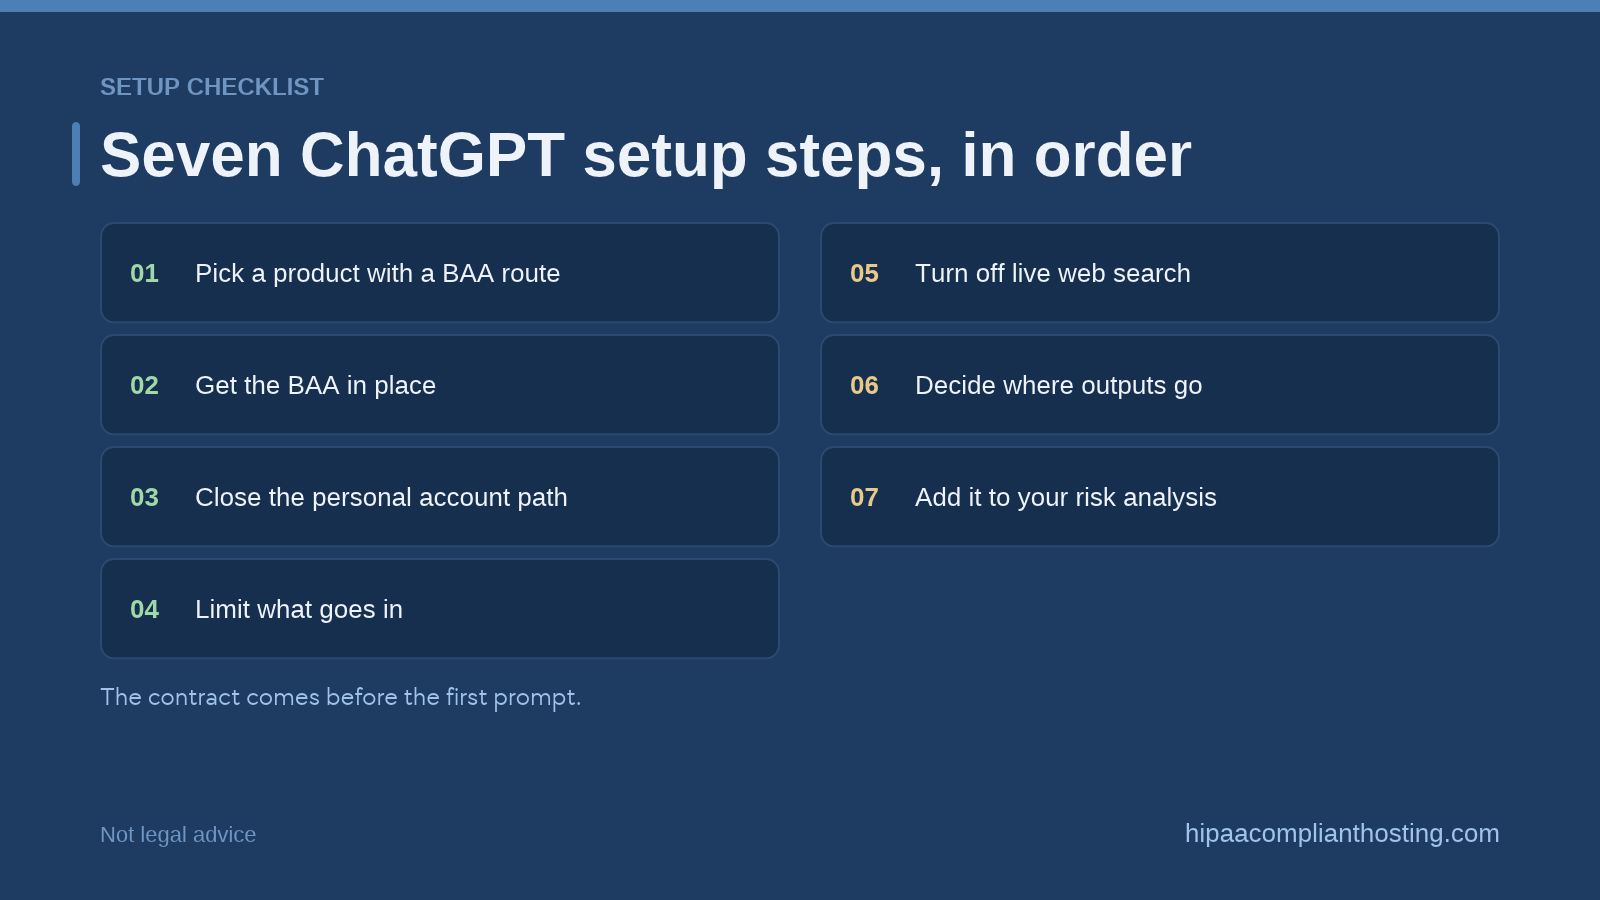
ChatGPT HIPAA compliant use takes seven steps, in this order. The contract comes before the first prompt.
Pick a product with a BAA route. Match the product to the work: a workspace for staff, or the API for your own app.
Get the BAA in place. Do this before any PHI goes in, and keep a copy with your vendor records.
Close the personal account path. Tell staff which account is approved, and use single sign-on where the product supports it.
Limit what goes in. Share only what the task needs, in line with the minimum necessary standard.
Turn off what the BAA does not cover. Start with live web search.
Decide where outputs go. A summary pasted into a chart, an email or a ticket is PHI there too.
Add it to your risk analysis. Record the product, the BAA and the data flows in your HIPAA risk analysis.
One more rule sits outside HIPAA. Have a person review clinical output before it reaches a chart or a patient.
What changes for a health system and for a small clinic?
The rules are the same. The work behind ChatGPT HIPAA compliant use is not.
Health systems and multi-site groups. The hard part is control at scale. OpenAI lists single sign-on, audit logs, data residency and customer managed keys among the options for ChatGPT for Healthcare. Decide who owns each one before rollout.
Healthtech companies. You will likely use the API. Customers will ask which model vendor sees their patients' data, so keep the addendum and your endpoint list ready. Our guide to the HIPAA compliant chatbot covers the three BAAs such a build needs.
Small clinics. The risk is the personal account already open on the front desk computer. If no covered product fits your budget, keep PHI out and use ChatGPT for work with no patient details.
ChatGPT is not the only route. If you already run Microsoft 365, see our guide to Microsoft Copilot. For Gemini on Google Cloud, see Google Cloud.
Where does our hosting fit, and where does it not?
We sell this, so weigh it as a disclosure. We do not sell ChatGPT or any AI model. We host the app layer of a ChatGPT HIPAA compliant build.
Where we fit. An app built on the OpenAI API has its own servers, database and logs. That layer needs a host that signs a BAA, and it is the layer we run.
Setup. Single-tenant AWS. Each plan is one server in one AWS availability zone.
BAA. We sign the BAA within 24 hours of signup, before patient data moves. Our BAA covers the servers and services we run. Email, SMS, EHR, form and AI model vendors need their own BAA.
Safeguards. Every plan includes CloudFront CDN, a web application firewall (WAF), encryption at rest and in transit, six-year audit logging and tested encrypted backups.
Where we do not fit. Staff who only use ChatGPT in a browser. That needs OpenAI's BAA, not a host.
Monthly plans have no long-term contract. Managed plans from $229 a month.
Frequently asked questions
Is ChatGPT HIPAA compliant?
Only where OpenAI has a BAA in place with you for that product, and you have set it up with care. A personal account is never covered.
Does OpenAI sign a BAA?
Yes, for some products. OpenAI says ChatGPT for Healthcare includes one, and eligible API customers can apply. Confirm your product with OpenAI before PHI goes in.
Is ChatGPT Plus HIPAA compliant?
Plus is a personal plan, and we did not see it on OpenAI's list of HIPAA eligible products on October 14, 2026. Treat it as no route to ChatGPT HIPAA compliant use unless OpenAI confirms otherwise in writing.
Can I use ChatGPT if I remove patient names?
Removing names is not enough. HIPAA lists 18 identifiers, and dates, phone numbers and record numbers all count. Use a formal method to remove identifiers before you rely on this.
Does OpenAI train on our data?
OpenAI says content shared with ChatGPT for Healthcare is not used to train models. It says API data is not used for training by default. Check the terms for any other plan.
Recap: is ChatGPT HIPAA compliant?
ChatGPT HIPAA compliant use starts with the right product and a BAA from OpenAI. Personal accounts never qualify. After the contract, the work is yours. Close the personal account path, limit what goes in, turn off live web search and write it into your risk analysis.
If you are building an app on the OpenAI API, tell us what it runs on and where its data is stored. Request a quote and we will reply with a plan and a price, with no long-term contract.
This article is general information, not legal advice. OpenAI's statements are as read on the dates shown, and they change often. Check OpenAI's current pages and your own agreement, and ask counsel about contract terms. We sell HIPAA compliant hosting. Reviewed November 2026.
Sources
45 CFR 164.308 (business associate contracts).
OpenAI: Introducing OpenAI for Healthcare (January 8, 2026; read November 20, 2026).
OpenAI: Data controls in the OpenAI platform (read November 20, 2026).
OpenAI help center: HIPAA eligible products and functionality (read October 14, 2026).
OpenAI help center: Getting a BAA for the OpenAI API (read October 14, 2026).