


Is Ghost CMS HIPAA Compliant? Ghost(Pro), Mailgun, and the Self-Hosted Path (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-ghost-cms-hipaa-compliant
Last updated: October 20, 2026
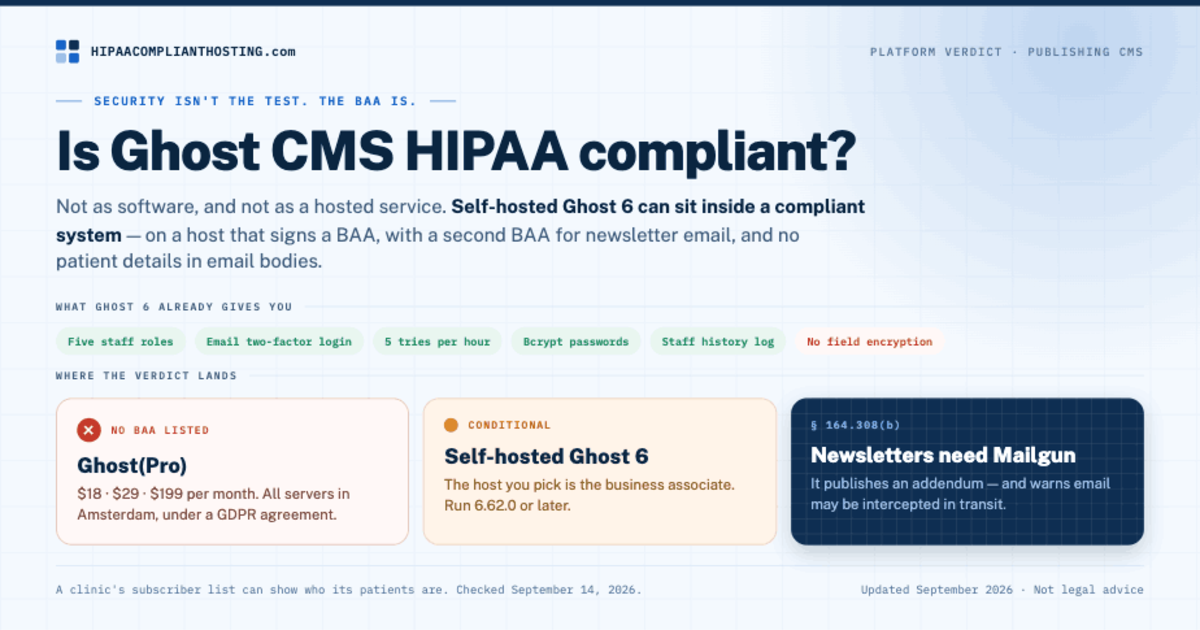
Ghost is not HIPAA compliant as software or as a hosted service. Ghost(Pro) offers no Business Associate Agreement (BAA) on any of its public pages, and its servers are in Amsterdam. Self-hosted Ghost 6 can sit inside a compliant system. It needs a host that signs a BAA and a separate BAA for newsletter email. And patient details must stay out of email bodies. That is the short answer to whether a Ghost CMS HIPAA compliant setup is possible. Yes, with work, and not on Ghost(Pro). Healthcare teams like Ghost for patient newsletters, memberships, and health education. Those uses carry more risk than they look. A clinic's subscriber list can show who its patients are. This guide covers what Ghost 6 gives you, what Ghost(Pro) and Mailgun offer, and the settings that matter. If you would rather hand off the server side, see our HIPAA compliant Ghost hosting. We sell it, so weigh our view with that in mind. Every fact was rechecked on October 20, 2026. One note: this page is about Ghost, the open-source publishing platform, not the analytics product Ghost Metrics.
TL;DR: Quick answer
Ghost(Pro) costs $15, $29, or $199 per month billed yearly, or $18, $35, or $239 billed monthly. Its pricing, terms, privacy, and data processing pages mention no HIPAA support or BAA.
Ghost(Pro) servers are in Amsterdam, the Netherlands. Its data agreement is written for the EU's GDPR, not HIPAA.
Newsletters need Mailgun. Mailgun publishes a HIPAA Business Associate Addendum, but it warns that email may be intercepted in transit.
Ghost 6 gives staff email-based two-factor login, a 5-per-hour login limit, bcrypt passwords, and a staff history log. It has no field encryption.
Ghost 5 reached end of life in January 2026. A Critical flaw disclosed on September 3, 2026 let suspended staff reactivate their accounts. It is fixed in 6.62.0. Newer flaws, published October 1, 2026, are fixed in 6.67.0, so run that version or later.
If you want the server layer handled, we host Ghost on single-tenant AWS and sign a BAA within 24 hours of signup. Managed plans start at $229 a month.
Is Ghost CMS HIPAA compliant? The three-layer answer
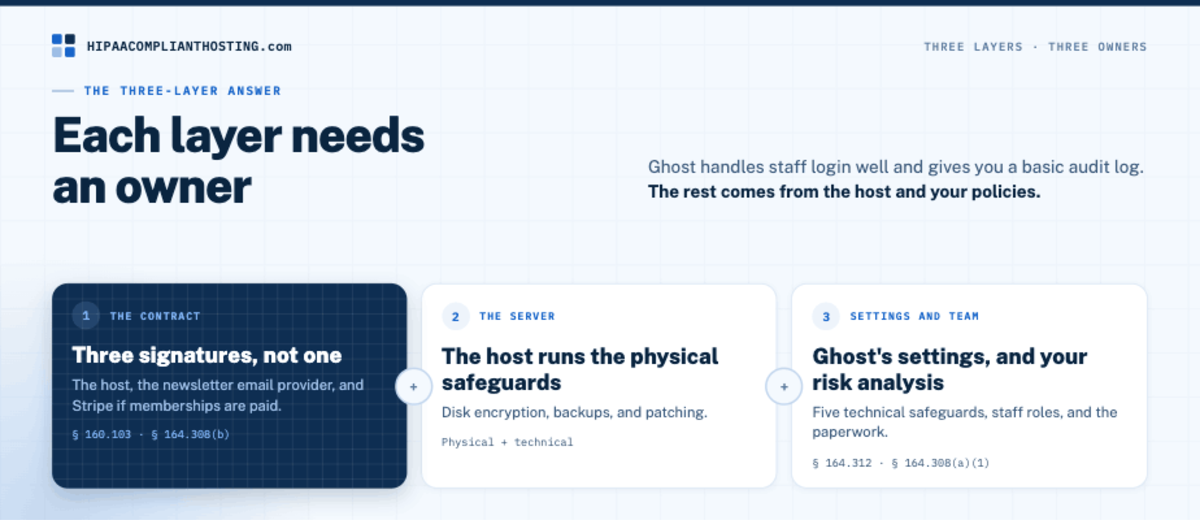
A Ghost CMS HIPAA compliant system has three layers, and each one needs an owner. The first is the contract. Any vendor that stores or processes protected health information (PHI) for a covered entity is a business associate under 45 CFR § 160.103. Under 45 CFR § 164.308(b), you need a signed BAA with that vendor first. With Ghost, that means the host and the newsletter email provider. If memberships are paid, review Stripe too. Our HIPAA business associate agreement guide explains what each contract must cover. The second layer is the server. The host runs the physical safeguards, disk encryption, and backups. Get in writing who patches the operating system, Node.js, and MySQL. The third layer is Ghost's settings and your team. The HIPAA Security Rule lists five technical safeguards in 45 CFR § 164.312. They are access control, audit controls, integrity, person or entity authentication, and transmission security. Ghost handles staff login well and gives you a basic audit log. That covers part of a Ghost CMS HIPAA compliant build. The rest comes from the host and your policies. You also run a risk analysis under 45 CFR § 164.308(a)(1).
Not every Ghost site handles PHI. A practice blog with public articles and no sign-ups holds none. The Ghost CMS HIPAA compliant question gets real when patients join a member list, pay for a program, or reply to a newsletter. Member records hold email addresses, names, notes, labels, and Stripe customer IDs. If those members are a provider's patients, the list itself can reveal who is a patient.
What does Ghost 6 give you for the HIPAA technical safeguards?
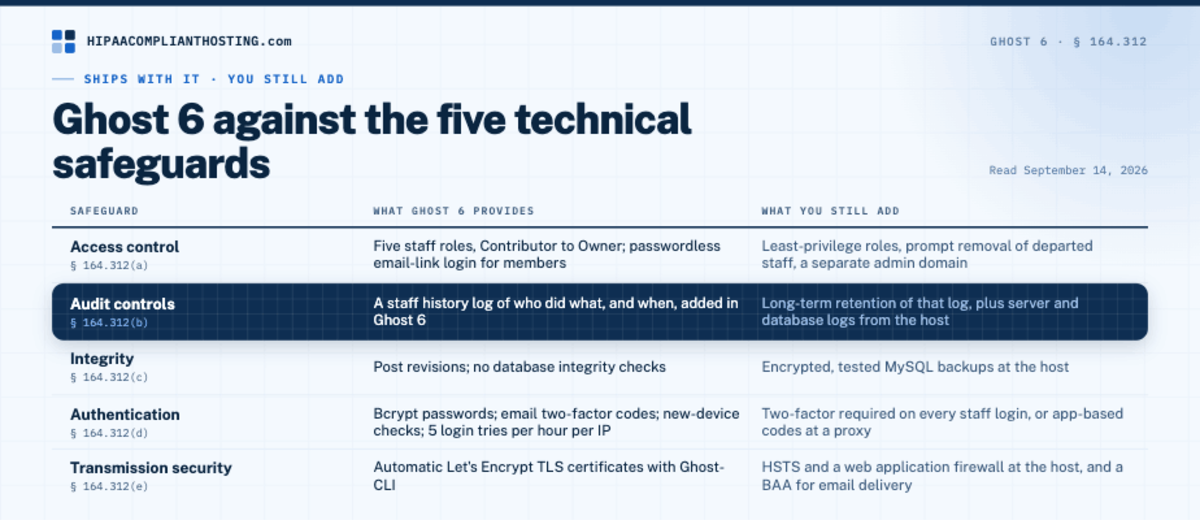
Here is how Ghost 6 maps to each rule in 45 CFR § 164.312. The middle column is what ships in Ghost. The last column is what a Ghost CMS HIPAA compliant site still needs from you or your host.
Safeguard (45 CFR § 164.312) | What Ghost 6 provides | What you still add |
|---|---|---|
Access control, (a) | Five staff roles, from Contributor to Owner; passwordless email-link login for members | Least-privilege roles, prompt removal of departed staff, and a separate admin domain |
Audit controls, (b) | A staff history log of who did what, and when | Long-term retention of that log, plus server and database logs from the host |
Integrity, (c) | Post revisions; no database integrity checks | Encrypted, tested MySQL backups at the host |
Person or entity authentication, (d) | Bcrypt passwords; email two-factor codes; new-device checks; 5 login tries per hour per IP address | Requiring two-factor on every staff login, or app-based two-factor at a proxy |
Transmission security, (e) | Automatic Let's Encrypt TLS certificates with Ghost-CLI | HSTS and a web application firewall at the host, and a BAA for email delivery |
Two limits matter most. First, Ghost's two-factor login sends a six-digit code by email. It has no authenticator app option. If your policy needs app-based codes, add them in front of the admin panel. Second, Ghost's docs say staff users are trusted by default. If any staff user is not fully trusted, run the admin panel and the public site on separate domains. Both limits shape a Ghost CMS HIPAA compliant setup. The two-factor rules are in HIPAA MFA requirements. Unlike Ghost, Joomla core accepts authenticator apps and security keys, not just email codes. Our Joomla HIPAA compliant guide shows how to require MFA for each staff user group.
Does Ghost(Pro) sign a BAA?
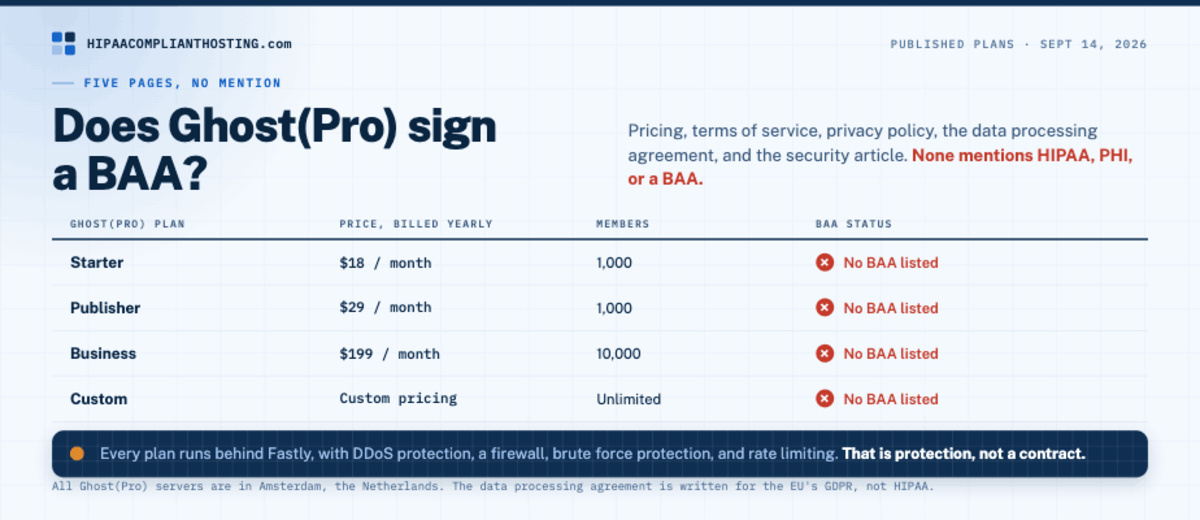
No, not on any page we could find. We checked Ghost(Pro)'s pricing page, terms of service, privacy policy, data processing agreement, and its security and data practices article. None mentions HIPAA, PHI, or a Business Associate Agreement. The data processing agreement is written for the EU's GDPR. It says data outside the EU may be processed anywhere in the world. Ghost's help center says all Ghost(Pro) servers are in Amsterdam, the Netherlands. So Ghost(Pro) is not a Ghost CMS HIPAA compliant route today. Here are its plans as published on October 20, 2026.
Ghost(Pro) plan | Price, billed yearly | Price, billed monthly | Members included |
|---|---|---|---|
Starter | $15 per month | $18 per month | 1,000 |
Publisher | $29 per month | $35 per month | 1,000 |
Business | $199 per month | $239 per month | 10,000 |
Custom | Custom pricing | Custom pricing | Unlimited |
Ghost(Pro) does have real security, even without a BAA. Every plan runs behind Fastly, with DDoS protection, a web application firewall, brute force protection, and rate limiting. That is protection, not a contract. HIPAA needs the contract. If your Ghost site handles no PHI, Ghost(Pro) is a sound and affordable host.
Is Mailgun HIPAA compliant for Ghost newsletters?
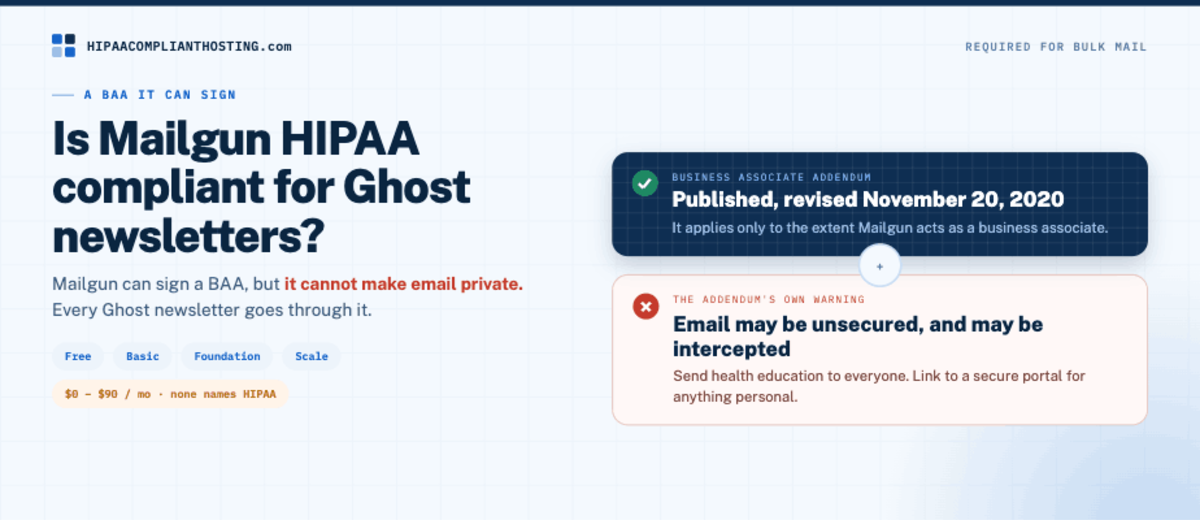
Mailgun can sign a BAA, but it cannot make email private. Ghost's docs say Mailgun is optional for transactional email and required for bulk mail. So every Ghost newsletter goes through Mailgun. Mailgun publishes a HIPAA Business Associate Addendum, last revised November 20, 2020. It applies only to the extent Mailgun acts as a business associate. The addendum also warns that email sent through Mailgun may be unsecured and may be intercepted. Mailgun's pricing page lists Free, Basic, Foundation, and Scale plans, from $0 to $90 per month. None of those plans mentions HIPAA. Ask Mailgun in writing which plan your BAA requires. Keep that answer with your compliance records. The safe rule for a Ghost CMS HIPAA compliant newsletter is simple. Sign the Mailgun BAA, and still never put PHI in the email body. Send health education to everyone, and link to a secure portal for anything personal. Our comparison of the best HIPAA compliant email providers covers other options for one-to-one messages.
The 8 settings that make a Ghost site HIPAA-ready
Start a Ghost CMS HIPAA compliant build with these eight settings. Each one is based on Ghost's own docs, changelog, or security advisories.
Run Ghost 6.67.0 or later. Version 6.62.0 fixed the Critical flaw that let suspended staff reactivate accounts. Ghost's six newest advisories, published October 1, 2026, are fixed in 6.67.0. One is a high-severity remote code execution flaw. After you upgrade, review suspended accounts for any unexpected reactivation, as Ghost's advisory recommends. As of October 20, 2026, the latest release is 6.72.0. Ghost 5 is past end of life.
Require two-factor on every staff login. Turn it on under Settings, then Staff users, then Security. Keep staffDeviceVerification at its default, which is on.
Split the admin and public domains. Ghost's docs recommend this whenever any staff user is not fully trusted.
Remove departed staff the same day. Delete the account, not just suspend it, and confirm access is gone. Log this step each time.
Sign the Mailgun BAA before the first send. Keep newsletters general, and never place PHI in an email body.
Review Stripe if members pay. Billing data lives in your own Stripe account. HIPAA's rules do not apply to payment processing itself (42 U.S.C. § 1320d-8). Ask counsel whether anything else you send Stripe needs an agreement.
Keep the history log long term. Export it on a schedule, and pair it with host-level server and database logs.
Only install themes you trust. A March 2026 flaw let crafted themes run code on the server until Ghost 6.19.1.
Item 4 matters more than it looks. HIPAA's workforce security standard in 45 CFR § 164.308(a)(3) covers ending access when people leave. Ghost's September 2026 flaw showed that suspension alone was not enough on older versions. With all eight in place, most Ghost CMS HIPAA compliant work inside the platform is done.
Where does Ghost leak PHI?
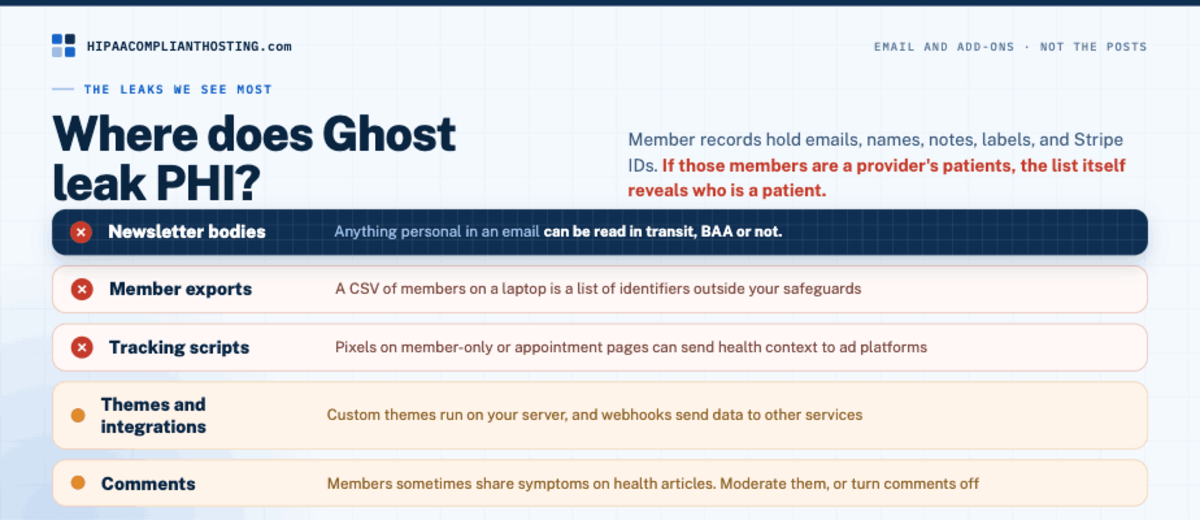
Mostly through email and add-ons, not the posts. A Ghost CMS HIPAA compliant setup watches all five paths below. Each one can move member data outside your safeguards.
Newsletter bodies. Anything personal in an email can be read in transit, BAA or not.
Member exports. A CSV of members on a laptop is a list of identifiers outside your safeguards. Names and email addresses are both among the 18 HIPAA identifiers.
Tracking scripts. Pixels on member-only or appointment pages can send health context to ad platforms. The rules are in HIPAA tracking technologies.
Themes and integrations. Custom themes run on your server, and webhooks send data to other services.
Comments. Members sometimes share symptoms in comments on health articles. Moderate them, or turn comments off.
What does HIPAA hosting for Ghost cost in 2026?
A Ghost CMS HIPAA compliant budget starts with a host that signs a BAA. Ghost(Pro) does not, so it cannot carry PHI at any price. Ghost(Pro) figures are as published on October 20, 2026.
Route | Published starting point | Who signs the BAA | What you still own |
|---|---|---|---|
Ghost(Pro) | $15 to $199 per month, billed yearly | No one listed | Not a PHI route today |
Self-hosted on your own cloud server | A server with at least 1 GB of memory, plus your time | Your cloud provider, if it signs | All hardening, Node.js and MySQL patching, logs, backups, and fast Ghost updates |
Managed hosting from us | From $229 per month ($259 for Docker hosting), with 4 hours of migration and configuration included in the first month | Us, within 24 hours of signup | Ghost settings, staff, themes, Ghost updates, your Mailgun BAA, your Stripe review, and a written agreement on who patches the operating system, Node.js, and MySQL |
We sell the last row, so weigh it as a disclosure. The DIY row looks cheap, but Ghost published 44 security advisories on GitHub between August 1 and October 20, 2026. Every self-hosted Ghost site needs those updates applied within days. Backups need the same attention, as covered in HIPAA backup and disaster recovery. If you are also weighing WordPress, see is WordPress HIPAA compliant for the same test applied there.
Headless teams can compare the Strapi HIPAA compliant route as well. Next.js teams can check the Payload CMS HIPAA compliant route too.
If you would rather not run the server layer yourself
Most teams choose Ghost to publish, not to run servers. Ghost is one of the 17 platforms we host on single-tenant AWS. Every plan includes CloudFront CDN, a web application firewall, and encryption at rest and in transit. It also includes EBS storage with 7-day snapshot retention, six-year audit logging, and tested encrypted backups. We sign the BAA within 24 hours of signup, before patient data moves. Our BAA covers the servers and services we run, so Mailgun needs its own BAA and Stripe its own review. The Ghost-specific plan details are on our HIPAA compliant Ghost CMS hosting page.
If you run Ghost's Docker Compose install, our HIPAA compliant Docker hosting gives it a single-tenant AWS host. You run the Ghost containers and their settings. If you run the classic Ghost-CLI stack, our managed HIPAA cloud hosting covers that setup. Tell us which install you use, and we match it. Your Ghost CMS HIPAA compliant setup stays the way you built it. Managed plans start at $229 a month, and Docker hosting is on our Performance tier, from $259 a month. Plans are monthly, with no long-term contract. Your first month includes 4 hours of migration and configuration. After that, work is $175 an hour, quoted before work starts. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your Ghost site is a public blog with no member sign-ups, it holds no PHI. Ghost(Pro), from $15 a month billed yearly, is then a fine choice, and you do not need us. If your team already runs a cloud server under a signed BAA and patches Ghost within days, that works too. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your members sign up for and get a straight answer.
Frequently asked questions
Is Ghost CMS HIPAA compliant?
No, not by itself. Ghost(Pro) offers no BAA and hosts in Amsterdam. A Ghost CMS HIPAA compliant setup needs self-hosted Ghost 6 on a host that signs a BAA. It also needs a Mailgun BAA, required staff two-factor login, and no PHI in newsletters.
Does Ghost(Pro) sign a BAA?
No. Ghost(Pro)'s pricing, terms, privacy policy, and GDPR data processing agreement never mention HIPAA or a BAA, as of October 20, 2026. Its servers are in Amsterdam. Without a signed BAA, Ghost(Pro) cannot store or process PHI.
Is Mailgun HIPAA compliant?
Mailgun publishes a HIPAA Business Associate Addendum, last revised November 20, 2020. It still warns that email may be intercepted in transit. Its pricing page names no HIPAA plan, so confirm eligibility with Mailgun. Keep PHI out of newsletter bodies either way.
Can I self-host Ghost on HIPAA compliant hosting?
Yes. Ghost's official stack is Ubuntu, Node.js 22, and MySQL 8 with at least 1 GB of memory. A Docker Compose install is also available as a preview. Either one can run on a host that signs a BAA and hardens the server.
Is Ghost safer than WordPress for a healthcare newsletter?
Ghost has fewer plugins to manage, which shrinks the attack surface. It still had a Critical staff access flaw in September 2026. Neither platform is compliant on its own. The host, the email BAA, and fast patching decide the outcome.
Recap: Ghost CMS HIPAA compliant
To recap, a Ghost CMS HIPAA compliant setup is self-hosted Ghost 6 on a host that signs a BAA. Ghost(Pro) offers no BAA and runs in Amsterdam, so it is not a PHI route. Newsletters run through Mailgun, which has its own BAA but warns that email can be intercepted. Ghost gives you staff roles, email two-factor, login limits, bcrypt, and a history log. You add long-term logs, same-day staff removal, trusted themes, and fast updates. Keep PHI out of email bodies, and run Ghost 6.67.0 or later.
This article is general information, not legal advice. Plans, prices, BAA terms, and support dates change often. The details here reflect Ghost's and Mailgun's public pages, docs, and GitHub advisories as rechecked on October 20, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
Ghost: Ghost(Pro) pricing, Terms of service, and GDPR data processing agreement.
Ghost: Privacy policy (server location).
Ghost help: Security and data practices.
Ghost docs: Security and Configuration.
Ghost docs: Staff users and Members.
Ghost docs: Hosting, Install with Docker (preview), and Major versions and LTS.
Ghost changelog: Ghost 6.0 (August 4, 2025) and Two-factor authentication (April 22, 2025).
GitHub: Ghost releases and Ghost security advisories.
GitHub advisories: Suspended staff account reactivation, CVE-2026-29053, and Remote code execution via bookmark card images (fixed in 6.67.0).
Mailgun: HIPAA Business Associate Addendum (revised November 20, 2020) and Pricing.
45 CFR § 164.312 (technical safeguards): law.cornell.edu.
45 CFR § 164.308 (administrative safeguards, BAA requirement): ecfr.gov.
42 U.S.C. § 1320d-8 (payment processing): law.cornell.edu.
45 CFR § 160.103 (definitions): ecfr.gov.