


Who Needs HIPAA Compliant Hosting? A Decision Framework by Role
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/who-needs-hipaa-compliant-hosting
Last updated: October 30, 2026
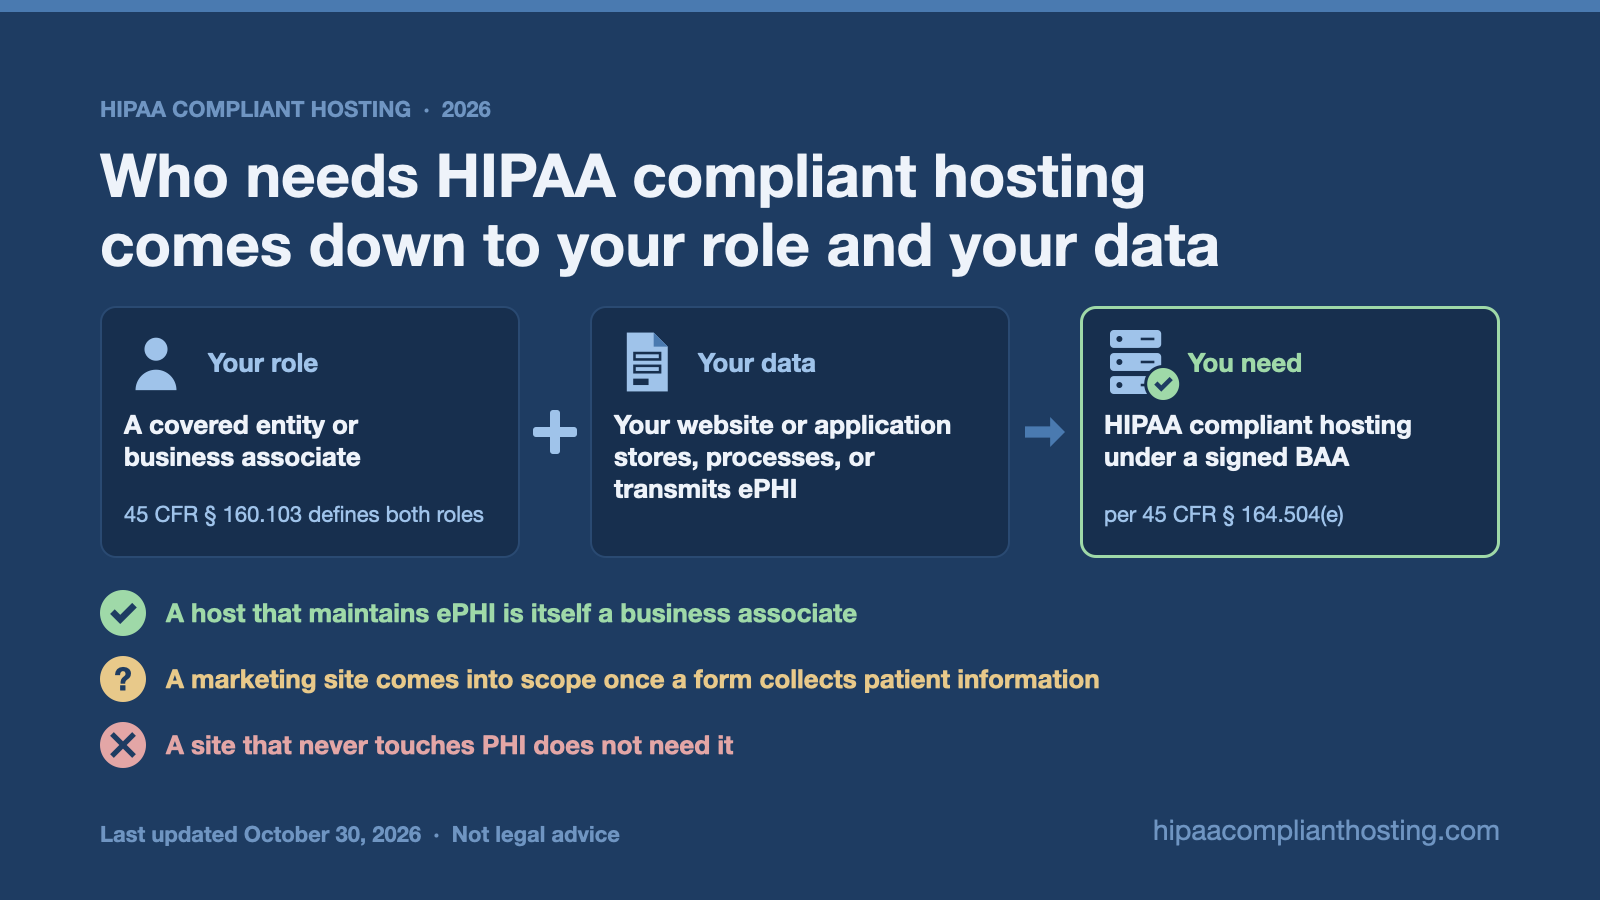
You need HIPAA compliant hosting if you are a covered entity or business associate and your website or application stores, processes, or transmits ePHI. ePHI is electronic protected health information, and 45 CFR § 160.103 defines both roles. Here is who needs HIPAA compliant hosting: healthcare providers who bill electronically, health plans, clearinghouses, and the vendors that handle patient data for them. Those vendors include healthtech SaaS companies, billing services, telehealth platforms, and agencies. A host that maintains ePHI is itself a business associate. So the hosting must sit under a signed Business Associate Agreement (BAA) per 45 CFR § 164.504(e). Choosing HIPAA compliant hosting that includes that BAA is the baseline. The hard part is not the rule; it is recognizing when your specific site is in scope.
TL;DR: Quick answer
- HIPAA reaches covered entities (providers transmitting electronically, health plans, clearinghouses) and business associates under 45 CFR § 160.103. Both need BAA-covered hosting for any system holding ePHI.
- A hosting provider that maintains ePHI is itself a business associate, so hosting PHI without a host BAA is a violation under §§ 164.308(b) and 164.504(e).
- Marketing sites become in-scope the moment an appointment or intake form collects health details. The page does not need to be a patient portal to carry ePHI.
- OCR's Risk Analysis Initiative kept settling cases in 2026, and its 14th action came in June 2026. It targets the risk analysis requirement at 45 CFR § 164.308(a)(1)(ii)(A).
- If no PHI ever touches the site or its notifications, standard hosting is generally fine; map data flows before buying either way.
Covered entities: providers, plans, and clearinghouses
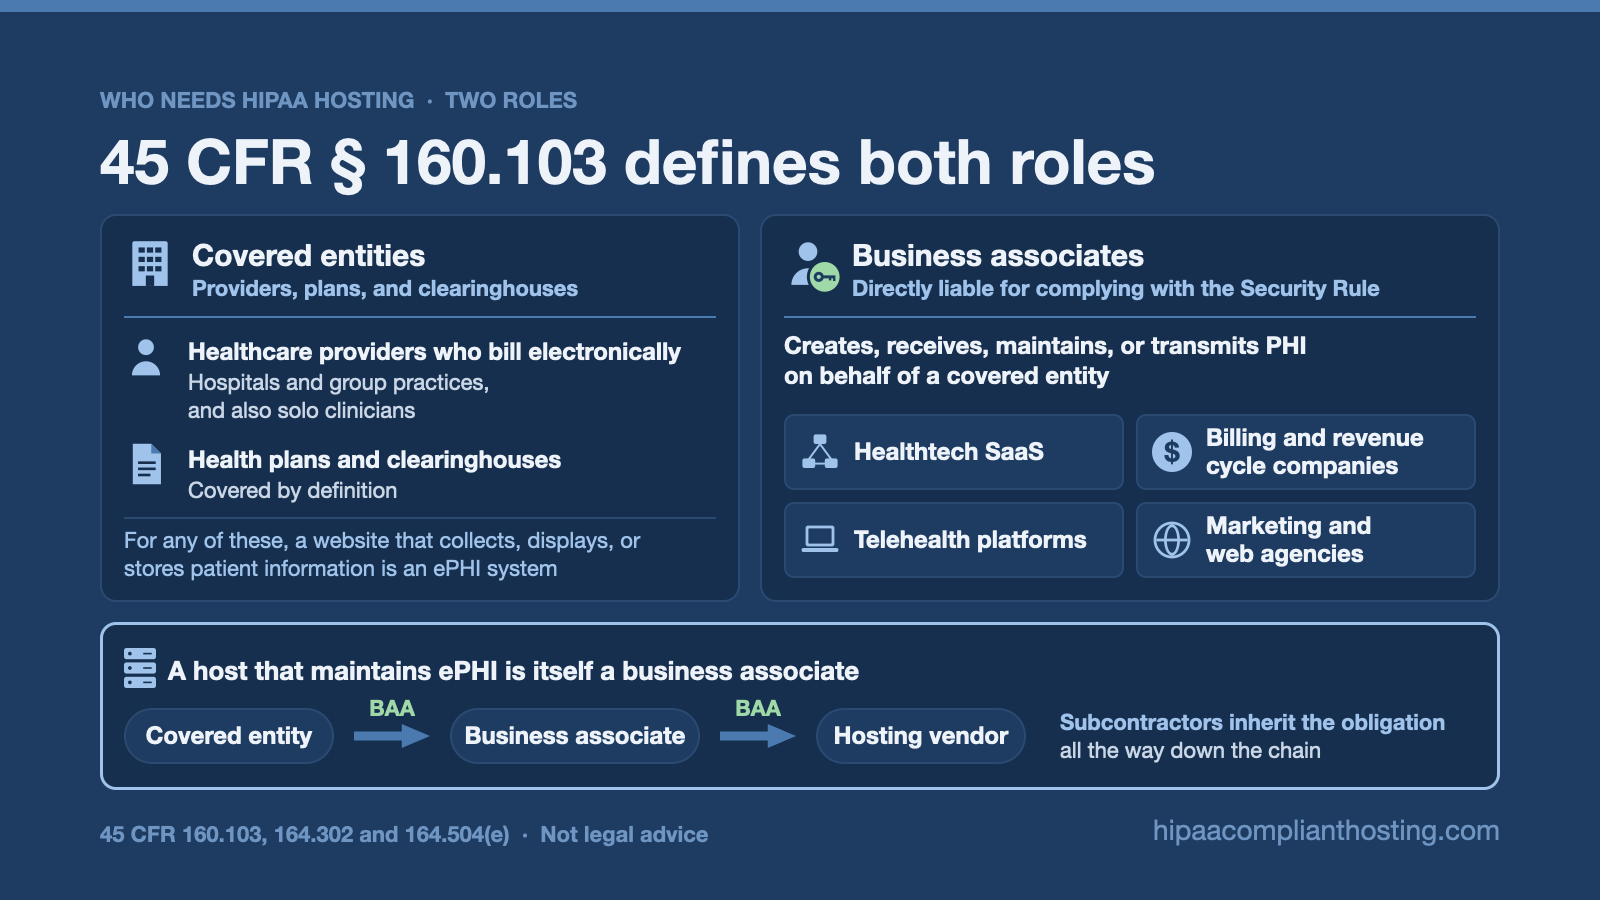
Covered entities are the first half of the answer to who needs HIPAA compliant hosting. A healthcare provider becomes a covered entity by transmitting health information electronically in connection with a standard transaction, usually insurance billing. That includes hospitals and group practices, and also solo clinicians. One example is a therapist whose website intake form feeds an insurance-billing practice; see HIPAA compliant hosting for therapists. Others include a naturopathic doctor whose biller files electronic claims, a dental office, and a home health agency. Health plans and clearinghouses are covered by definition. For any of these, a website that collects, displays, or stores patient information is an ePHI system. It belongs in the risk analysis required by 45 CFR § 164.308(a)(1)(ii)(A). It also needs the technical safeguards in § 164.312, such as access controls and audit controls. Encryption in transit and at rest is "addressable" there: encrypt where reasonable and appropriate; if not, document why and use an equivalent measure where reasonable. For a practice-specific view of what to look for, see our guide to medical website hosting.
Business associates: SaaS, billing, telehealth, and agencies
A business associate creates, receives, maintains, or transmits PHI on behalf of a covered entity. Since the 2013 Omnibus Rule, business associates are directly liable for complying with the Security Rule (45 CFR § 164.302). OCR's Risk Analysis Initiative has settled with business associates too. A New York accounting firm, BST & Co. CPAs, LLP, paid $175,000 in August 2025. A Maryland software company, MMG Fusion, LLC, paid $10,000 in March 2026. On the business associate side, this is who needs HIPAA compliant hosting:
- Healthtech SaaS. Scheduling tools, EHR add-ons, remote monitoring dashboards, AI scribes. If provider customers put patient data in your product, you need HIPAA-eligible infrastructure under a BAA with your cloud provider, plus BAAs with your customers. See HIPAA compliant hosting for healthcare SaaS.
- Billing and revenue cycle companies. Claims data is PHI end to end. See HIPAA compliant hosting for medical billing.
- Telehealth platforms. Session metadata, intake, and recordings are all ePHI. See our guide to telehealth BAA and recording rules.
- Marketing and web agencies. An agency that administers sites storing patient submissions, or that receives form data for a provider client, is a business associate. Our guide to HIPAA compliance for marketing agencies covers the scenarios.
Subcontractors inherit the obligation: a business associate's hosting vendor needs its own BAA, all the way down the chain. Developers who build these sites need the training covered in HIPAA training for web developers. Healthtech startups and small practices can compare six routes by who signs the BAA in our guide to HIPAA hosting for small businesses.
Edge cases that surprise people
- The "brochure site" with an appointment form. A five-page marketing site for a clinic is out of scope until its contact form collects patient information. Once it takes appointment requests or invites "tell us about your symptoms," submissions are ePHI. The form pipeline, database, and notification emails then all need safeguards.
- Telehealth landing pages. A campaign page that collects condition-specific signups ("get treatment for anxiety today" plus name and phone) is collecting health information in a treatment-seeking context.
- Tracking pixels. In AHA v. Becerra (N.D. Tex., June 20, 2024), a federal court vacated one part of OCR's tracking guidance. The vacated part said an IP address plus a visit to a public page about specific health conditions or providers, by itself, triggers HIPAA obligations. HHS appealed, then asked the Fifth Circuit to dismiss its own appeal. The appeal was dismissed on September 4, 2024. The rest of the guidance still applies. Trackers on patient portals, login pages, booking flows and apps can still expose PHI, and HHS says it is still evaluating its next steps.
- International companies serving US patients. HIPAA follows the data, not the server's flag. A Canadian or European company acting as a business associate for a US covered entity has HIPAA obligations wherever it hosts. See HIPAA for non-US sites serving US patients. State law can add a location duty on top. Texas SB 1188 requires covered entities, as Texas law defines them, to keep electronic health records physically in the United States or a US territory. That rule has applied to storage since January 1, 2026. The Florida health data storage law requires providers that use certified EHR technology to keep offsite patient data in the continental US, its territories, or Canada.
- Wellness businesses outside HIPAA. Most coaches and cash-only practitioners are not covered entities. They can still be business associates if they handle PHI for a covered entity. State laws such as Washington's My Health My Data Act also regulate consumer health data.
A four-question decision test
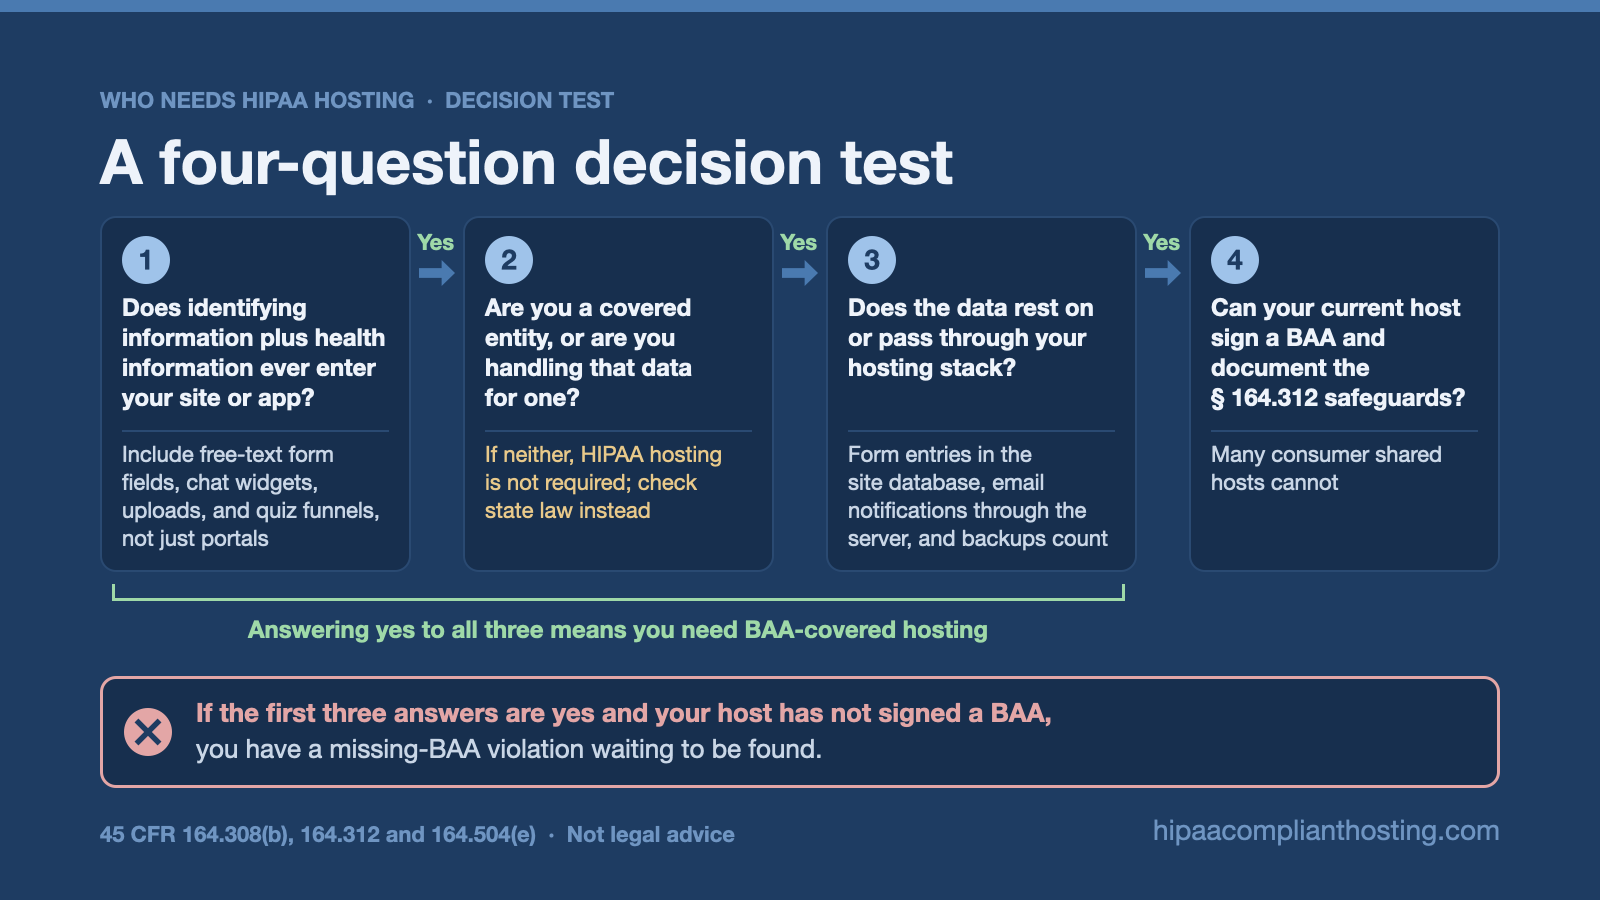
- Does identifying information plus health information ever enter your site or app? Include free-text form fields, chat widgets, uploads, and quiz funnels, not just portals.
- Are you a covered entity, or are you handling that data for one? If neither, HIPAA hosting is not required; check state law instead.
- Does the data rest on or pass through your hosting stack? Form entries in the site database, email notifications through the server, and backups all count. List each system and its host with our map of practice systems and their BAAs.
- Can your current host sign a BAA and document the § 164.312 safeguards? Many consumer shared hosts cannot. If the first three answers are yes and your host has not signed a BAA, you have a missing-BAA violation waiting to be found. If that is you, here is how to migrate to HIPAA compliant hosting.
The first three questions decide who needs HIPAA compliant hosting: answering yes to all three means you need BAA-covered hosting. What that involves and costs is covered in our HIPAA compliant hosting guide and the 2026 cost breakdown.
Once the answer is yes, the seven-step build is in make your website HIPAA compliant. Note that no host can make you "HIPAA certified"; there is no official HIPAA certification, and HHS does not recognize private ones. A HIPAA host can sign a BAA and supply safeguarded infrastructure. Your policies, training, and risk analysis are still your job. Not sure which side you fall on? Take our HIPAA hosting assessment.
Who does not need HIPAA hosting?
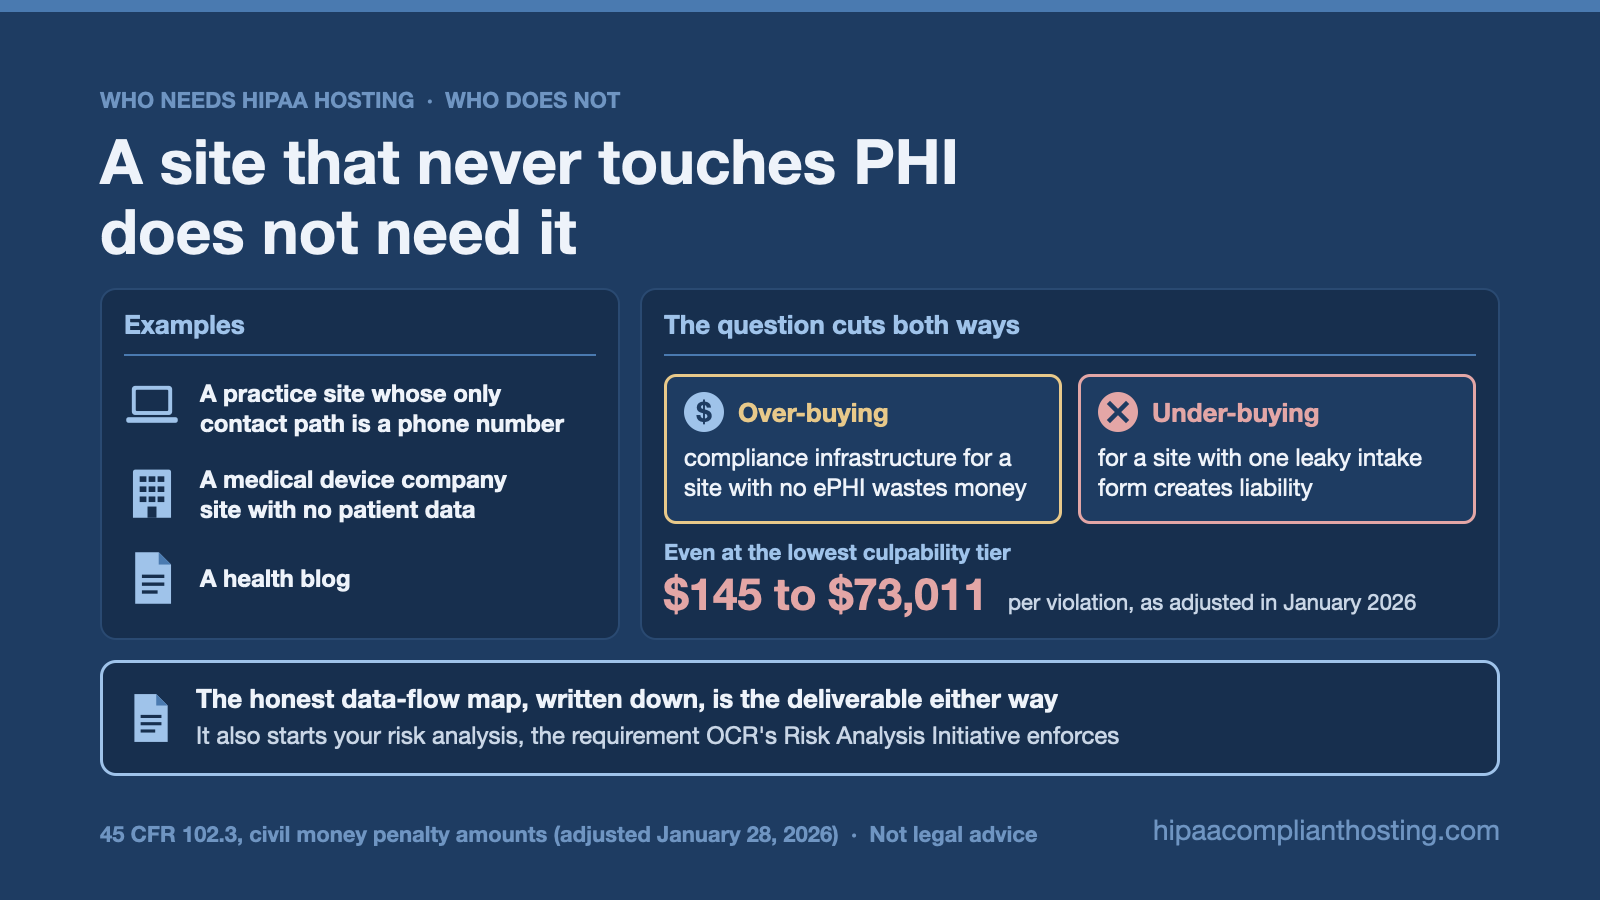
A site that never touches PHI does not need it. Examples: a practice site whose only contact path is a phone number, a medical device company site with no patient data, and a health blog. The question of who needs HIPAA compliant hosting cuts both ways. Over-buying compliance infrastructure for a site with no ePHI wastes money. Under-buying for a site with one leaky intake form creates liability. Even at the lowest culpability tier, 45 CFR § 102.3 sets $145 to $73,011 per violation, as adjusted in January 2026. The honest data-flow map, written down, is the deliverable either way. It also starts your risk analysis, the requirement OCR's Risk Analysis Initiative enforces. If the cost of BAA-covered hosting is what gives you pause, HIPAA hosting vs regular hosting compares the two side by side. Canadian practices are usually outside HIPAA and under PIPEDA or a provincial privacy law; the split is in HIPAA Canada PIPEDA. Ontario clinics fall under PHIPA rather than HIPAA; see HIPAA vs PHIPA.
Frequently asked questions
Does a small clinic website need HIPAA hosting?
Yes, if any form, chat, or upload on it collects patient information and the clinic is a covered entity. A phone-number-only brochure site generally does not.
Is regular shared hosting ever acceptable for a healthcare site?
Only when the site holds no ePHI at all. Once PHI lands in the database or mail queue, the host must sign a BAA. The setup also needs the § 164.312 technical safeguards: access control, audit controls, integrity, authentication, and transmission security. Our guide to HIPAA audit logs shows what audit controls involve. Consumer shared hosting typically will not sign a BAA or document these safeguards for you. For one common example, see our breakdown of whether GoDaddy is HIPAA compliant.
My SaaS only stores data for one doctor's office. Do I still need this?
Yes. Business associate status has no size threshold in the HIPAA definition (45 CFR § 160.103). OCR has also settled with a software company acting as a business associate: MMG Fusion, LLC, in March 2026. You need a BAA with the practice and HIPAA-eligible hosting under a BAA of your own.
Does AWS count as HIPAA compliant hosting?
Not by itself. AWS offers a BAA, and AWS lists 174 HIPAA eligible services as of its October 15, 2026 update. Eligible does not mean compliant. AWS says customers must still configure each service to meet HIPAA. Hardening and the application layer remain your responsibility. See our breakdown of whether AWS is HIPAA compliant.
What happens if I host PHI without a BAA?
The missing BAA is itself a violation under 45 CFR §§ 164.308(b) and 164.504(e), separate from any breach. HIPAA requires the BAA to be documented in writing (45 CFR § 164.308(b)(3)). During an investigation, HHS can require access to records like it (45 CFR § 160.310).
Recap: who needs HIPAA compliant hosting
To recap, deciding who needs HIPAA compliant hosting comes down to your role and your data. Covered entities and business associates whose sites or apps hold ePHI need a host that signs a BAA. A host that maintains ePHI is itself a business associate. A marketing site comes into scope once a form collects patient information. If no PHI ever touches the site or its notifications, standard hosting is generally fine. Over-buying for a site with no ePHI wastes money, and under-buying for a site with one leaky intake form creates liability.
Where to go from here
If the decision test put you in scope, map your data flows first. Then evaluate hosts against the BAA and safeguard criteria in the pillar guide. Compare your options against our roundup of the best HIPAA compliant hosting providers. For our own service page, see our HIPAA compliant healthcare hosting.
We are a HIPAA compliant hosting provider offering managed HIPAA cloud hosting on single-tenant AWS, with a BAA signed within 24 hours of signup. That puts the BAA in place before patient data moves. Managed plans start at $229 a month, on monthly terms with no long-term contract. That is our own service, so hold it to the same checklist you would apply to anyone else. You can also ask us whether your setup actually needs it. If no PHI touches your site, the answer may be no.
This article is general information, not legal advice. Whether HIPAA applies to you is fact-specific; confirm your status with qualified counsel and base safeguards on a documented risk analysis. Reviewed October 2026.
Sources
- 45 CFR § 160.103, covered entity and business associate definitions: ecfr.gov
- 45 CFR § 164.504(e), business associate contracts: ecfr.gov
- 45 CFR § 164.312, technical safeguards: ecfr.gov
- HHS OCR, covered entities and business associates: hhs.gov
- HHS OCR, guidance on HIPAA and cloud computing: hhs.gov
- AWS, HIPAA compliance program: aws.amazon.com
- 45 CFR § 164.308, risk analysis and written business associate contracts: law.cornell.edu
- 45 CFR § 164.302, Security Rule applies to business associates: law.cornell.edu
- 45 CFR § 160.310, records and access during investigations: law.cornell.edu
- 45 CFR § 102.3, civil money penalty amounts (adjusted January 28, 2026): law.cornell.edu
- HHS OCR, BST & Co. CPAs settlement, August 18, 2025: hhs.gov
- HHS OCR, MMG Fusion settlement, March 5, 2026: hhs.gov
- HHS OCR, health plan ransomware settlement and 14th Risk Analysis Initiative action, June 18, 2026: hhs.gov
- American Hospital Association v. Becerra, No. 4:23-cv-01110 (N.D. Tex.), and Fifth Circuit No. 24-10775: district docket and appeal docket
- HHS OCR, use of online tracking technologies bulletin: hhs.gov
- Texas SB 1188 (89th Legislature), enrolled text: capitol.texas.gov
- Florida Statutes section 408.051 (2026): leg.state.fl.us
- Washington My Health My Data Act, RCW 19.373: app.leg.wa.gov
- AWS, HIPAA Eligible Services Reference (updated October 15, 2026): aws.amazon.com