


Is n8n HIPAA Compliant? n8n Cloud, Self-Hosting, and Where Execution Data Goes (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-n8n-hipaa-compliant
Last updated: September 28, 2026
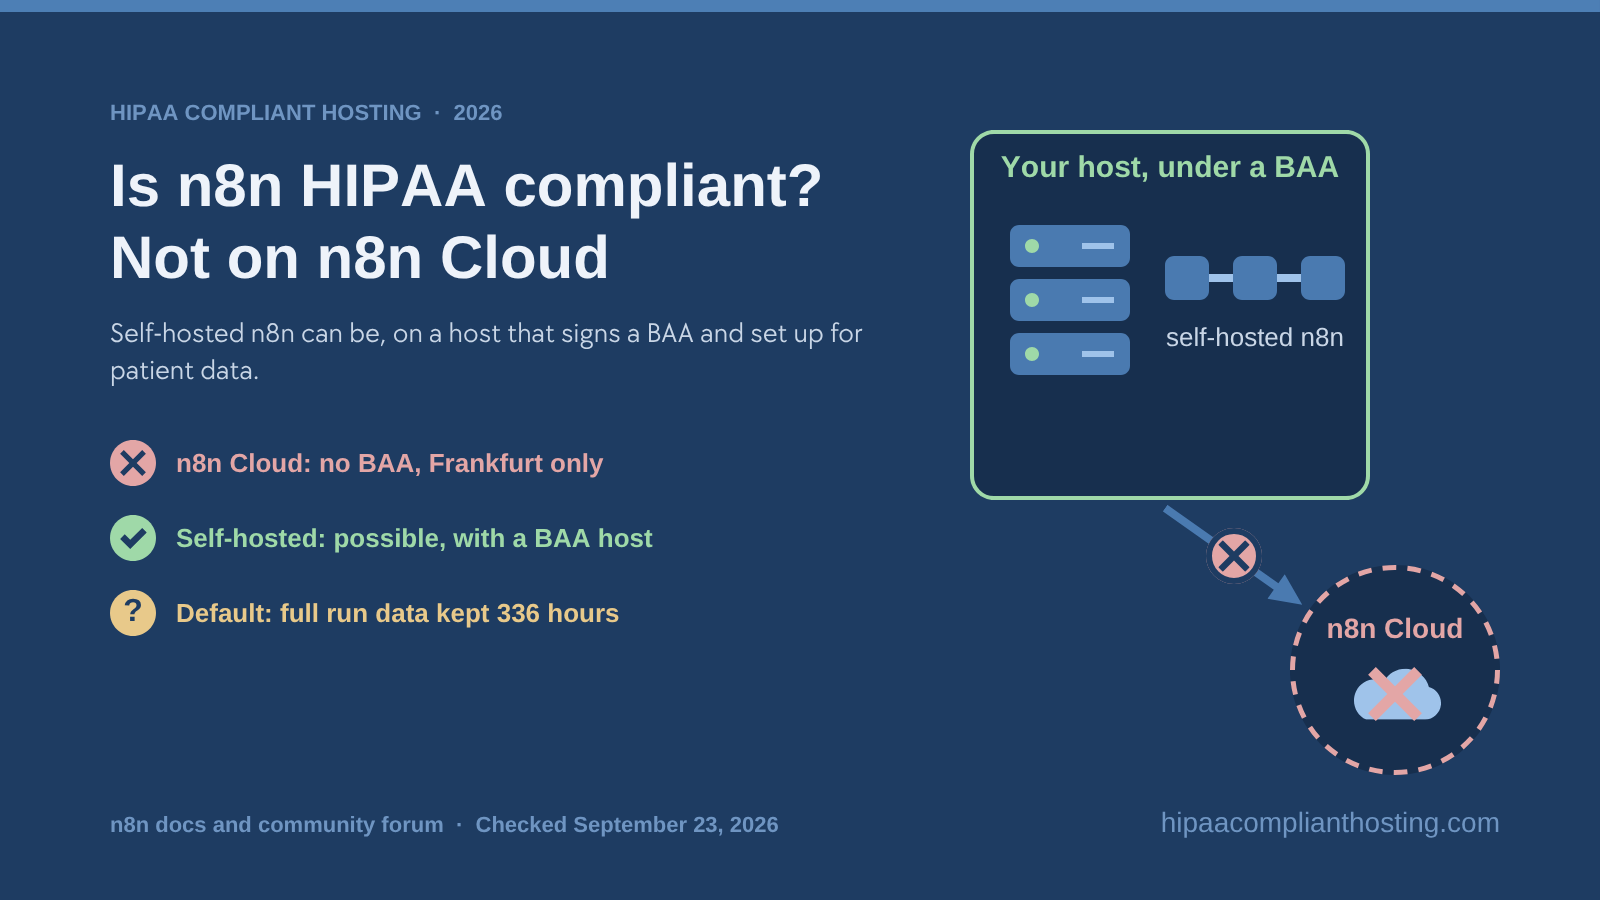
n8n is not HIPAA compliant on its own, and no automation tool is. HIPAA regulates the organizations that handle patient data, not their software. And n8n Cloud does not sign a Business Associate Agreement (BAA) as of September 28, 2026. So an n8n HIPAA compliant setup means self-hosted n8n, on a host that signs a BAA, set up for patient data. Clinics use n8n to move intake forms into an EHR, send reminders, and run AI summaries. By default, n8n saves the full input and output of every one of those runs. This guide shows where protected health information (PHI) lands inside n8n and which setting controls each spot. We sell HIPAA compliant hosting, so weigh our advice accordingly.
TL;DR: Quick answer
n8n Cloud does not sign a BAA, as n8n staff confirmed on January 19, 2026. It runs on Microsoft Azure in Frankfurt, Germany, with no US region listed.
Self-hosted n8n can be part of an n8n HIPAA compliant system. The host must sign a BAA under 45 CFR § 164.308(b), and the instance must be set up for PHI.
By default, n8n keeps the full data of every successful, failed, and manual run for 336 hours. Enterprise redaction hides it on screen and in the API, not in the database.
n8n encrypts only credentials. As of its September 2026 docs, webhooks are public, community nodes are on, and SSRF protection is off by default.
n8n fixed more than a dozen Critical flaws in 2026, including a 10.0 that needed no login, and 2.40.5 or later covers them all. The stable release is 2.40.7, from September 25, 2026.
Is n8n HIPAA compliant? The three-layer answer
Only as part of a larger system. n8n (pronounced "n eight n") comes from n8n GmbH in Berlin, founded in 2019. Most of its code is under the Sustainable Use License. It allows use for your own internal business purposes. Giving n8n to others is allowed only free of charge and for non-commercial purposes.
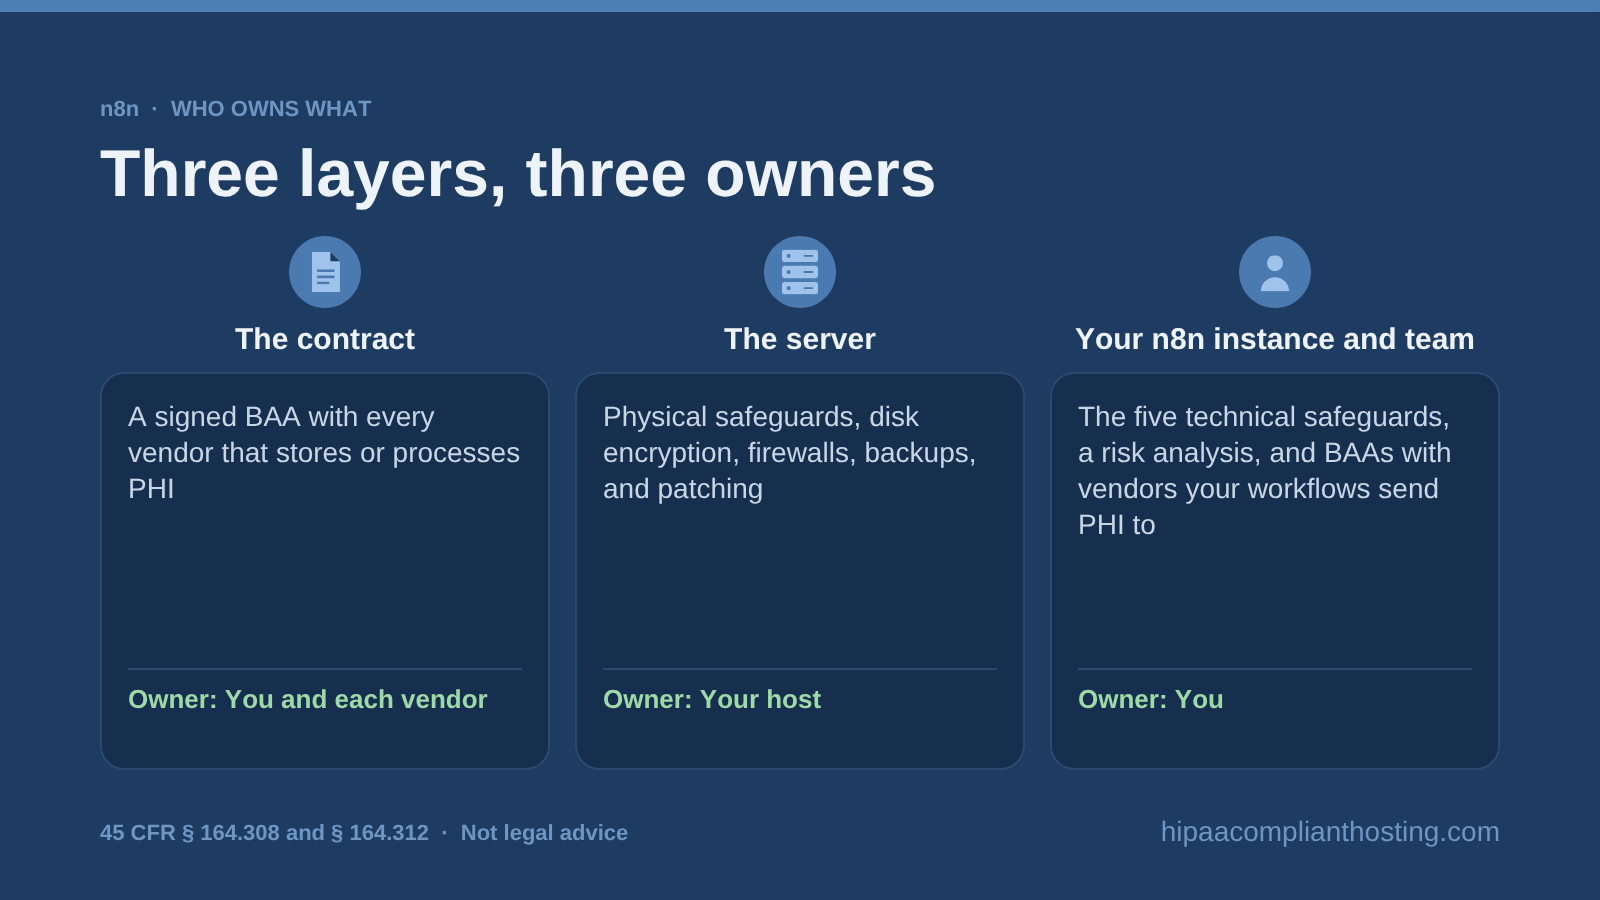
An n8n HIPAA compliant system has three layers, and each needs an owner. The first is the contract. A vendor that stores or processes PHI for a covered entity is a business associate. Under 45 CFR § 164.308(b), you need a signed BAA with that vendor first. Our HIPAA business associate agreement guide explains what it must cover. The second layer is the server. The host runs physical safeguards, disk encryption, firewalls, backups, and patching. The third layer is your n8n instance and your team. That covers the five technical safeguards in 45 CFR § 164.312 and a risk analysis under 45 CFR § 164.308(a)(1). It also covers a BAA with every vendor a workflow sends PHI to.
Does n8n Cloud sign a BAA?
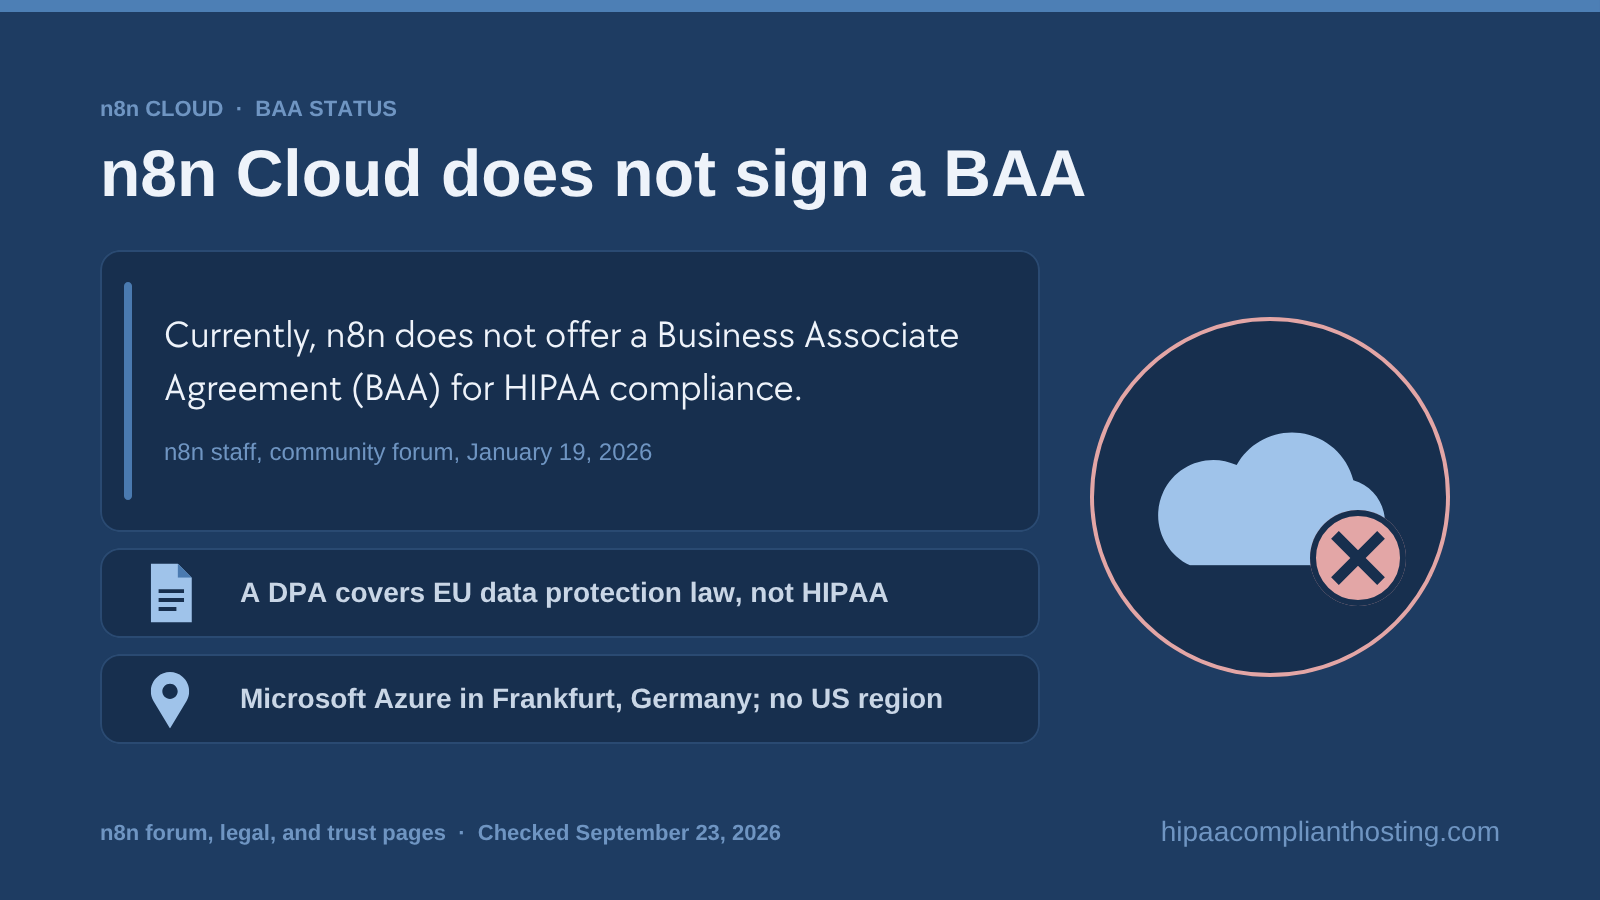
No. In a forum thread on BAAs for n8n Cloud, n8n staff answered on January 19, 2026. The answer was short: "Currently, n8n does not offer a Business Associate Agreement (BAA) for HIPAA compliance." Nothing newer was posted as of September 28, 2026. n8n's pricing, legal, DPA, security, and trust pages do not mention HIPAA or a BAA either. n8n offers a Data Processing Agreement (DPA), but a DPA covers EU data protection law, not HIPAA. So an n8n HIPAA compliant plan cannot run on n8n Cloud today.
n8n Cloud does have security paperwork. Its trust center lists SOC 2 Type 2, SOC 3, and GDPR. It runs on Microsoft Azure, with data stored on servers in Frankfurt, Germany. Daily backups go to a second region in the same country. n8n says more locations are coming, with no dates. Plans are priced in euros, billed yearly: Starter 20, Pro 50, and Business 667 per month. Business is listed as self-hosted, Enterprise is priced by sales, and we saw no US dollar prices.
The best-known alternatives answer the same way. Zapier says it does not support HIPAA and does not sign a BAA. For Make, we found no official statement. So switching tools does not solve the n8n HIPAA compliant problem. Our HIPAA compliant app hosting review lists hosted platforms that do sign.
Where does PHI land inside n8n?
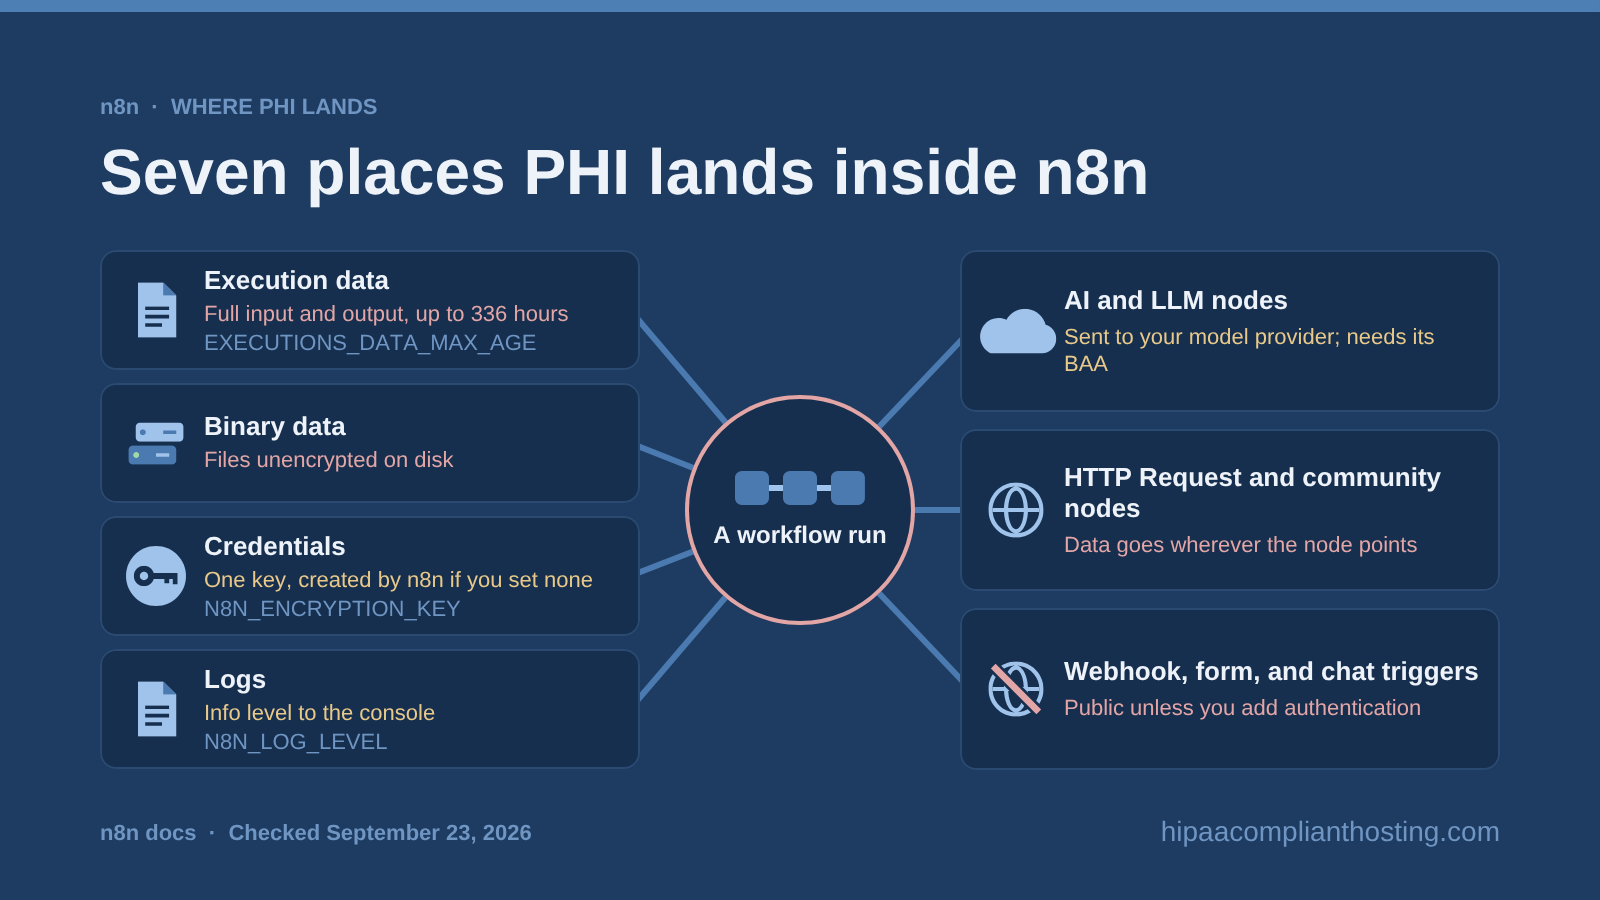
In seven places, and most are on by default. This table is the core of any n8n HIPAA compliant review. Self-hosted n8n is set up with environment variables. An environment variable is a named setting passed to n8n when the server starts. Each default below is from n8n's docs as of September 28, 2026.
Where PHI lands | What n8n does by default | Setting that controls it |
|---|---|---|
Execution data (each run's input and output) | Kept for successful, failed, and manual runs, up to 336 hours or 10,000 runs | EXECUTIONS_DATA_SAVE_ON_SUCCESS, EXECUTIONS_DATA_SAVE_ON_ERROR, EXECUTIONS_DATA_SAVE_MANUAL_EXECUTIONS, EXECUTIONS_DATA_MAX_AGE |
Binary data (PDFs, images, other files) | Unencrypted files on disk; n8n 2.x defaults to filesystem mode, though the docs page says memory | N8N_DEFAULT_BINARY_DATA_MODE; S3 or Azure storage needs Business or Enterprise |
Credentials | Encrypted with one key, created by n8n if you set none | N8N_ENCRYPTION_KEY |
Logs | Info level to the console; Code node print output kept out | N8N_LOG_LEVEL; CODE_ENABLE_STDOUT |
AI and LLM nodes | Prompts and context go to the model provider you pick | The provider's own BAA |
HTTP Request and community nodes | Data goes wherever the node points; community nodes allowed | N8N_COMMUNITY_PACKAGES_ENABLED; N8N_SSRF_PROTECTION_ENABLED |
Webhook, form, and chat triggers | Public unless the workflow adds authentication | Each trigger's authentication option |
Execution data needs the most care. EXECUTIONS_DATA_SAVE_ON_SUCCESS and EXECUTIONS_DATA_SAVE_ON_ERROR set whether n8n keeps data from runs that succeed or fail. EXECUTIONS_DATA_SAVE_MANUAL_EXECUTIONS covers test runs started in the editor. EXECUTIONS_DATA_MAX_AGE is how many hours a run is kept. The data sits in plain text, in a SQLite file unless you choose Postgres. For an n8n HIPAA compliant instance, these are the first settings to change.
N8N_ENCRYPTION_KEY is the secret key that encrypts stored credentials. If you set none, n8n creates one and saves it in its own folder. So a backup of that folder holds the credentials, the key, and the run data together. That breaks a basic rule of key management: keep a key apart from the data it protects. n8n's docs tell self-hosters to use encrypted partitions, the host's part of encryption at rest and in transit.
N8N_LOG_LEVEL sets how much detail n8n logs. CODE_ENABLE_STDOUT decides whether Code node print output goes to the server's log stream. Turn it on, and your log platform needs a BAA too.
What does n8n give you for the HIPAA technical safeguards?
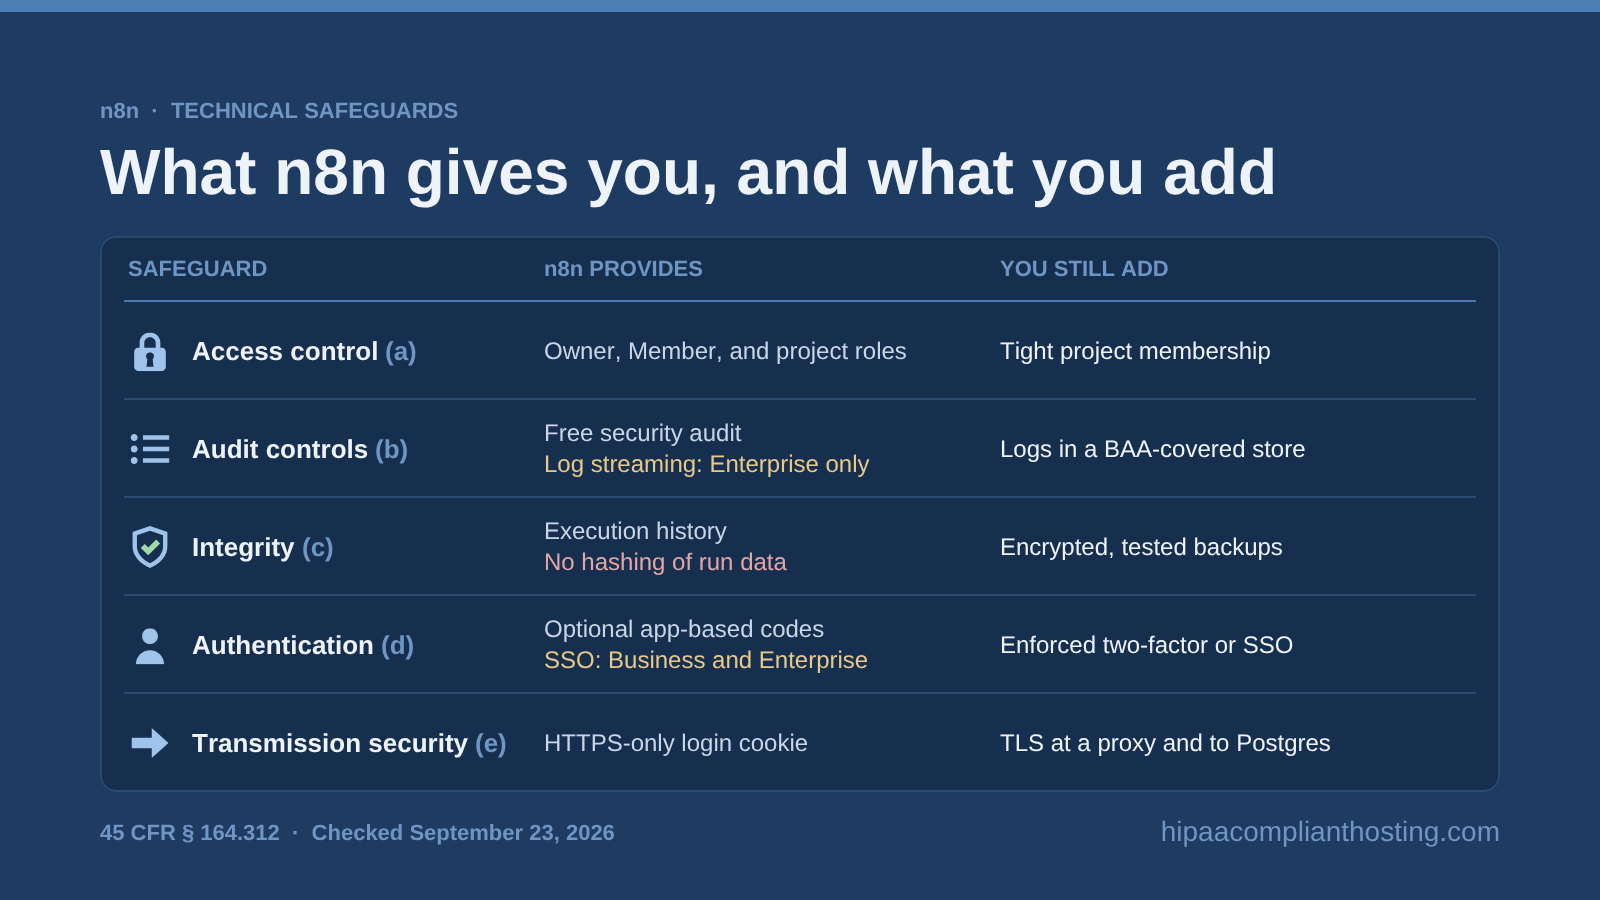
Parts of each, with the strongest controls on paid plans. Here is how self-hosted n8n maps to 45 CFR § 164.312. The last column is what an n8n HIPAA compliant instance still needs.
Safeguard (45 CFR § 164.312) | What n8n provides | What you still add |
|---|---|---|
Access control, (a) | Owner and Member roles and a project Admin role; the Admin instance role, project Editor and Viewer, and custom roles need Enterprise | Tight project membership, since Viewers can read executions |
Audit controls, (b) | A free security audit; audit events for logins, credentials, and workflows; log streaming on Enterprise only | Logs shipped to a BAA-covered store; n8n logs no ordinary run views, only Enterprise reveals of redacted data |
Integrity, (c) | Execution history; Git version control on Business and Enterprise; no hashing of run data | Encrypted, tested backups and change control |
Person or entity authentication, (d) | Email and password with optional app-based codes; SAML, OIDC, and LDAP on Business and Enterprise | Enforced two-factor or SSO, and shorter sessions |
Transmission security, (e) | An HTTPS-only login cookie by default | TLS at a reverse proxy, and TLS to Postgres, which is off by default |
For audit controls, the free n8n audit command flags unused credentials, risky nodes, and unprotected webhooks. Streaming audit events off the server needs Enterprise. Other teams set N8N_LOG_FORMAT, the log format, to json and collect container logs in a SIEM. An n8n HIPAA compliant audit trail should meet the bar in our entry on audit logging.
For authentication, N8N_MFA_ENABLED lets users turn on two-factor codes but does not require them. An n8n HIPAA compliant instance must require them. N8N_USER_MANAGEMENT_JWT_DURATION_HOURS, the login session length, defaults to 168 hours. Shorten it to fit your HIPAA automatic logoff policy. Business and Enterprise add SAML and OIDC single sign-on. N8N_SECURE_COOKIE sends the login cookie over HTTPS only. It defaults to true. Many setup guides say to turn it off. Do not do that on an n8n HIPAA compliant instance.
Which n8n defaults should you change before a workflow touches PHI?
Eleven, before any n8n HIPAA compliant go-live. None needs a paid license to change.
Setting | Default | Change it to |
|---|---|---|
Save data from successful runs (EXECUTIONS_DATA_SAVE_ON_SUCCESS) | all | none, or keep it with a short retention |
Hours before old runs are deleted (EXECUTIONS_DATA_MAX_AGE) | 336 | A few hours, or what your policy allows |
Database type (DB_TYPE) | sqlite | postgresdb, with DB_POSTGRESDB_SSL_ENABLED set to true |
Community nodes (N8N_COMMUNITY_PACKAGES_ENABLED) | true | false |
Block workflows from reading server variables (N8N_BLOCK_ENV_ACCESS_IN_NODE) | false | true |
Folders file nodes may use (N8N_RESTRICT_FILE_ACCESS_TO) | Empty, so no limit | One dedicated folder |
SSRF protection (N8N_SSRF_PROTECTION_ENABLED) | false | true |
Anonymous usage data to n8n (N8N_DIAGNOSTICS_ENABLED) | true | false |
Required two-factor login (N8N_MFA_ENFORCED_ENABLED) | false | true, from version 2.18.0 |
Public REST API (N8N_PUBLIC_API_DISABLED) | false, so the API is on | true, unless you use the API |
Task runner mode (N8N_RUNNERS_MODE) | Internal when unset; deprecated from n8n 3.0 | external |
In plain words, DB_POSTGRESDB_SSL_ENABLED encrypts the link to Postgres. N8N_BLOCK_ENV_ACCESS_IN_NODE blocks workflows from reading server variables, such as the encryption key. N8N_RESTRICT_FILE_ACCESS_TO lists the only folders file nodes may use. SSRF, or server-side request forgery, tricks your server into calling addresses inside your network. N8N_SSRF_PROTECTION_ENABLED, added in 2.12.0, checks node requests against a block list of private ranges. N8N_DIAGNOSTICS_ENABLED sends anonymous usage data to n8n every six hours. N8N_RUNNERS_MODE sets where Code node scripts run. The docs call internal mode insecure by design.
Which n8n versions are safe to run?
Only a current, patched release. As of September 28, 2026, the stable release is 2.40.7, from September 25. n8n ships a minor version about weekly and patches the two newest 2.x lines at once. The 1.x line still got a security fix, 1.123.80, in September 2026. n8n publishes no end-of-life calendar, so record your version in your risk analysis.
Advisory | What it allowed | Severity | Fixed in |
|---|---|---|---|
CVE-2026-21858 (January 7, 2026) | File access with no login, through forms and webhooks | Critical, 10.0 | 1.121.0 |
CVE-2026-21877 (January 6, 2026) | Code execution through the Git node | Critical, 9.9 | 1.121.3 |
CVE-2026-1470 (January 27, 2026) | Code execution through workflow expressions | Critical, 9.9 | 1.123.17, 2.4.5, and 2.5.1 |
CVE-2026-25049 (February 4, 2026) | Code execution by escaping an expression | Critical, 9.4 | 1.123.17 and 2.5.2 |
GHSA-9rhv-fhr8-7q5r (September 16, 2026) | Any project member could decrypt any credential | High, 8.3 | 2.39.6 and 2.40.1 |
GHSA-w24g-6454-7w7f (September 16, 2026) | Reading other users' chat history with no login | High, 7.0 | 1.123.80, 2.39.6, and 2.40.1 |
Any 1.x version below 1.123.17 is open to both expression flaws. The 10.0 flaw needed no login and came through public forms and webhooks, where intake data arrives. An n8n HIPAA compliant instance on 2.40.5 or later is covered for all six, and for every other Critical n8n flaw GitHub listed in 2026.
The 9 settings that make a self-hosted n8n instance HIPAA-ready
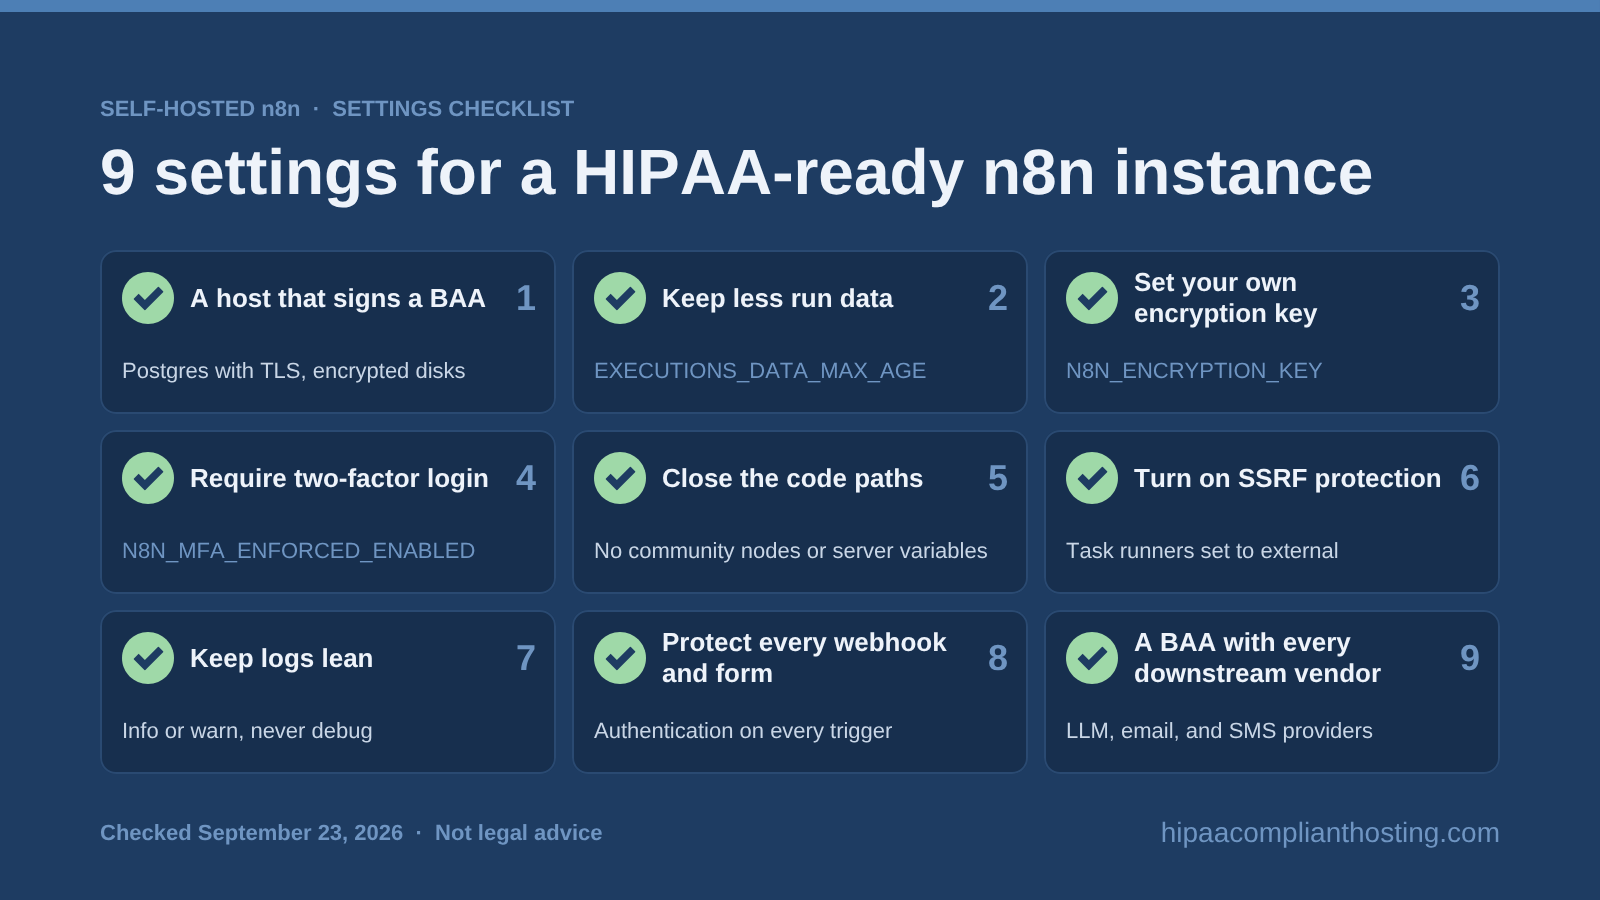
These are the first settings we check in n8n HIPAA compliant reviews. Each maps to the defaults above.
Run on a host that signs a BAA. Use Postgres with TLS, not SQLite, on encrypted disks.
Keep less run data. Set
EXECUTIONS_DATA_SAVE_ON_SUCCESSto none, or cutEXECUTIONS_DATA_MAX_AGEto hours. KeepEXECUTIONS_DATA_PRUNE, which deletes old runs, at true.Set your own encryption key. Load
N8N_ENCRYPTION_KEYfrom a secrets manager.N8N_ENV_FEAT_ENCRYPTION_KEY_ROTATIONturns on key rotation. The docs call that a one-way change, so back up the database first.Require two-factor login. Set
N8N_MFA_ENFORCED_ENABLEDandN8N_SECURITY_POLICY_MANAGED_BY_ENVto true. The second locks the policy at each start. Or use SSO on Business or Enterprise.Close the code paths. Set
N8N_COMMUNITY_PACKAGES_ENABLEDto false andN8N_BLOCK_ENV_ACCESS_IN_NODEto true.Turn on SSRF protection and external task runners. Set
N8N_SSRF_PROTECTION_ENABLEDto true andN8N_RUNNERS_MODEto external.Keep logs lean. Set
N8N_LOG_LEVELto info or warn, never debug in production. Ship logs only to a BAA-covered destination.Protect every webhook and form. Add authentication or a header check to each trigger. Put the instance behind a reverse proxy with TLS.
Sign a BAA with every downstream vendor. That means LLM, email, and SMS providers a node sends PHI to. If one will not sign, keep PHI out of that node.
For item 1 on AWS, see Amazon RDS HIPAA compliant and HIPAA compliant database hosting. With all nine in place, most n8n HIPAA compliant work inside the instance is done. If you run n8n in Docker, the container layer needs the same care; our guide to whether Docker HIPAA compliant setups are possible covers logs, secrets, and images.
Where do n8n workflows leak PHI?
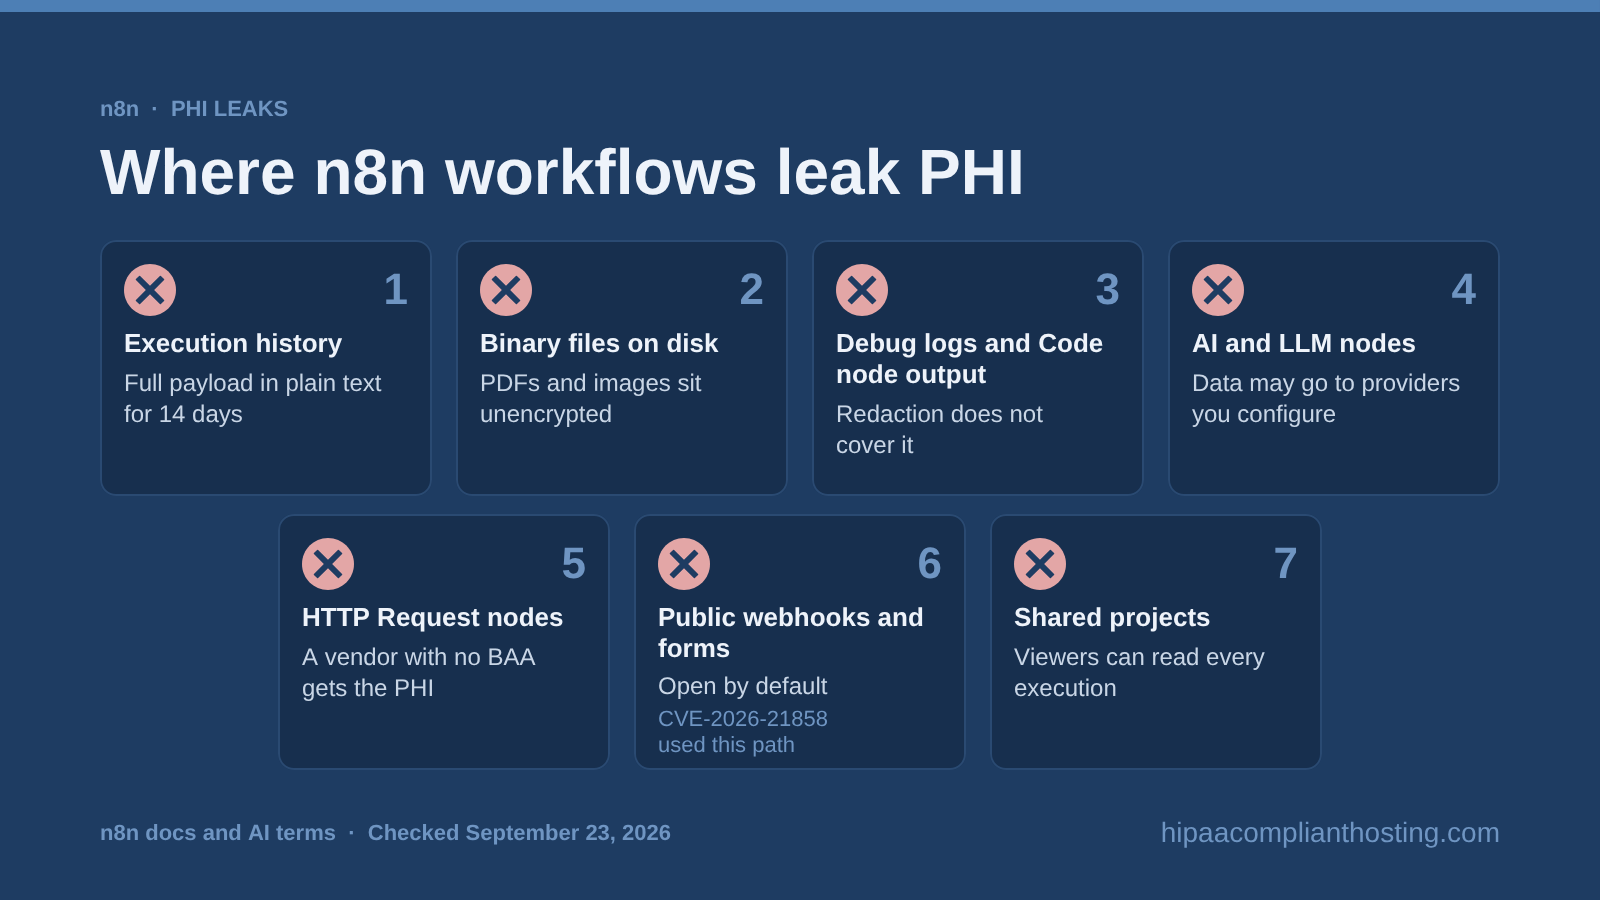
Mostly in places nobody treats as storage. These are the leaks we see most in n8n HIPAA compliant reviews.
Execution history. Every saved run holds the full payload in plain text for 14 days by default. Database backups copy it again.
Binary files on disk. Uploaded PDFs and images sit unencrypted in n8n's storage folder, or binaryData on older installs, unless the disk is encrypted.
Debug logs and Code node output. Print output reaches the log stream when
CODE_ENABLE_STDOUTis on. Redaction does not cover it.AI and LLM nodes. n8n's AI terms say customer data may go to the providers you configure. n8n's template gallery even has a patient intake workflow that uses an LLM.
HTTP Request nodes. A request to a vendor with no BAA sends PHI to that vendor.
Public webhook and form endpoints. They are open by default, and CVE-2026-21858 used this path.
Shared projects. A Project Viewer can read every execution in the project.
An n8n HIPAA compliant workflow keeps PHI out of any node whose vendor has not signed. Reminder workflows often end in an email step, so see HIPAA compliant email. SMS reminders also need opt-in consent and minimal PHI in the message, as our guide to HIPAA compliant texting explains. If a headless CMS form feeds n8n, see Payload CMS HIPAA compliant and Strapi HIPAA compliant.
Who signs the BAA for an n8n instance, and what does it cost?
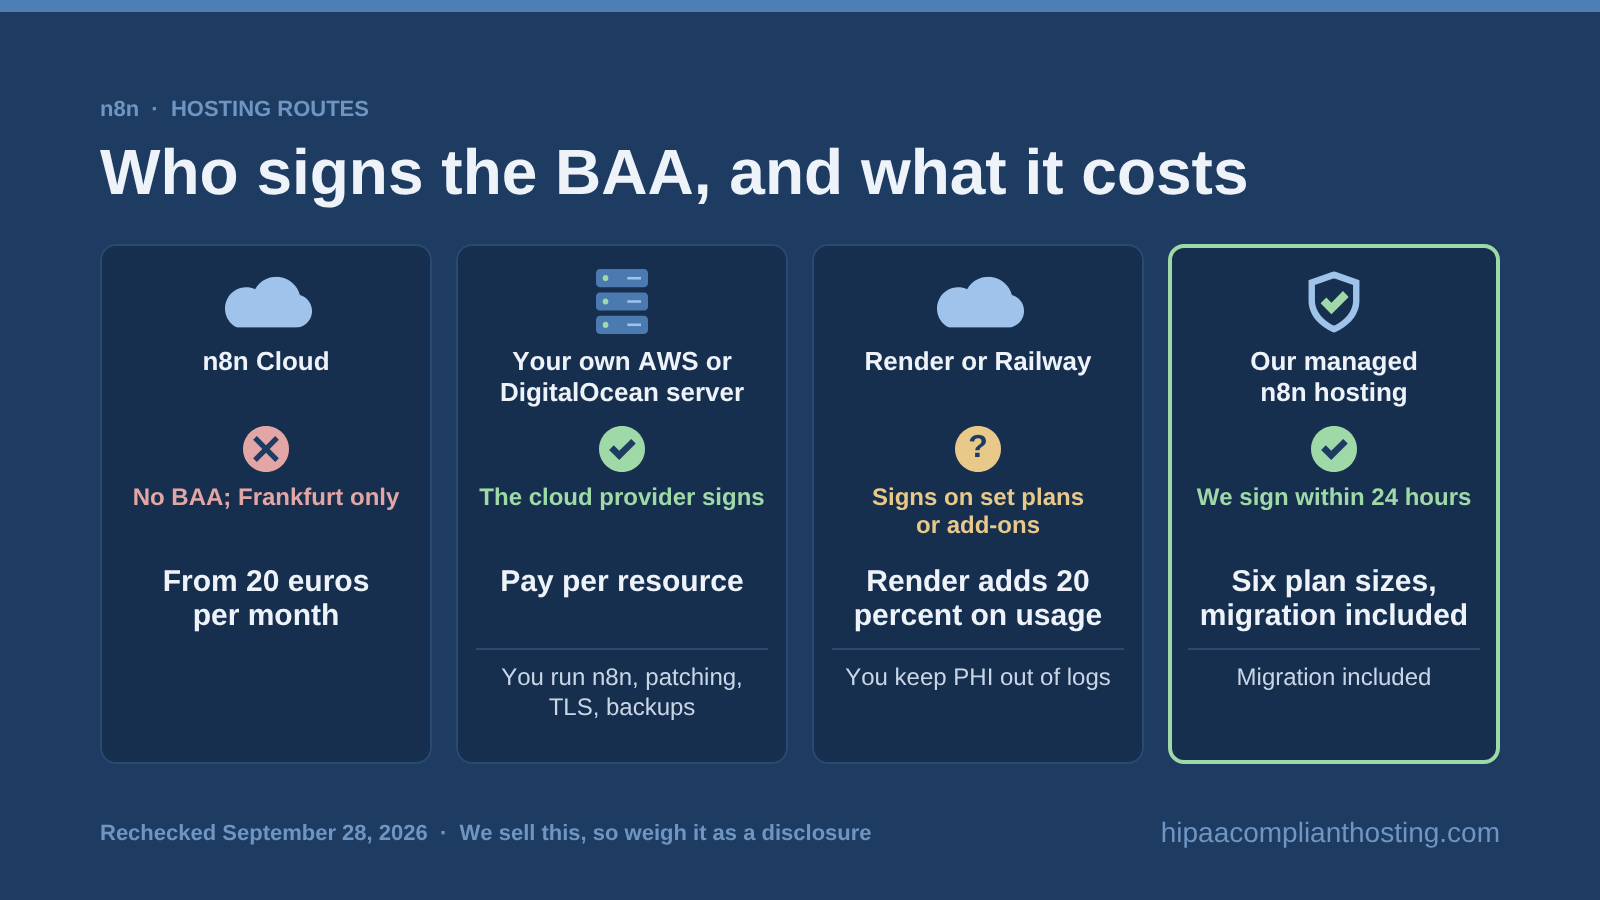
Your host does, since n8n will not. Every vendor in the path needs a signed Business Associate Agreement (BAA). Here are the routes as rechecked on September 28, 2026.
Route | Published starting point | Who signs the BAA | What you still own |
|---|---|---|---|
n8n Cloud | From 20 euros per month, billed yearly | No one; Frankfurt only | Not a PHI route |
Your own AWS server or DigitalOcean Droplet | Pay per resource | The cloud provider; DigitalOcean lists Droplets as eligible, not Managed Databases or App Platform | All n8n settings, Postgres, patching, TLS, logs, and backups |
Render or Railway | Render: Scale or Enterprise plan plus 20 percent on usage; Railway: a BAA add-on with a monthly spend threshold | The platform, under those terms | All n8n settings, and PHI-free logs |
HIPAA compliant n8n hosting from us | Six plan sizes, migration included | Us, within 24 hours | Your workflows, credentials, connected vendors, and their BAAs |
We sell the last row, so weigh it as a disclosure. DigitalOcean's one-click n8n image comes from a third party, and the BAA covers the Droplet, not the image's setup. Render bars PHI from all service logs. For the AWS route, our answer on whether AWS HIPAA compliant hosting is enough covers what AWS's BAA leaves to you. An n8n HIPAA compliant budget should count the engineer's hours, not just the server.
If you would rather not run the n8n server yourself
Most clinics want working automations, not a server to patch every week. Our HIPAA compliant n8n hosting runs self-hosted n8n on a single-tenant AWS environment. We run the AWS account, network isolation, server patching, the n8n process, version updates, and TLS. CloudFront, a web application firewall, encryption, six-year audit logs, and backups come with every tier. You keep your workflows, credentials, connected systems, and any community nodes you install. That puts an n8n HIPAA compliant setup under one host and one BAA. The BAA is signed within 24 hours, before patient data moves. Plans come in six sizes, from Starter to Network, with migration included. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your workflows never carry patient identifiers, HIPAA does not reach them, and you do not need us. If a platform engineer runs n8n on AWS under AWS's BAA, that path works and costs less in cash. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your workflows do and get a straight answer.
Frequently asked questions
Is n8n HIPAA compliant?
Not by itself, and no software is. An n8n HIPAA compliant setup needs self-hosting on a host that signs a BAA. It also needs short or no saved run data, enforced two-factor login, protected webhooks, and BAAs with connected vendors.
Does n8n Cloud sign a BAA?
No. n8n staff confirmed on January 19, 2026 that n8n offers no BAA. No n8n pricing, legal, or trust page mentioned one on September 28, 2026. n8n Cloud also runs only in Frankfurt, Germany.
Is self-hosted n8n HIPAA compliant?
It can be part of an n8n HIPAA compliant system. The host signs a BAA and encrypts the disks. You change the risky defaults and run a risk analysis. Every connected vendor that receives PHI signs a BAA too.
Does n8n store the data that passes through workflows?
Yes, by default. n8n saves the full input and output of successful, failed, and manual runs for 336 hours, or up to 10,000 runs. The data sits in plain text. For an n8n HIPAA compliant setup, turn saving off or shorten retention.
Can I use n8n AI nodes with patient data?
Only if the model provider signs a BAA with you. n8n's AI terms say customer data may go to the providers you configure. An n8n HIPAA compliant workflow sends PHI only to providers that sign.
Recap: n8n HIPAA compliant
To recap, an n8n HIPAA compliant setup is self-hosted, because n8n Cloud signs no BAA and runs only in Frankfurt. The host signs the BAA and encrypts the disks. You cut saved run data, set your own key, require two-factor login, and close community nodes and environment access. Turn on SSRF protection, protect every webhook, run 2.40.5 or later, and get a BAA from every connected vendor.
This article is general information, not legal advice. Versions, defaults, and plan terms change often. Facts reflect n8n's docs, legal pages, forum, and GitHub advisories as read on September 22, 2026. Key items were rechecked on September 23 and September 28, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed September 2026.
Sources
n8n: Pricing, Legal, Security, AI Terms, and Trust Center.
n8n community: BAA agreement for n8n Cloud.
n8n docs, environment variables: Executions, Security, Deployment, Logs, and Database.
More environment variables: Binary data, Nodes, SSRF protection, and User management and 2FA.
n8n docs, security: Security policies, Redact execution data, Security audits, and Rotate encryption keys.
More security docs: SSRF protection, SSO, Task runners, and Privacy and security.
n8n docs, administration: Project roles, Log streaming, Backup and restore, and Community node risks.
n8n on GitHub: License, Releases, Security advisories, and Binary data config.
Advisories: CVE-2026-21858, CVE-2026-21877, CVE-2026-1470, CVE-2026-25049, GHSA-9rhv-fhr8-7q5r, and GHSA-w24g-6454-7w7f.
Hosts: Render HIPAA compliance, Railway compliance, DigitalOcean HIPAA, and the DigitalOcean n8n Marketplace listing.
Alternatives: Is Zapier HIPAA compliant?
45 CFR § 164.312 (technical safeguards): law.cornell.edu.
45 CFR § 164.308 (administrative safeguards, BAA requirement): ecfr.gov.