


Is Slim Framework HIPAA Compliant? What a Micro-Framework Leaves to You (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-slim-framework-hipaa-compliant
Last updated: October 22, 2026
Slim is not HIPAA compliant on its own, and no framework is. HIPAA regulates the organizations that handle patient data, not the code they use. Slim also gives you less to start with than most frameworks. Its own docs describe it as a dispatcher that takes a request, runs your code, and returns a response. So a Slim Framework HIPAA compliant app is mostly what you add. You pick middleware for login, CSRF, sessions, rate limits, and audit logs. You encrypt PHI with a library. And you run on a host that signs a Business Associate Agreement (BAA). None of that is a problem if you plan it. This guide covers what Slim 4 includes, what to add, and which versions to run. Every Slim fact was checked again against Slim's docs and GitHub on October 20, 2026. The PHP patch note was checked on php.net on October 22, 2026.
TL;DR: Quick answer
Slim 4 ships routing, PSR-15 middleware, and six packaged middleware: routing, error handling, method overriding, output buffering, body parsing, and content length.
Slim's docs have no sections on security, login, sessions, CSRF, or encryption. You add each one through middleware or a library.
Slim's own CSRF middleware, Slim-Csrf, is still maintained. The popular JWT login middleware tuupola/slim-jwt-auth is archived.
Slim 4.15.3, released September 1, 2026, is still the latest release on October 20, 2026. It fixed a route constraint bypass. Slim 4.15.2 fixed an error page XSS flaw in May 2026. PHP itself also needs its October 21, 2026 security release: 8.5.12, 8.4.27, 8.3.36, 8.2.35, or your distribution's patched package.
Slim has no official hosting product, so no Slim vendor signs a BAA. Your host must.
Our HIPAA compliant Slim hosting runs your API on a single-tenant AWS server from $229 per month. We sign the BAA within 24 hours of signup, before patient data moves.
Is Slim Framework HIPAA compliant? The three-layer answer
A Slim Framework HIPAA compliant system has three layers, and each one needs an owner. The first is the contract. Any vendor that stores or processes protected health information (PHI) for a covered entity is a business associate under 45 CFR § 160.103. Under 45 CFR § 164.308(b), you need a signed BAA with that vendor first. Our HIPAA business associate agreement guide explains what it must cover.
The second layer is the server. The data center runs the physical safeguards. Disk encryption, firewalls, backups, and patching sit here too. Check which of these your host runs and which fall to your own engineer. The third layer is your app and your team. The HIPAA Security Rule lists five technical safeguards in 45 CFR § 164.312. They are access control, audit controls, integrity, person or entity authentication, and transmission security. Slim provides the pipeline where those controls run, but not the controls. You also run a risk analysis under 45 CFR § 164.308(a)(1). Teams often choose Slim for small APIs behind a mobile app or a JavaScript front end. That is exactly where the Slim Framework HIPAA compliant work matters, because the API is the door to the data.
What does Slim 4 give you for the HIPAA technical safeguards?
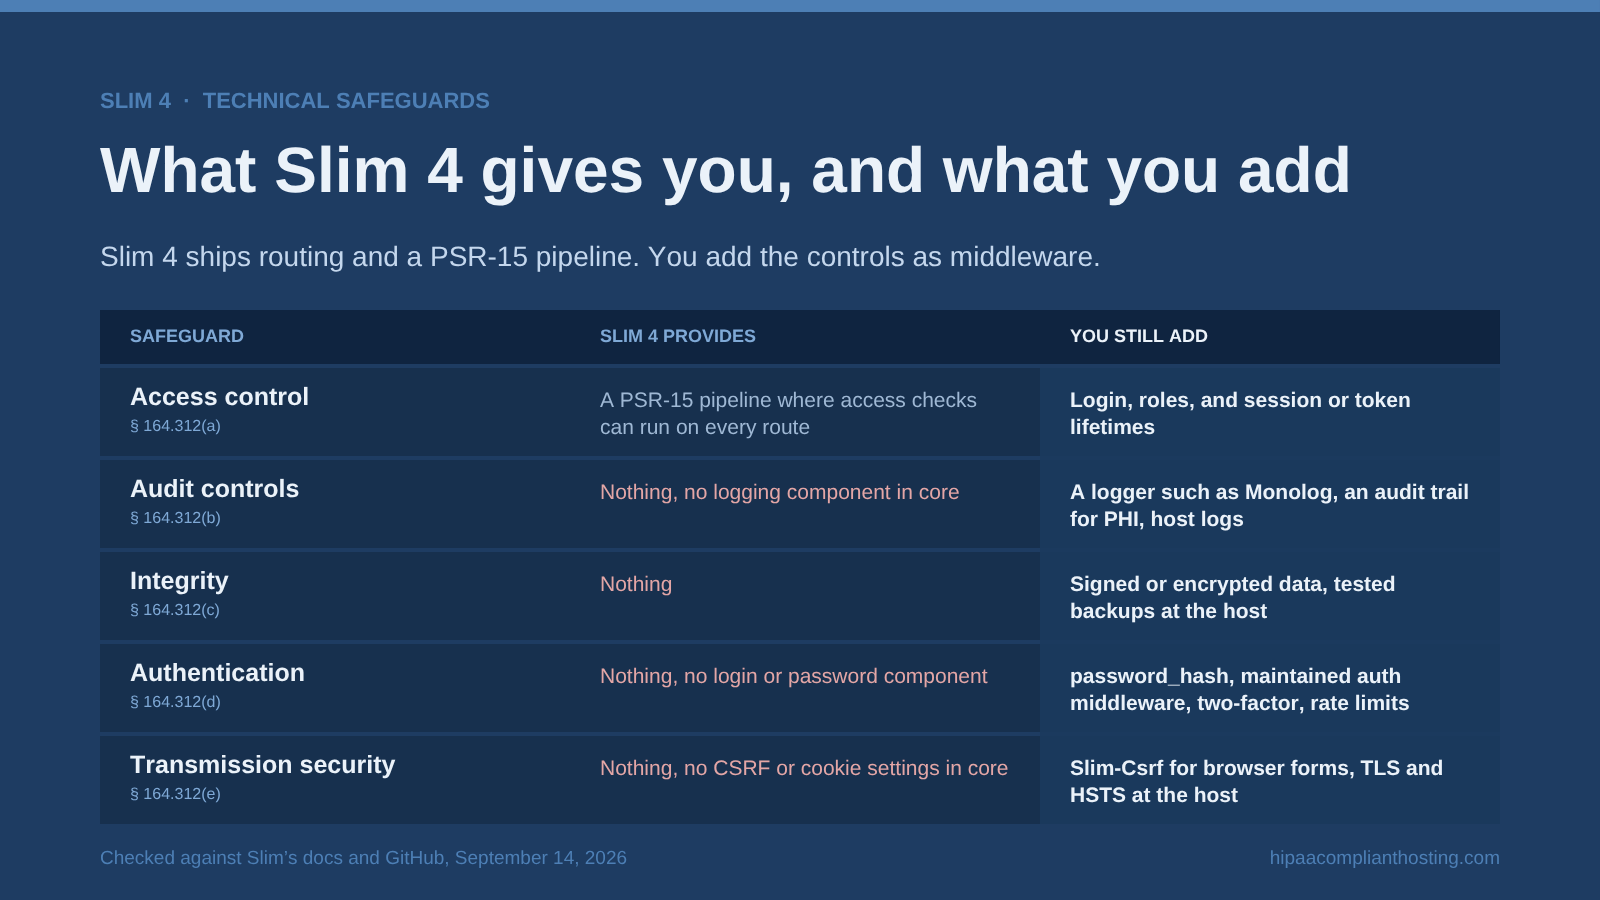
Very little by design. Here is how Slim 4 maps to each rule in 45 CFR § 164.312. The last column is what a Slim Framework HIPAA compliant API still needs from you or your host.
Safeguard (45 CFR § 164.312) | What Slim 4 provides | What you still add |
|---|---|---|
Access control, (a) | A PSR-15 middleware pipeline where access checks can run on every route | Login, roles, and session or token lifetimes |
Audit controls, (b) | Nothing; no logging component in core | A logger such as Monolog, an audit trail for PHI, and server logs from the host |
Integrity, (c) | Nothing | Signed or encrypted data where needed, and tested backups at the host |
Person or entity authentication, (d) | Nothing; no login or password component | PHP's password_hash, a maintained auth middleware, two-factor login, and rate limits |
Transmission security, (e) | Nothing; no CSRF or cookie settings in core | Slim-Csrf for browser forms, TLS and HSTS at the host |
That table looks bleak, but it is not a flaw. Slim's middleware docs say middleware is the place for authentication, authorization, logging, and CSRF protection. The work is choosing packages that are still maintained. Slim-Csrf, the official CSRF middleware, has about 350 GitHub stars and is not archived. Its latest release, 1.5.1, came out on November 5, 2025. The popular tuupola/slim-jwt-auth, with about 820 stars, is archived and was last updated in September 2024. A Slim Framework HIPAA compliant API should not depend on an archived login package. Choose any maintained PSR-15 middleware and a maintained JWT library instead. Audit trails need the same care. Our glossary entry on audit logging explains what to record, and our guide to HIPAA audit logs covers how long to keep them.
Those empty cells are the price of a micro-framework, and they are not Slim's alone. The same rows come up in our guide to whether Flight PHP HIPAA compliant apps are possible.
A full-stack framework fills a few of them in before you write any code. Laravel ships encrypted casts and Fortify two-factor login, and Symfony ships firewalls and login throttling. Neither ships an audit log either, so that row stays yours whichever way you go.
Phalcon 5 fills the encryption row too. It ships signed encryption and a deny-by-default ACL, but it runs as a compiled C extension. That needs a host willing to build and patch the extension, which our guide to whether Phalcon HIPAA compliant apps are possible works through.
Which Slim versions are safe to run?
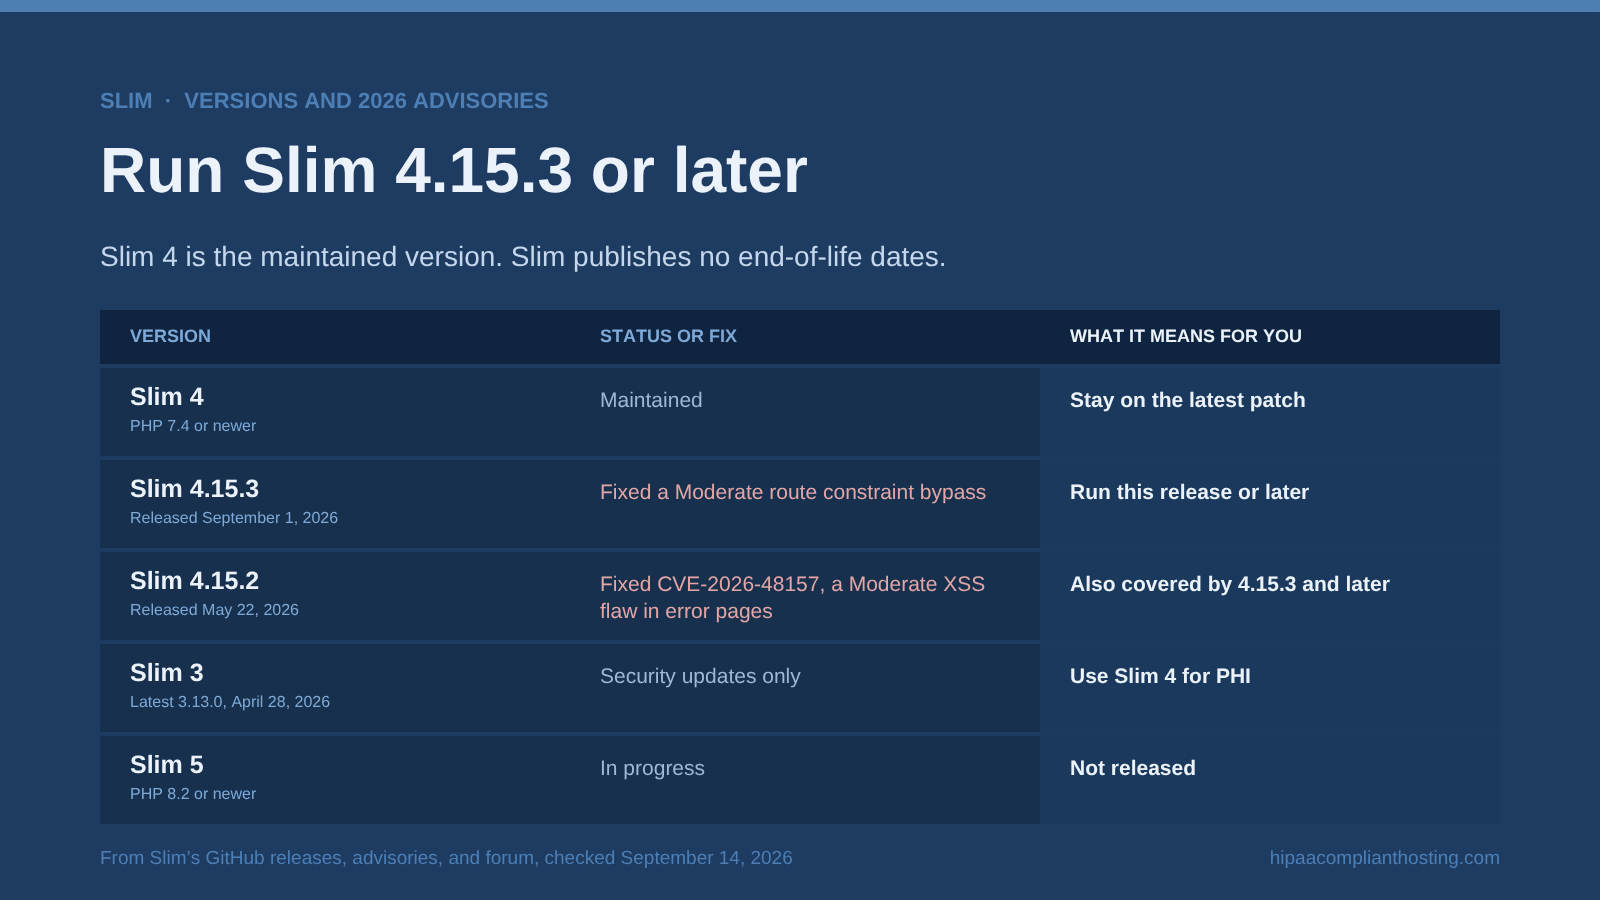
A current Slim 4 release. Slim's maintainers said on the official forum that Slim 4 is the maintained version. They said Slim 3 only receives security updates. Slim publishes no end-of-life dates. For a Slim Framework HIPAA compliant app, that means Slim 4 on its latest patch.
Version | Status on October 20, 2026 | Latest release |
|---|---|---|
Slim 3 | Security updates only, per the maintainers | 3.13.0, April 28, 2026 |
Slim 4 | Maintained; PHP 7.4 or newer | 4.15.3, September 1, 2026 |
Slim 5 | In progress; PHP 8.2 or newer | Not released |
Two 2026 Slim advisories matter. Slim 4.15.2, from May 22, fixed CVE-2026-48157. That Moderate XSS flaw hit error pages when untrusted data reached an exception's title or description. The advisory says hiding error details does not block it. Update, or keep request data out of error titles and descriptions. Slim 4.15.3, from September 1, fixed a Moderate route constraint bypass through double percent-encoding. No newer Slim advisory had been published by October 20, 2026. Record your version and patch cadence in your HIPAA risk analysis. List your auth middleware versions there too, because login packages get their own advisories. In August 2026, a Critical flaw hit the cookie login in CakePHP's first-party Authentication plugin. Our guide to CakePHP HIPAA compliant apps shows the plugin update and cookie setting that close it.
Slim patches do not cover flaws in PHP itself, so run PHP 8.5.12, 8.4.27, 8.3.36, 8.2.35, or a newer patch. The PHP project released those versions on October 21, 2026. They fix two critical flaws, CVE-2026-109618 and CVE-2026-109619, that can allow unauthenticated remote code execution. If you install PHP from your Linux distribution, apply its updated package instead, since php.net says distributions received the patches in advance. PHP 8.1 and older no longer receive updates from the PHP project, so upgrade to one of the patched releases above. PHP 8.2 reaches end of life on December 31, 2026, so pick 8.3.36, 8.4.27, or 8.5.12 when you upgrade.
The 7 settings that make a Slim API HIPAA-ready
Work through these seven settings before a Slim Framework HIPAA compliant API takes real patient data.
Run Slim 4.15.3 or later on patched PHP. That covers both 2026 Slim advisories. Slim does not fix PHP itself, so also run PHP 8.5.12, 8.4.27, 8.3.36, 8.2.35, a newer patch, or your distribution's patched package.
Hide error details in production. Turn off error detail display in the error middleware, so stack traces never reach users.
Add a maintained auth middleware to every PHI route. Avoid archived packages. Use short token lifetimes.
Hash passwords with password_hash. Slim has no password component, so use PHP's built-in function with bcrypt or Argon2id.
Add Slim-Csrf for any browser form. APIs that only accept tokens in headers need strict CORS rules instead.
Encrypt PHI fields with libsodium. Keep the key outside the code and the web root.
Log who touched PHI, and rate-limit login. Wire a logger through middleware, keep PHI out of log lines, and add a PSR-15 rate limiter or a host firewall rule.
Short token lifetimes tie to HIPAA automatic logoff. Two-factor login for staff ties to HIPAA MFA requirements. With all seven in place, most Slim Framework HIPAA compliant work inside the app is done.
Where do Slim apps leak PHI?
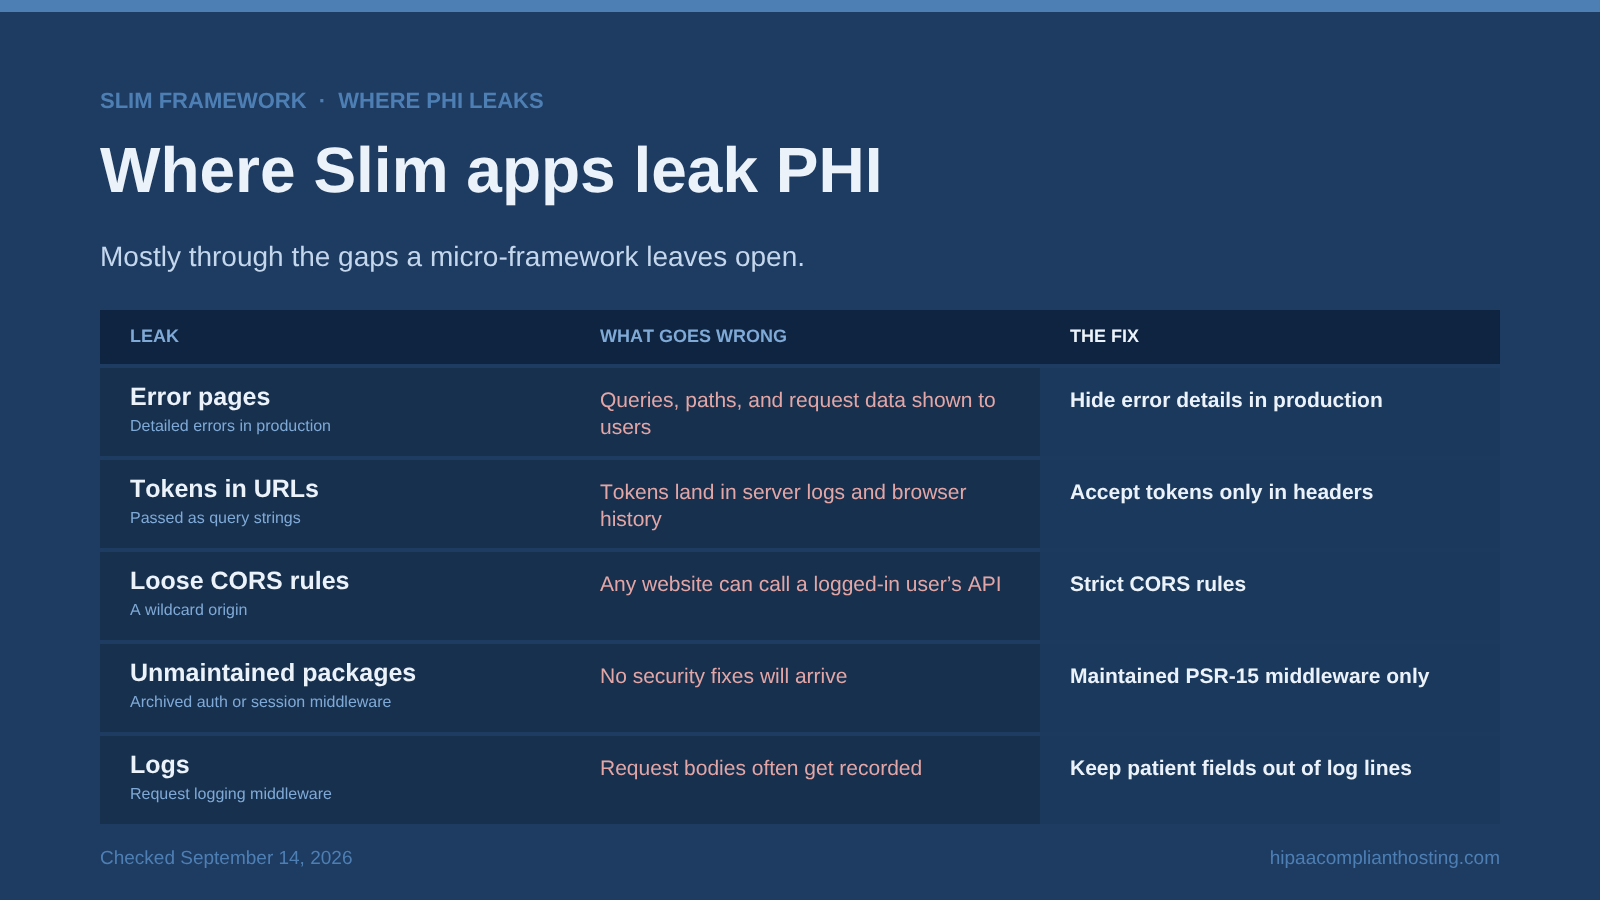
Mostly through the gaps a micro-framework leaves open. Close these five paths before a Slim Framework HIPAA compliant API goes live.
Error pages. Detailed errors in production can show queries, paths, and request data.
Tokens in URLs. Tokens passed as query strings end up in server logs and browser history.
Loose CORS rules. A wildcard origin lets any website call a logged-in user's API.
Unmaintained packages. Archived auth or session middleware will not get security fixes.
Logs. Request logging middleware often records bodies. Keep patient fields out.
Developers carry much of this duty in a micro-framework. The basics are in HIPAA training for web developers.
Who signs the BAA for a Slim app, and what does it cost?
Your host does. Slim has no official hosting product, so no Slim vendor signs a BAA. A Slim Framework HIPAA compliant budget starts with a host that will. As of October 20, 2026, AWS lets you accept its BAA in AWS Artifact. DigitalOcean offers a BAA on request for its HIPAA-eligible products: new customers contact Sales, and existing customers contact Support. If your Slim API runs on AWS Lambda, the settings are in our guide to whether AWS Lambda HIPAA compliant setups are possible. Other hosts that sign a BAA are compared in our guide to the best HIPAA compliant hosting providers.
Route | Published starting point | Who signs the BAA | What you still own |
|---|---|---|---|
Your own AWS or DigitalOcean server | Pay per resource | The cloud provider: AWS in AWS Artifact, DigitalOcean on request | Firewall, encryption, audit logs, backups, and the engineer's hours |
Managed HIPAA cloud hosting from us | From $229 per month, 4 hours of migration and configuration included | Us, within 24 hours of signup | Your middleware choices, app code, and risk analysis |
We sell the second row, so weigh it as a disclosure.
If you would rather not host your Slim API yourself
A Slim API is small, but the server under it is not. Our HIPAA compliant Slim hosting runs Slim Framework HIPAA compliant APIs on a single-tenant AWS server, encrypted at rest and in transit. Every plan includes a web application firewall, CloudFront CDN, six-year audit logging, and tested encrypted backups. EBS storage keeps snapshots for 7 days. The BAA is signed within 24 hours of signup, before patient data moves. Our BAA covers the servers and services we run.
Plans start from $229 per month, with 4 hours of migration and configuration included in the first month. After that, work is $175 an hour, quoted before work starts. Monthly plans have no long-term contract. Containerized APIs fit our HIPAA compliant Docker hosting, which starts from $259 per month. Our guide to whether Docker HIPAA compliant setups are possible covers what a container host must settle first. That list runs from a daemon that runs as root by default to the registry your images sit in. You keep Slim and your middleware. Before you sign with any host, us included, confirm in writing who applies PHP security releases. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your Slim API never handles PHI for a covered entity, HIPAA does not apply, and you do not need us. If your team runs AWS under AWS's BAA with an engineer who owns the server, that works and costs less in cash. Know our limits too. Each plan is one server in one AWS availability zone, and a multi-zone design is quoted separately. Root access comes only through an Enterprise engagement. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your API serves and get a straight answer.
Frequently asked questions
Is Slim Framework HIPAA compliant?
No framework is HIPAA compliant by itself. A Slim Framework HIPAA compliant API needs a host that signs a BAA. It also needs maintained auth middleware, password hashing, CSRF or strict CORS, field encryption, rate limits, and an audit trail. Slim 4 provides the middleware pipeline, not those controls.
Does Slim 4 have built-in authentication?
No. Slim 4 has no login or password component. Its docs point to middleware for authentication. Use a maintained PSR-15 auth middleware, and avoid tuupola/slim-jwt-auth, which is archived.
Does Slim have CSRF protection?
Not in core. Slim's official Slim-Csrf package adds CSRF middleware. Its latest release, 1.5.1, came out on November 5, 2025. APIs that accept tokens only in headers usually rely on strict CORS rules instead.
Is Slim 3 end of life?
Slim's maintainers say Slim 4 is the maintained version and Slim 3 receives security updates only. No end-of-life date is published. The latest Slim 3 release was 3.13.0, on April 28, 2026. It requires PHP 8.1 or newer and runs on PHP up to 8.5. Use Slim 4 for PHI.
Is Slim 5 released?
Not as of October 20, 2026. Slim's road map lists Slim 5 as in progress on its 5.x branch, and it needs PHP 8.2 or newer. No Slim 5 release has been tagged on GitHub. Keep PHI apps on the latest Slim 4 patch until Slim 5 ships.
Do I need a BAA for a Slim API?
Yes, if the API stores or sends PHI for a clinic, health plan, or other covered entity. Every vendor that touches that data needs one, starting with your host. Slim has no official host, so your hosting provider must sign.
Slim or Flight for a small PHI API?
Both leave the same rows to you, so the choice rests on the packages around them. Slim follows PSR-15, so any maintained PSR-15 middleware drops in. Flight carries its own middleware style and a smaller package pool. Our guide to whether Flight PHP HIPAA compliant apps are possible walks the same seven settings for Flight.
Recap: Slim Framework HIPAA compliant
To recap, a Slim Framework HIPAA compliant API needs a host that signs a BAA and a hardened server. Slim 4 gives you routing and a PSR-15 pipeline, not security controls. You add maintained auth middleware, password hashing, CSRF or strict CORS, field encryption, rate limits, and an audit trail. Run Slim 4.15.3 or later on a patched PHP release, hide error details, and avoid archived packages.
This article is general information, not legal advice. Versions and packages change often. The details here reflect Slim's documentation, forum, and GitHub repositories and advisories as read on October 20, 2026. AWS and DigitalOcean BAA terms were read on their own pages the same day. PHP release details were read on php.net on October 22, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
Slim docs: Slim 4 documentation, Middleware, and Installation.
GitHub: Slim releases and Slim 5 road map.
Slim forum: Release dates and supported versions.
GitHub advisories: CVE-2026-48157 and Route constraint bypass.
PHP: php.net security advisory for PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 and PHP 8.2.35 release notes, October 21, 2026.
Packages: slimphp/Slim-Csrf and tuupola/slim-jwt-auth.
Cloud providers: AWS HIPAA compliance (BAA in AWS Artifact) and HIPAA at DigitalOcean.
45 CFR § 164.312 (technical safeguards): law.cornell.edu.
45 CFR § 164.308 (administrative safeguards, BAA requirement): law.cornell.edu.
45 CFR § 160.103 (definitions): law.cornell.edu.