


Is Drupal HIPAA Compliant? Acquia, Pantheon, Upsun, and the 9 Settings (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-drupal-hipaa-compliant
Last updated: September 23, 2026
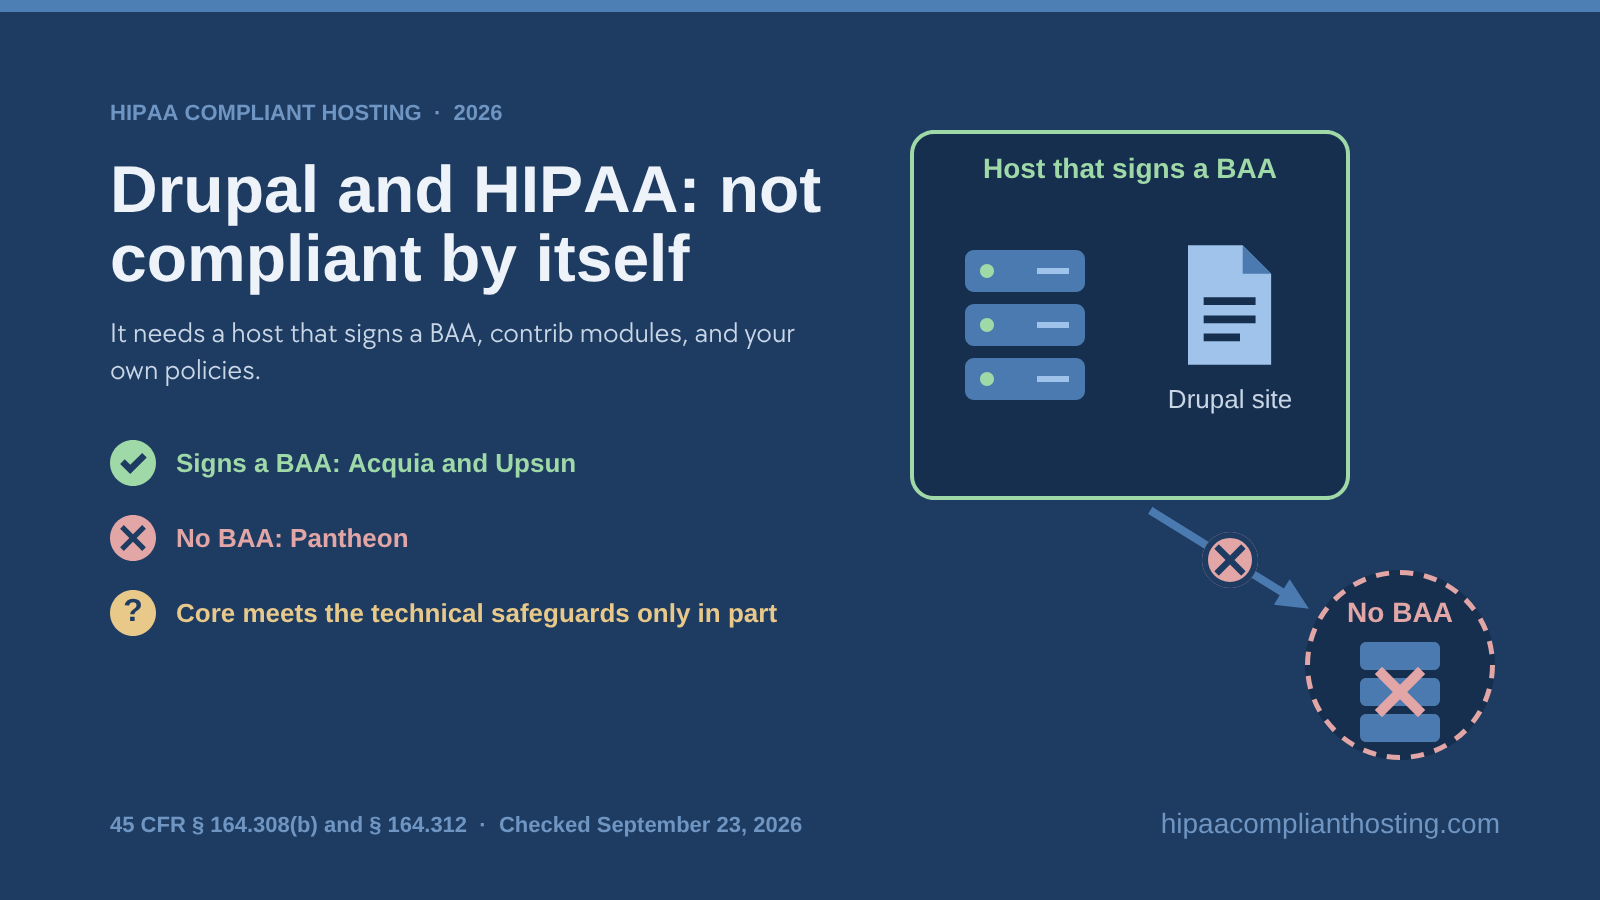
Drupal is not HIPAA compliant on its own, and no CMS is. HIPAA regulates the organizations that handle patient data, not the software they install. A Drupal HIPAA compliant site needs a host that signs a Business Associate Agreement (BAA). It also needs contrib modules and your own policies. Acquia and Upsun sign a BAA. Pantheon does not. Core ships with no multi-factor login, no idle logout, and no field encryption. And Drupal 10 reaches end of life on December 9, 2026. We sell HIPAA compliant hosting, so weigh our advice accordingly.
TL;DR: Quick answer
Drupal is not HIPAA compliant by itself. Under 45 CFR § 164.308(b), the host that stores your database must sign a BAA. As of September 23, 2026, Acquia and Upsun sign one, and Pantheon does not.
Against 45 CFR § 164.312, core gives you roles, login flood control, bcrypt hashing, revisions, and a database log. It lacks MFA, a password policy, idle logout, field encryption, and a record-level access log. A Drupal HIPAA compliant build adds all five from contrib.
In core's default files as of September 22, 2026, the session cookie lasts about 23 days. The private file path and trusted host patterns are unset, and core does not force HTTPS.
Drupal 11.4.7 and 10.6.17, released September 16, 2026, are current. Core had 13 security advisories in 2026 by mid-September.
Webform, used on 331,609 sites, stores submissions in the database and can email or remote-post them. Its encryption add-on had no stable release as of September 23, 2026.
Is Drupal HIPAA compliant? The three-layer answer
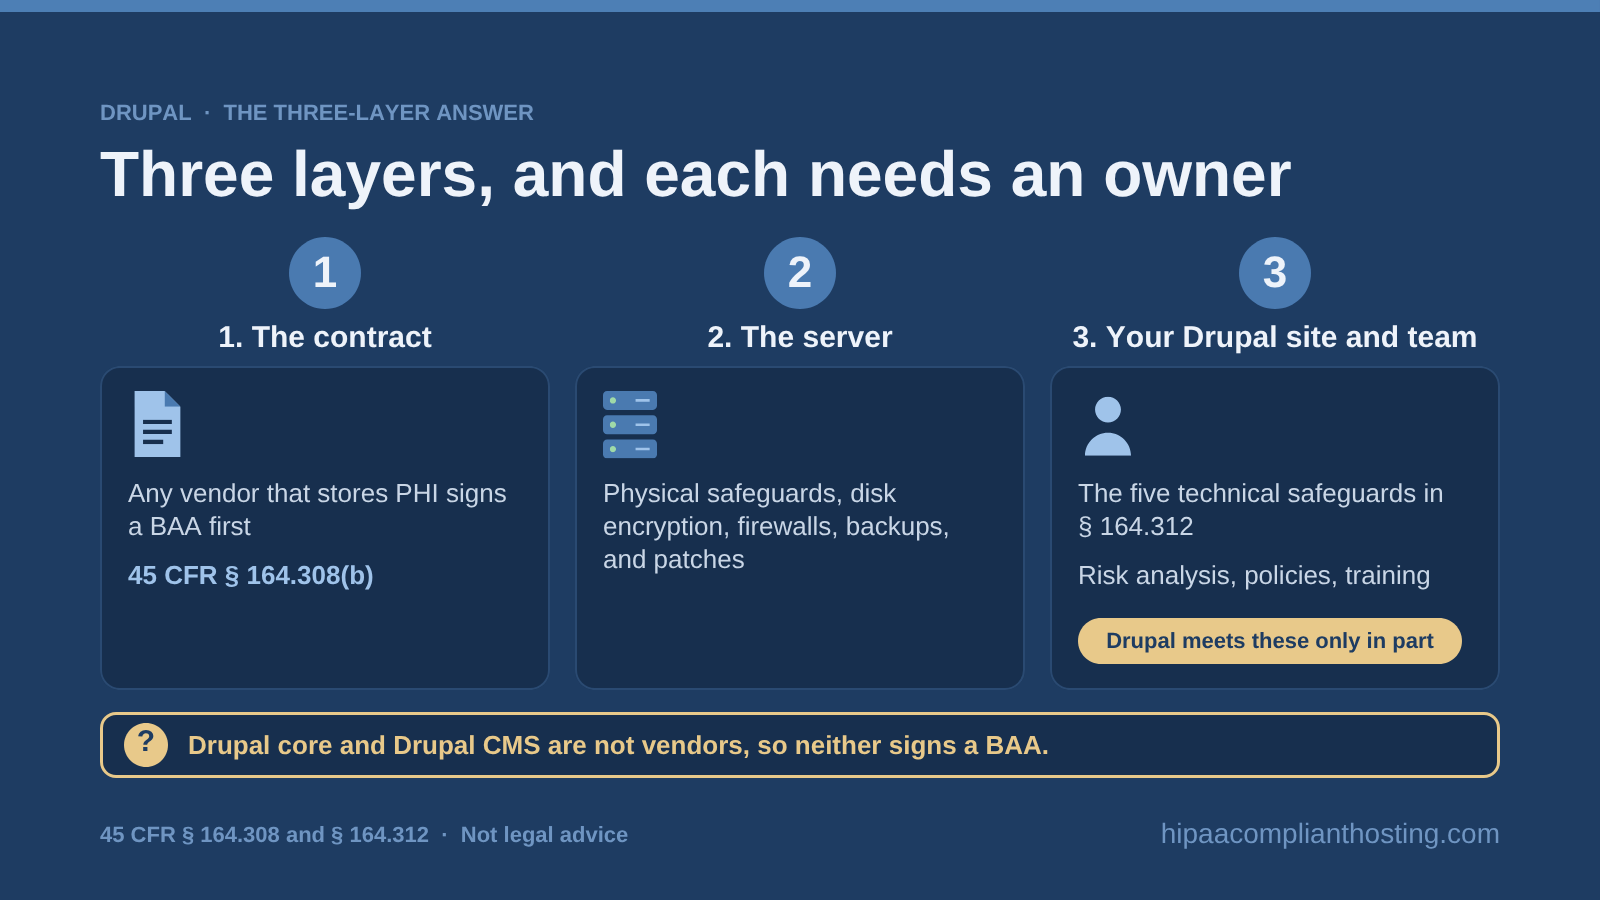
A Drupal HIPAA compliant system has three layers, and each needs an owner. The first is the contract. Under 45 CFR § 164.308(b), any vendor that stores protected health information (PHI) for you must sign a BAA first. Our HIPAA business associate agreement guide covers what the contract must say. The second layer is the server: physical safeguards, disk encryption, firewalls, backups, and patches. The third layer is your Drupal site and your team. It covers the five technical safeguards in 45 CFR § 164.312, which Drupal meets only in part. It also covers the risk analysis under 45 CFR § 164.308(a)(1), policies, training, and a BAA with every vendor in the data path.
Know which Drupal you mean. Drupal core is the open-source PHP framework, licensed GPL-2.0-or-later and supported by the nonprofit Drupal Association. Drupal CMS is a packaged product on Drupal 11 core, now at version 2.1.4 (September 1, 2026). Its page says GDPR and CCPA are "handled automatically" and says nothing about HIPAA. The Drupal HIPAA compliant answer is the same for both. Neither is a vendor, so neither signs a BAA.
What Drupal gives you for the HIPAA technical safeguards
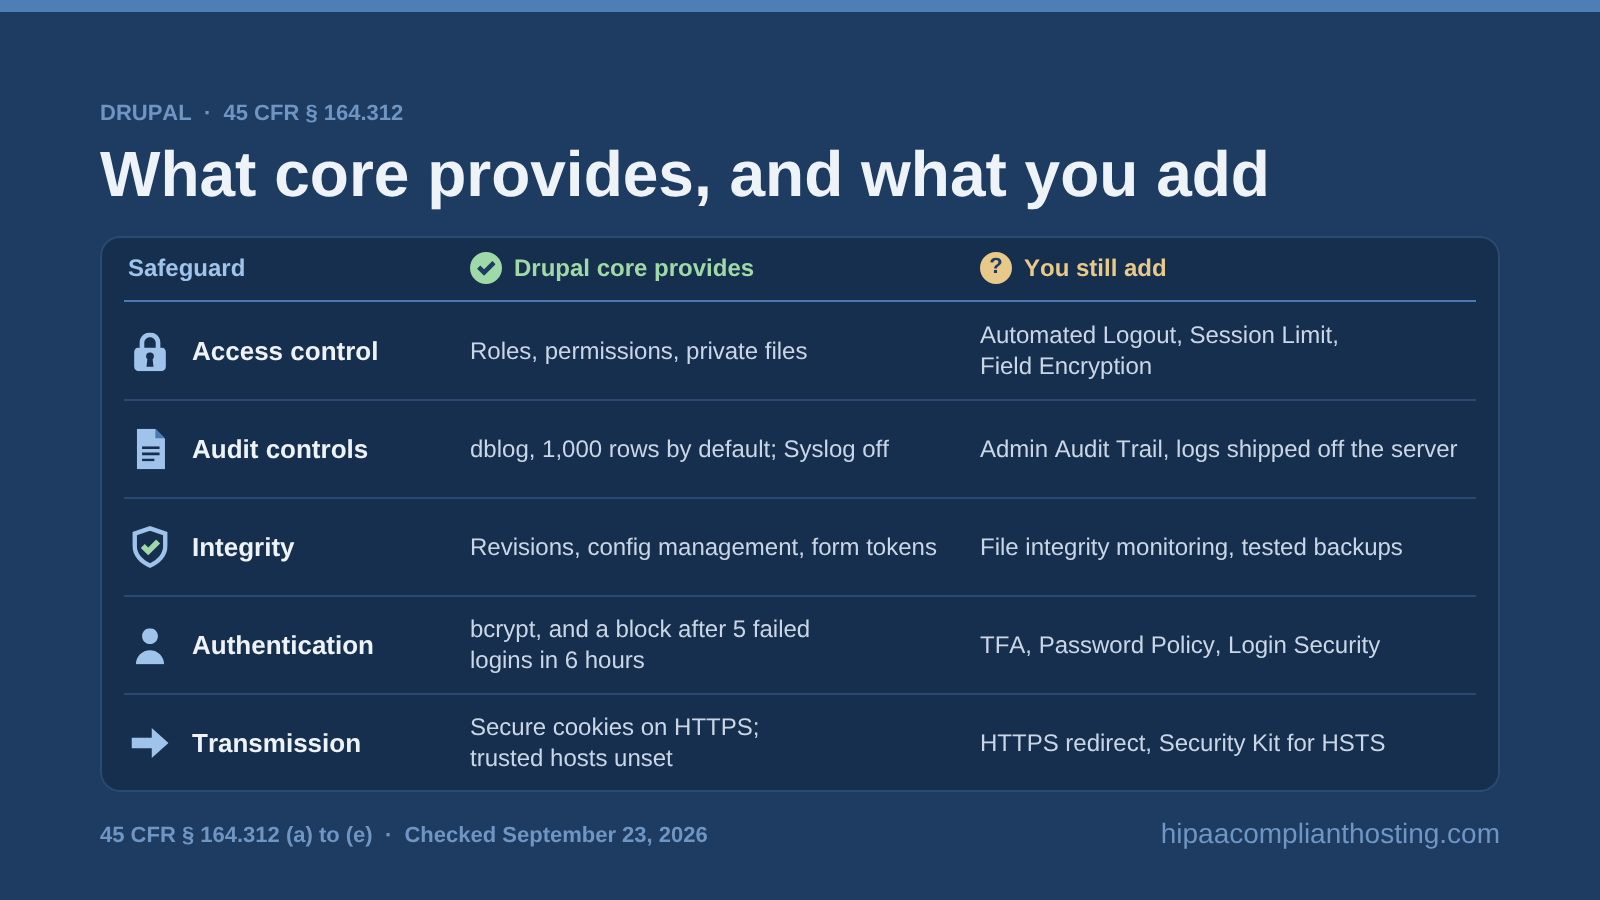
Here is how Drupal core maps to 45 CFR § 164.312. The last column is what a Drupal HIPAA compliant site adds from contrib modules or the host.
Safeguard (45 CFR § 164.312) | What Drupal core provides | What you still add |
|---|---|---|
Access control, (a) | Roles and permissions, unique user accounts, private files with access checks, and session settings | Automated Logout, Session Limit, and Field Encryption for PHI fields |
Audit controls, (b) | Database Logging (dblog), keeping 1,000 rows by default, and Syslog, off by default | Admin Audit Trail, plus log shipping and retention at the host |
Integrity, (c) | Revisions, configuration management, and form tokens | File integrity monitoring and tested backups at the host |
Person or entity authentication, (d) | bcrypt password hashing, and flood control that blocks an account after 5 failed logins in 6 hours | TFA for MFA, Password Policy, and Login Security |
Transmission security, (e) | Secure session cookies on HTTPS sites; trusted host patterns, unset by default | An HTTPS redirect at the web server, Security Kit for HSTS, and SMTP over TLS |
Two gaps matter most for a Drupal HIPAA compliant site. First, core has no encryption for database fields, files, or config. Field-level encryption needs three contrib modules: Encrypt, Key, and Field Encryption. Disk and database encryption at rest and in transit is the host's job. Second, the database log is a system log, not a record of who viewed which patient. Audit logging for a Drupal HIPAA compliant site means a contrib trail plus logs shipped off the server. Database settings are in HIPAA compliant database hosting.
Does Acquia, Pantheon, or Upsun sign a BAA?
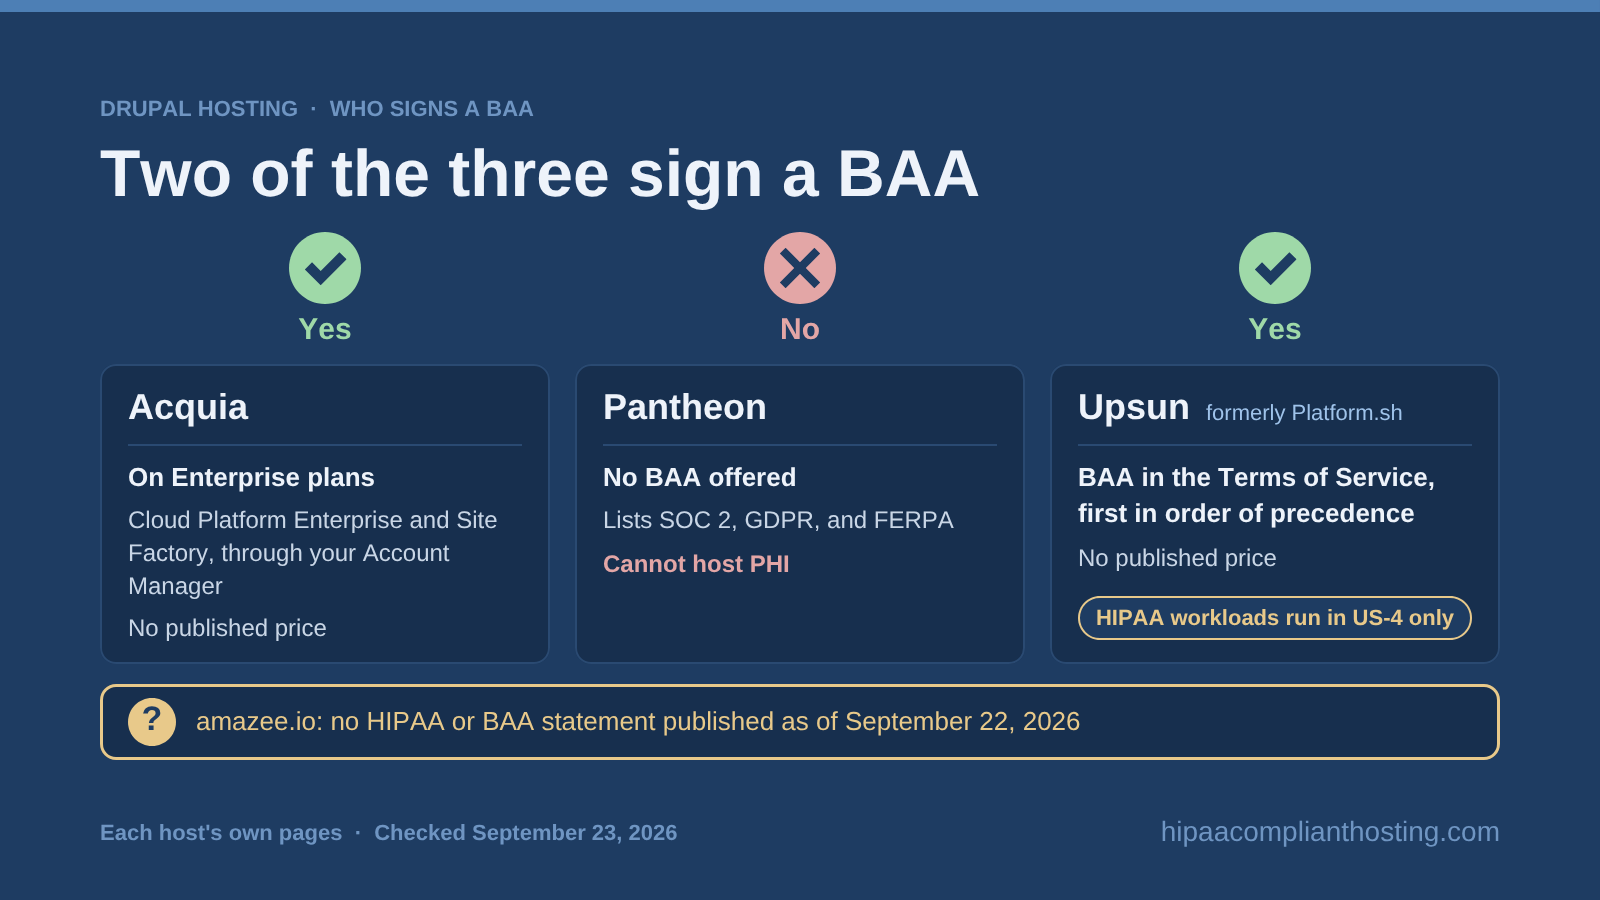
Two of the three do, per each host's own pages on September 23, 2026. For a Drupal HIPAA compliant build, settle this first.
Acquia: yes, on Enterprise plans. Acquia sells a separate HIPAA offering. Customers with it "must sign a BAA through Acquia," its compliance docs state. It is for Cloud Platform Enterprise and Site Factory customers, through their Account Manager. HIPAA customers run in a separate environment with encrypted EBS volumes. No price is published, so expect a quote.
Pantheon: no. Pantheon's own HIPAA article says it "doesn't specifically cater to HIPAA-compliant needs." Its security page lists SOC 2, GDPR, and FERPA on Google Cloud. Site plans run from $55 to $1,150 per month, with workspace plans priced separately. No page we read offers a BAA. So Pantheon cannot carry a Drupal HIPAA compliant site that stores PHI.
Upsun, formerly Platform.sh: yes, in one region. Upsun's HIPAA page says "The Customer must sign a Business Associate Agreement with Platform.sh." The old name survives there. HIPAA workloads "will run on the US-4 region," the page adds. Upsun's Terms of Service, version 1.3 of September 17, 2026, rank the BAA first in order of precedence. No HIPAA price is published. Only Upsun names a single region for Drupal HIPAA compliant workloads. It also hosts Symfony, covered in our Symfony HIPAA compliant guide.
A fourth host, amazee.io, lists GDPR, CCPA, PCI DSS, ISO 27001, and SOC 2 Type II. It did not publish a HIPAA or BAA statement as of September 22, 2026. Other hosts are compared in HIPAA compliant app hosting.
Which Drupal defaults need changing?
These defaults suit a brochure site, not a patient portal. Each comes from core's 11.x default files, read September 22, 2026. A Drupal HIPAA compliant setup changes all seven.
Setting | Default | Where it lives | Change for PHI |
|---|---|---|---|
Session cookie lifetime | 2,000,000 seconds, about 23 days | cookie_lifetime in sites/default/services.yml | Set 0 so the cookie ends when the browser closes |
Session cleanup | 200,000 seconds, about 2.3 days | gc_maxlifetime in sites/default/services.yml | Shorten to match your logoff policy |
Private file path | Unset, so private files are off | file_private_path in settings.php | An absolute path outside the web root |
Trusted host patterns | Unset | trusted_host_patterns in settings.php | Your exact domain names |
HTTPS redirect | Not in core | Web server config or .htaccess | A 301 redirect to HTTPS |
Database log size | Last 1,000 rows kept | row_limit in dblog.settings | Raise it, and ship logs off the server |
Syslog | Module off | Extend page, then the logging settings | Turn on and forward to a BAA-covered log store |
The session cookie is the Drupal HIPAA compliant fix most teams miss. With the default, a shared front-desk browser stays signed in for weeks. Copy default.services.yml to services.yml to change it. Trusted host patterns block Host header spoofing, used for phishing links and cache poisoning. And a 1,000-row log is trimmed on every cron run, far short of HIPAA's six-year documentation rule.
Which Drupal versions are safe to run?
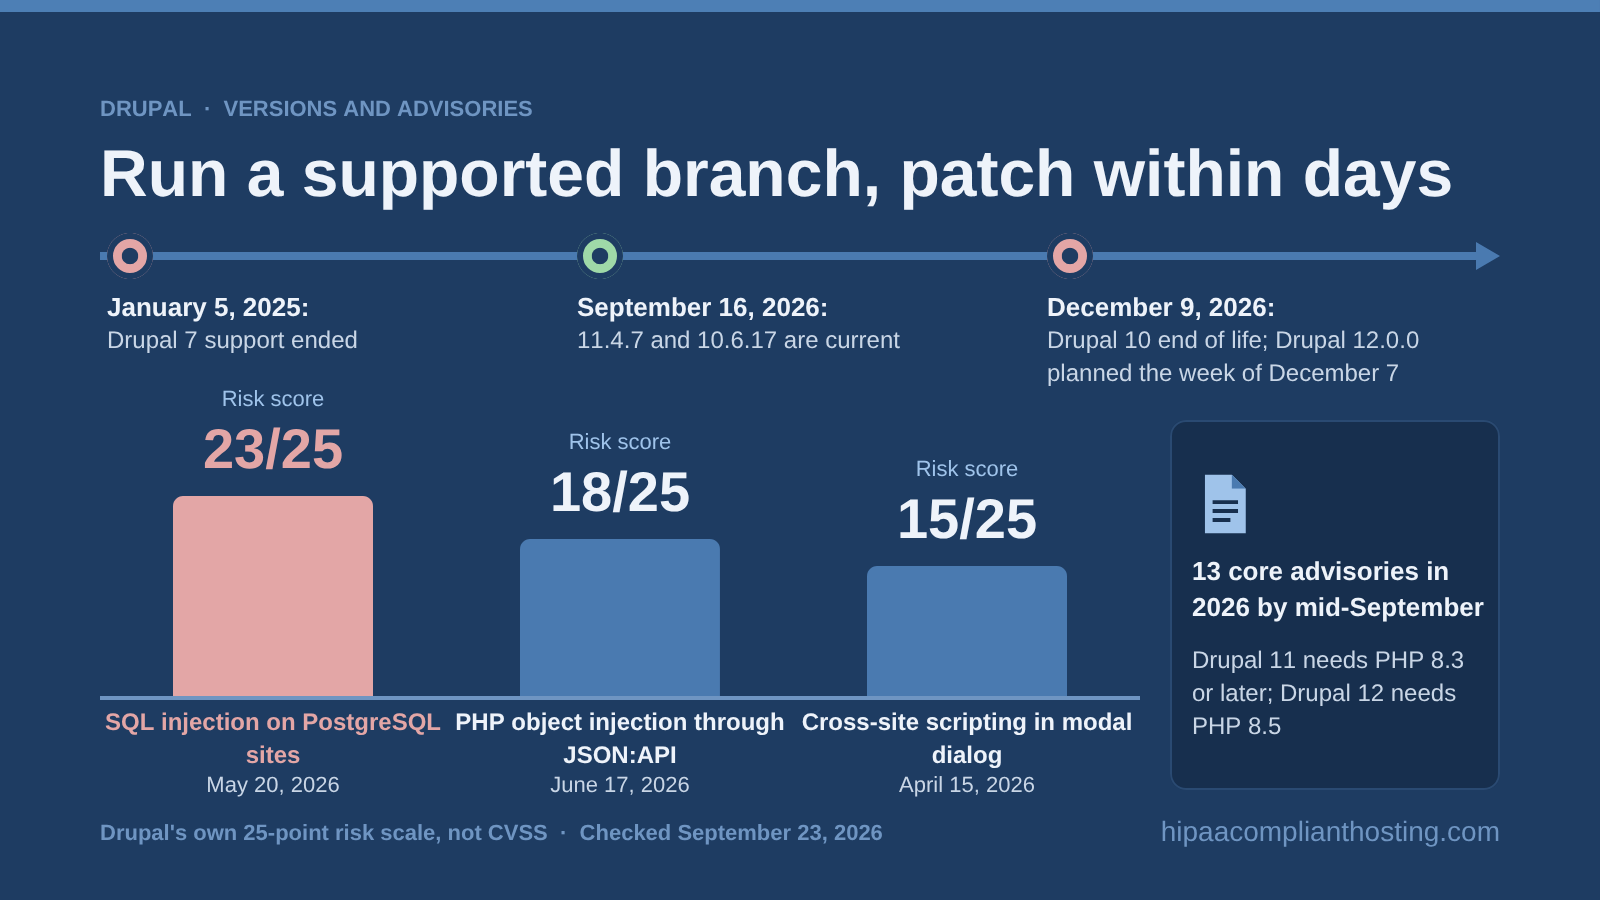
As of September 23, 2026, the current releases are Drupal 11.4.7 and 10.6.17. Both shipped September 16, 2026, for SA-CORE-2026-013, a CKEditor fix. Drupal's release schedule sets the dates that matter:
Drupal 10 reaches end of life on December 9, 2026, with no releases after that.
Drupal 12.0.0 and 11.5.0 are planned for the week of December 7, 2026, when support for 11.3.x and 10.6.x ends.
Drupal 7 support ended January 5, 2025.
Drupal 11 needs PHP 8.3 or later, and Drupal 12 needs PHP 8.5. The most serious of 2026's 13 core advisories so far:
Advisory and date | Drupal risk score | What it was |
|---|---|---|
SA-CORE-2026-004, May 20, 2026 | Highly critical, 23/25 | SQL injection on PostgreSQL sites, open to anonymous users (CVE-2026-9082) |
SA-CORE-2026-005, June 17, 2026 | Critical, 18/25 | PHP object injection through JSON:API, with write access |
SA-CORE-2026-001, April 15, 2026 | Critical, 15/25 | Cross-site scripting in core's modal dialog |
SA-CORE-2025-008, November 12, 2025 | Moderately critical, 10/25 | Wrong cache headers on private files |
Drupal scores advisories on its own 25-point risk scale, not CVSS. On September 9, 2026, the SAML SSO Service Provider module got two Critical ones, SA-CONTRIB-2026-141 and 143. If you use it for single sign-on (SSO), update it now. A Drupal HIPAA compliant site runs a supported branch and patches within days.
The 9 settings that make a Drupal site HIPAA-ready
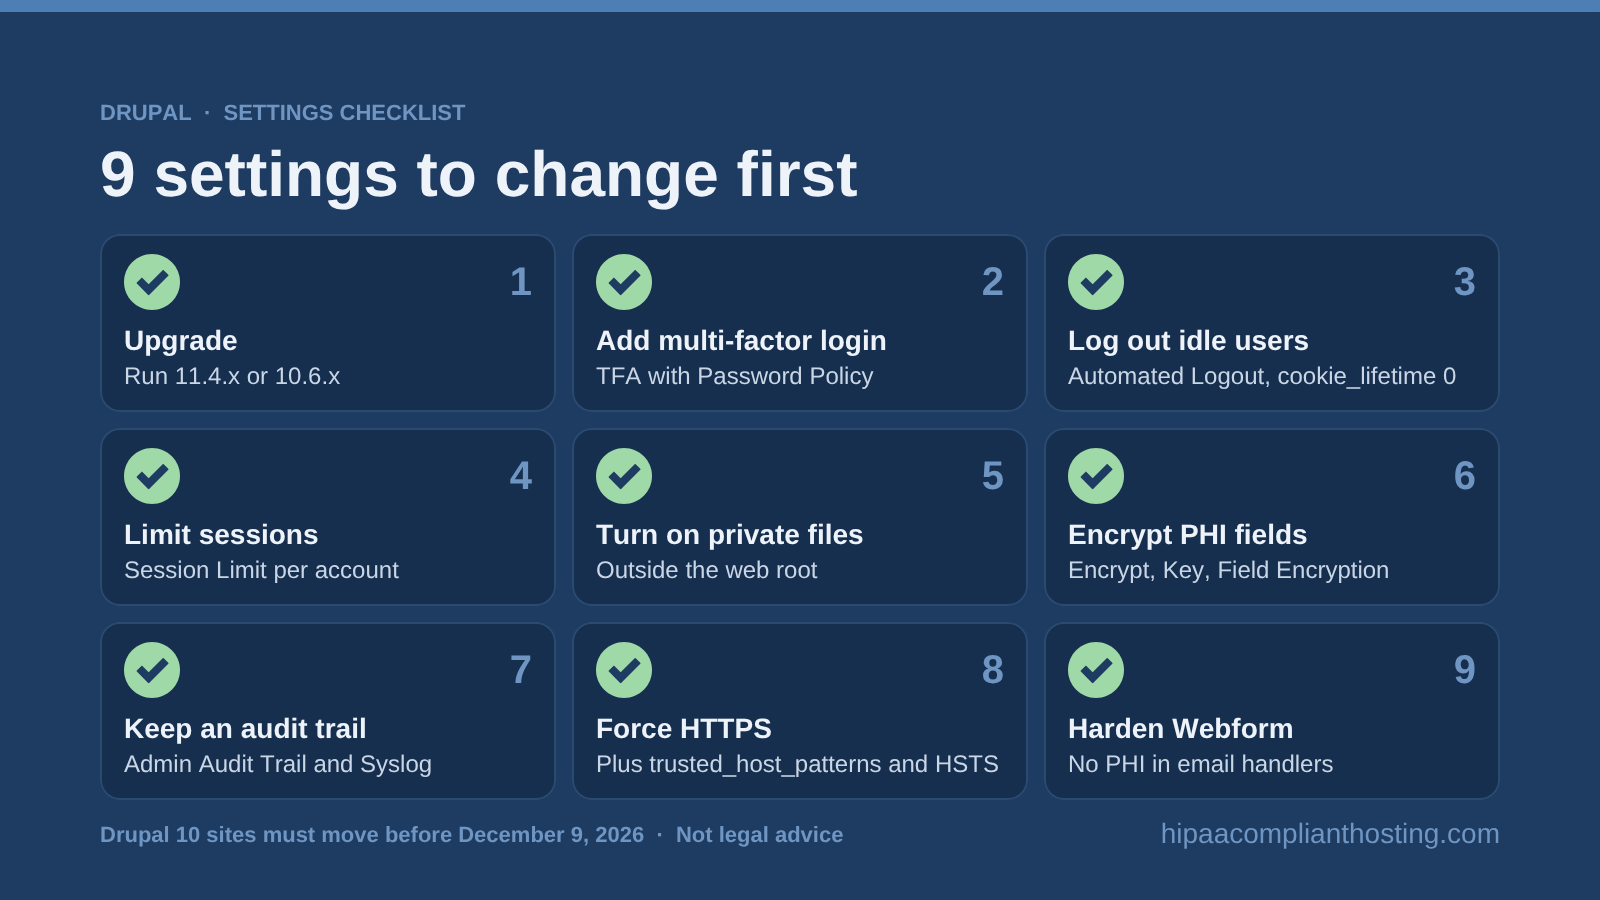
We check these first in every Drupal HIPAA compliant review.
Upgrade, and plan for Drupal 12. Run 11.4.x or 10.6.x today. Sites on Drupal 10 must move before December 9, 2026.
Add multi-factor login. Use TFA 8.x-1.13 (September 16, 2026) with Password Policy and Login Security.
Log out idle users. Automated Logout adds idle timeouts by role. Also set cookie_lifetime to 0.
Limit sessions per user. Session Limit caps sessions per account.
Turn on private files. Set file_private_path outside the web root, and store every PHI upload there.
Encrypt PHI fields. Use Encrypt, Key, and Field Encryption, with keys outside the database. Field Encryption 4.1.0 does not work with Views filters.
Keep an audit trail. Add Admin Audit Trail, turn on Syslog, and ship logs to a store under a BAA.
Force HTTPS and lock host names. Redirect to HTTPS at the web server, set trusted_host_patterns, and add Security Kit for HSTS.
Harden Webform. Keep PHI out of email handlers, remote-post only to vendors with a BAA, and delete old submissions on schedule. Webform Encrypt is still alpha.
Item 2 is covered in HIPAA MFA requirements. Item 3 is the automatic logoff rule in 45 CFR § 164.312(a)(2)(iii), explained in HIPAA automatic logoff. With these nine in place, the Drupal HIPAA compliant work inside your site is mostly done.
Where Drupal sites leak PHI
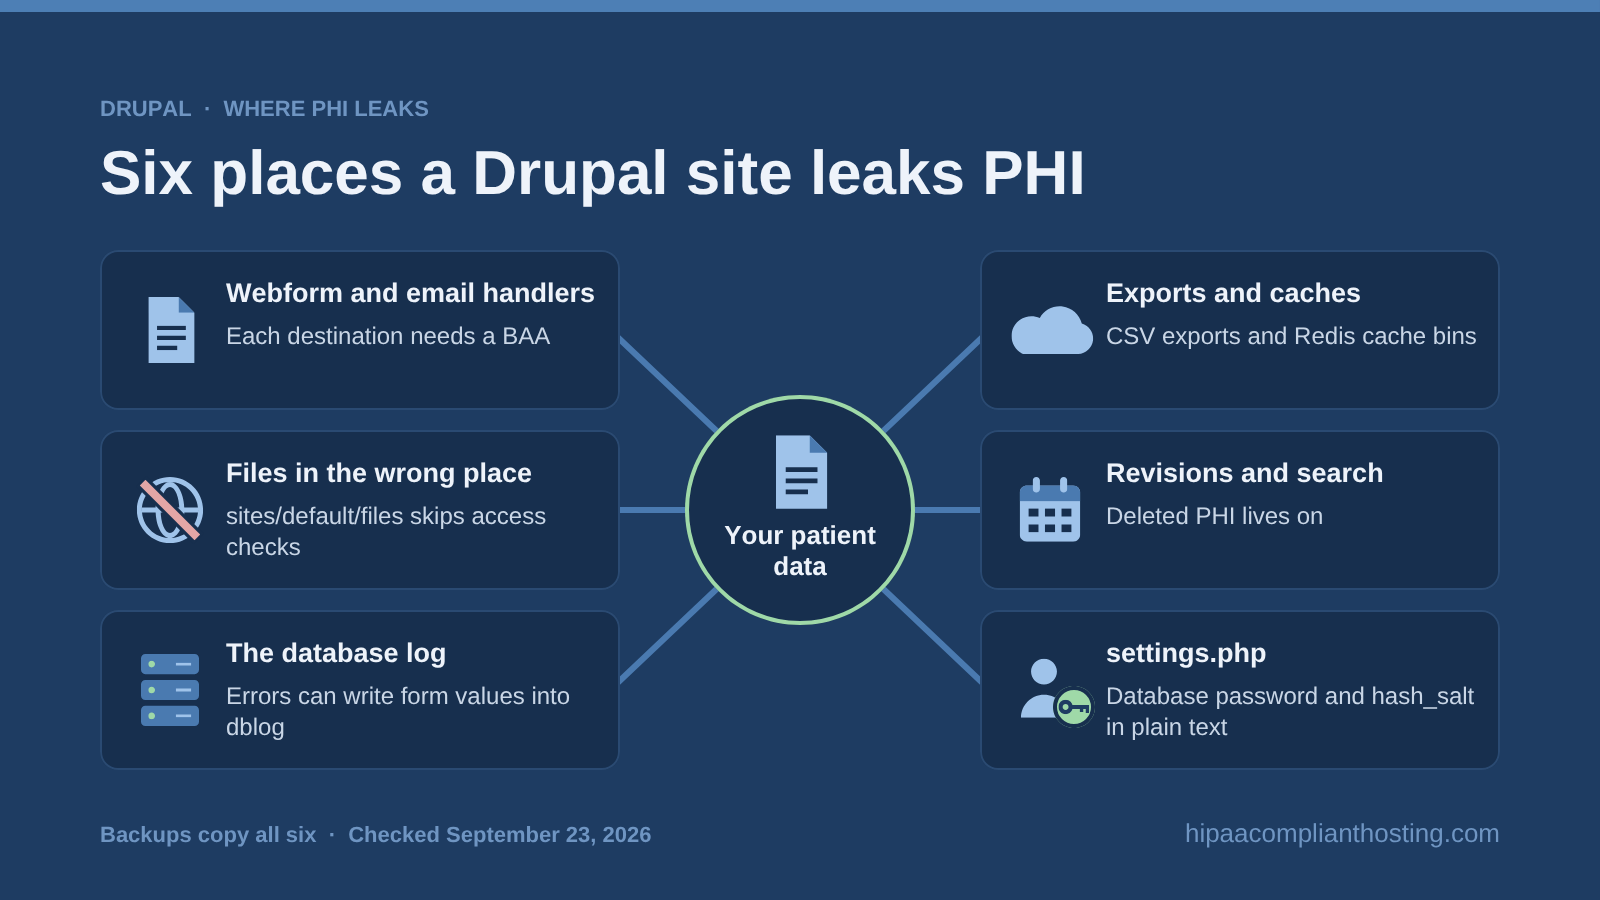
A Drupal HIPAA compliant review finds most leaks in forms, files, and logs.
Webform submissions and email handlers. Intake forms save PHI, email it, and post it to remote targets. Each destination needs a BAA.
Private files in the wrong place. Files under sites/default/files skip Drupal's access checks.
The database log. Errors and custom code can write form values into dblog.
Exports and caches. Views Data Export writes CSV files that a public file location exposes. Redis cache bins can hold rendered patient pages.
Revisions and the search index. Deleted PHI lives on in old revisions and in core Search tables.
settings.php. It holds your database password and hash_salt in plain text.
Webform settings and dblog content are your layer. The mail relay, log store, and backups are the host layer, which you can hand off. Intake form rules are in HIPAA compliant forms. Backups copy all of these, so see HIPAA backup and disaster recovery.
Who signs the BAA for a Drupal site, and what does it cost?
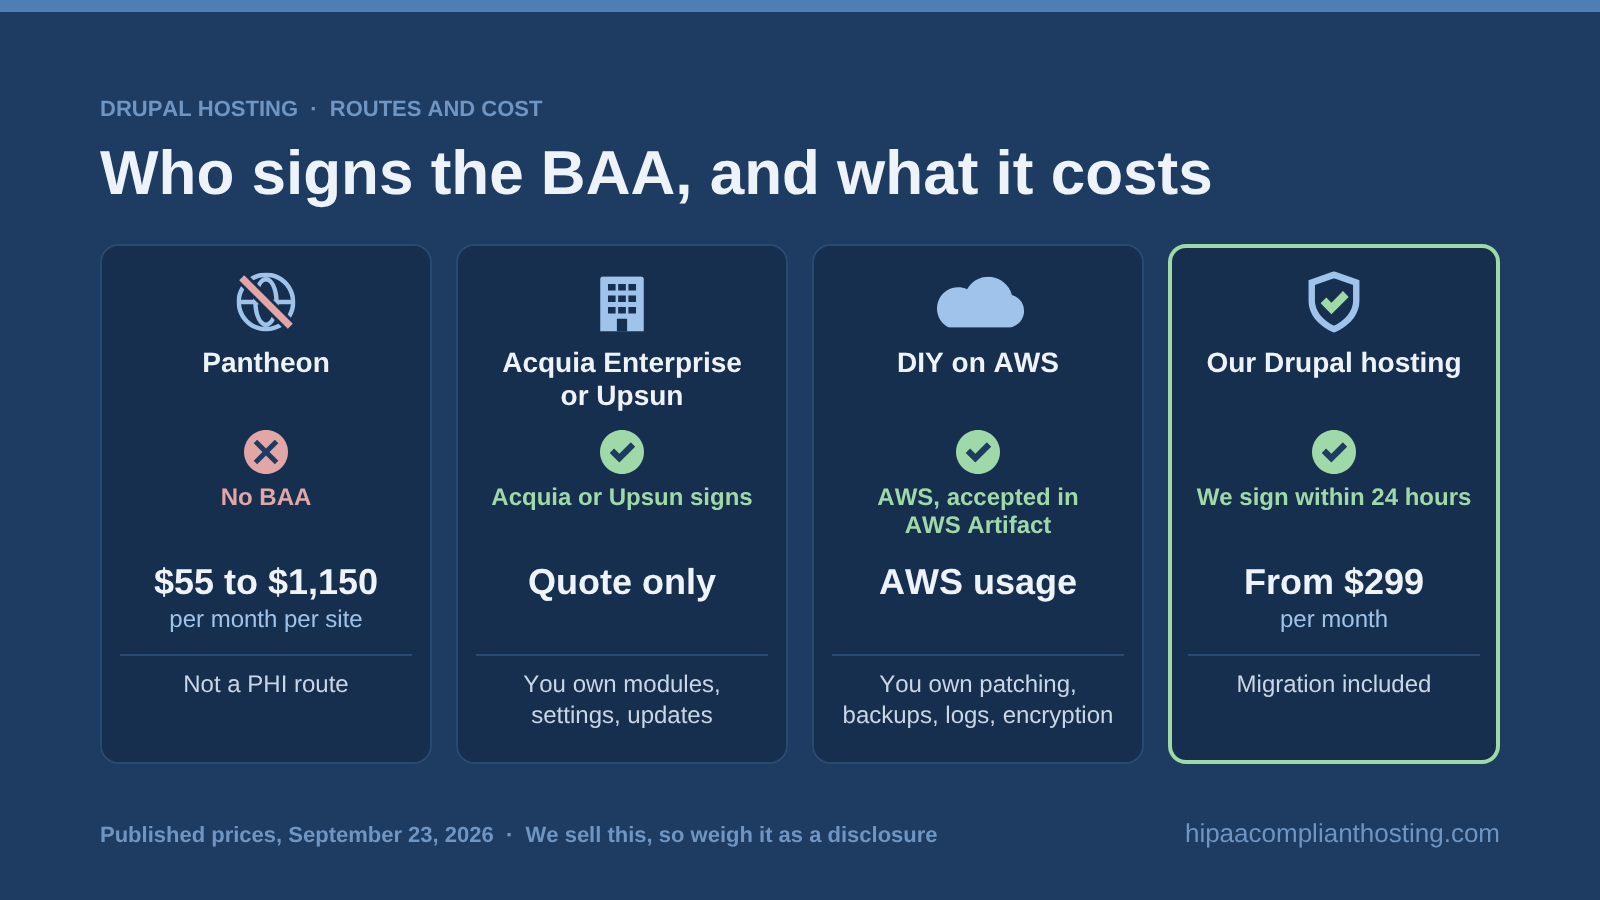
A Drupal HIPAA compliant budget starts with the host that signs the BAA. Figures are as published on September 23, 2026.
Route | Published price | Who signs the BAA | What you still own |
|---|---|---|---|
Pantheon | $55 to $1,150 per month per site | No one; no BAA offered | Not a PHI route |
Acquia Enterprise or Upsun | Quote only | Acquia or Upsun; Upsun in US-4 only | Modules, settings, updates, and your policies |
DIY on AWS | AWS usage | AWS, accepted in AWS Artifact | Server, PHP, and Drupal patching, firewall, backups, logs, and encryption |
HIPAA compliant Drupal hosting from us | From $299 per month, migration included | Us, within 24 hours | Your Drupal site, modules, roles, and content |
We sell the last row, so weigh it as a disclosure. On AWS, PHI belongs only in the HIPAA-eligible services named in AWS's BAA. A Drupal HIPAA compliant DIY build also means applying every core advisory yourself.
If you would rather not run the Drupal server yourself
Most Drupal teams would rather build the site than patch PHP. Our HIPAA compliant Drupal hosting runs Drupal on single-tenant AWS servers. We run the AWS account, network, operating system, PHP, database, TLS, disk encryption, server logs, backups, and monitoring. You run your Drupal modules, roles, Webform settings, content, and updates. That split keeps the Drupal HIPAA compliant duties clear on both sides. The BAA is signed within 24 hours, before any patient data moves. Plans start from $299 per month with migration included. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your team already runs on Acquia Enterprise or Upsun with the BAA signed, you do not need us. If your site is a brochure with no forms and no patient data, it does not need a Drupal HIPAA compliant setup. Moving to a headless CMS? Read our Strapi HIPAA compliant and Payload CMS HIPAA compliant guides first. Weighing WordPress? See is WordPress HIPAA compliant. For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your Drupal site collects.
Frequently asked questions
Is Drupal HIPAA compliant?
Not by itself, and no CMS is. A Drupal HIPAA compliant site needs a host that signs a BAA. It also needs contrib modules for MFA, idle logout, encryption, and audit trails, plus a risk analysis. Drupal is software, not a vendor, so the project never signs a BAA.
Does Acquia sign a BAA?
Yes, through a separate HIPAA offering for Cloud Platform Enterprise and Site Factory, arranged through your Account Manager. Acquia published no price for it as of September 23, 2026.
Is Pantheon HIPAA compliant?
Pantheon does not offer a BAA, so it cannot host PHI. Its pages list SOC 2, GDPR, and FERPA, as of September 23, 2026.
Can Drupal Webform store patient information?
Yes, on a host under a BAA. Webform saves submissions in the database and can email or remote-post them, so keep PHI out of email handlers. Webform Encrypt had only an alpha release as of September 23, 2026.
Does Drupal encrypt data at rest?
No. Drupal core does not encrypt database fields, files, or config. Field-level encryption needs the Encrypt, Key, and Field Encryption modules. On a Drupal HIPAA compliant site, disk and database encryption comes from the host.
Recap: Drupal HIPAA compliant
A Drupal HIPAA compliant site is Drupal on a host that signs a BAA, plus contrib modules and your policies. Acquia and Upsun sign a BAA, and Pantheon does not. Core lacks MFA, idle logout, field encryption, and a record-level audit trail. Change the 23-day session cookie, set private files and trusted hosts, and force HTTPS. Leave Drupal 10 before December 9, 2026.
This article is general information, not legal advice. The details here reflect drupal.org and vendor pages as read on September 22 and 23, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed September 2026.
Sources
Drupal.org: Release schedule, Releases, and PHP requirements.
Drupal.org security: Core advisories, SA-CORE-2026-004, SA-CORE-2026-005, and SA-CORE-2026-001.
Drupal.org docs: Enabling HTTPS, Session management, Trusted host settings, Database Logging, and Syslog.
Drupal core source (11.x): default.services.yml, default.settings.php, user.flood.yml, and dblog.settings.yml.
Drupal CMS: project page.
Modules: TFA, Automated Logout, Session Limit, Field Encryption, Admin Audit Trail, Webform, and Webform Encrypt.
Acquia: Compliance standards and regulations.
Pantheon: HIPAA compliance article, Security and compliance, and Pricing.
Upsun: HIPAA and Terms of Service.
amazee.io: Enterprise Drupal hosting.
AWS: HIPAA compliance.
45 CFR § 164.308 and § 164.312: ecfr.gov.
45 CFR § 164.316 (documentation retention): law.cornell.edu.