


Is ExpressionEngine HIPAA Compliant? EE 7, Packet Tide, and the Settings That Matter (2026)
HIPAA Compliant Hosting · https://hipaacomplianthosting.com/blog/is-expressionengine-hipaa-compliant
Last updated: October 22, 2026
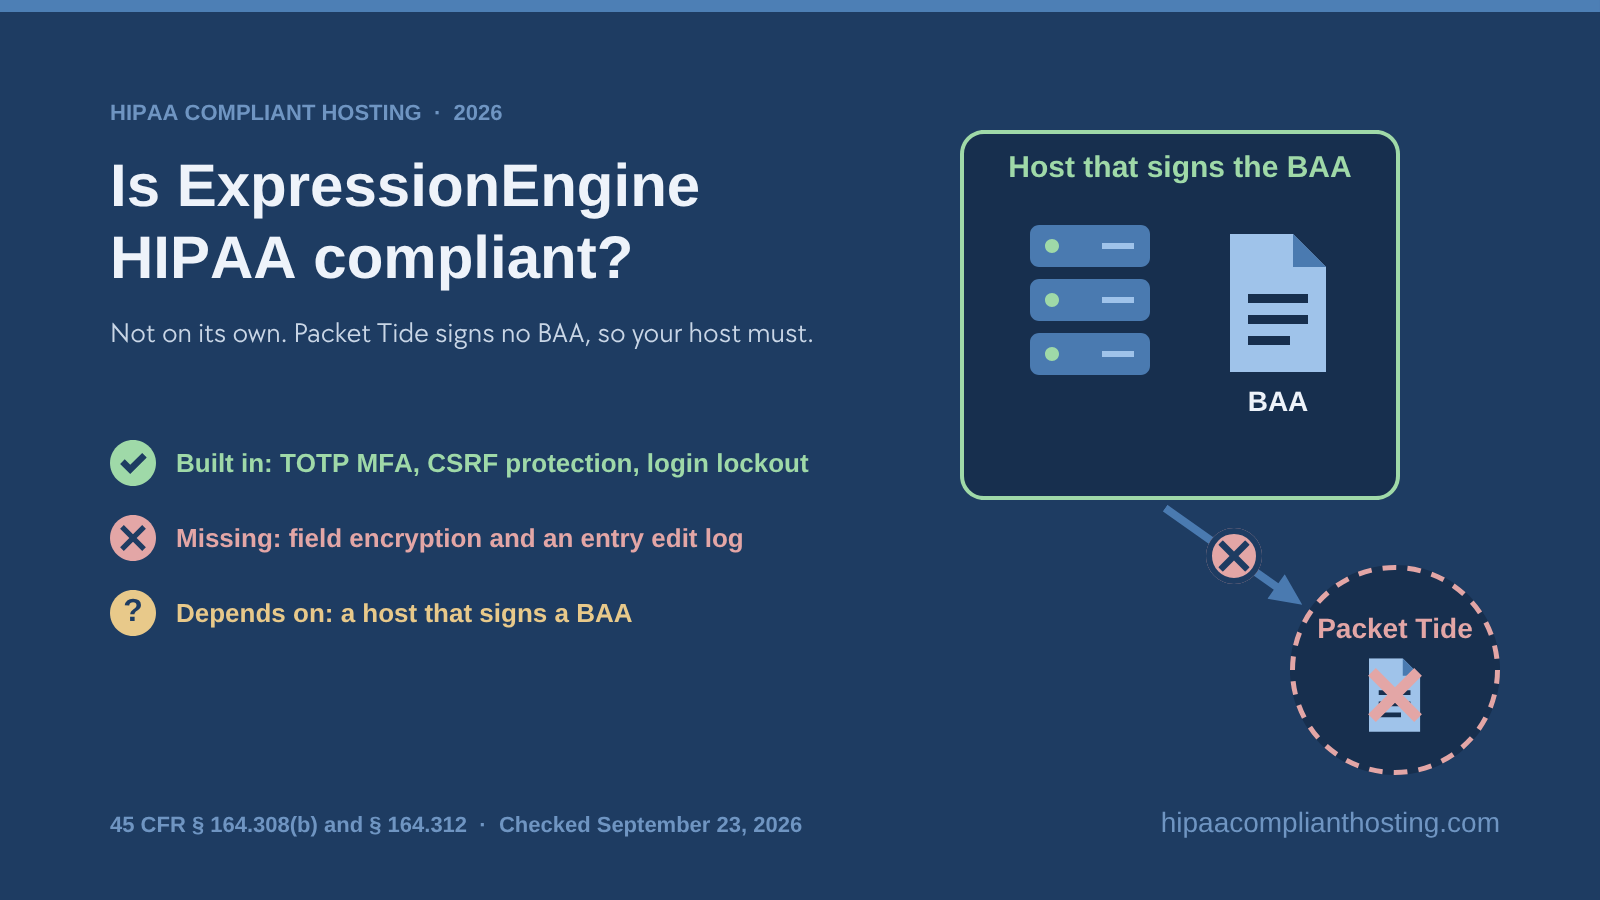
ExpressionEngine is not HIPAA compliant on its own, and no CMS is. HIPAA regulates the organizations that handle patient data, not the software they install. An ExpressionEngine HIPAA compliant site needs a host that signs a Business Associate Agreement (BAA). Packet Tide, which owns EE, sells software, not hosting, so it signs no BAA. EE 7 has two-factor login and CSRF protection built in, but no field encryption and no log of who edited which entry. And EE 6 reaches end of life on December 31, 2026. We sell HIPAA compliant hosting, so weigh our advice accordingly.
TL;DR: Quick answer
ExpressionEngine is open-source PHP software under the Apache License 2.0, owned by Packet Tide. As of October 20, 2026, the newest release is 7.5.28, which the changelog flags for important security updates. EE 8.0 is not out yet.
Packet Tide signs no BAA, so your host is the business associate under 45 CFR § 164.308(b). As of October 20, 2026, Liquid Web's EE plans list no BAA, while its HIPAA line and Nexcess offer one.
Against 45 CFR § 164.312, EE 7 ships TOTP multi-factor login, default CSRF protection, bcrypt hashing, and login lockout. It has no field encryption, no entry edit log, and no private uploads.
Per the EE 7 docs, re-checked October 20, 2026,
cookie_secureis off by default. EE has no force-HTTPS setting, and its Backup Utility writes a plaintext SQL file.Core allows one control panel user. An ExpressionEngine HIPAA compliant site with staff needs Pro, $249 as of October 20, 2026, for unique logins under 45 CFR § 164.312(a)(2)(i).
Prefer not to run the server? Our HIPAA compliant ExpressionEngine hosting runs EE on single-tenant AWS from $229 a month. We sign the BAA within 24 hours of signup.
Is ExpressionEngine HIPAA compliant? The three-layer answer
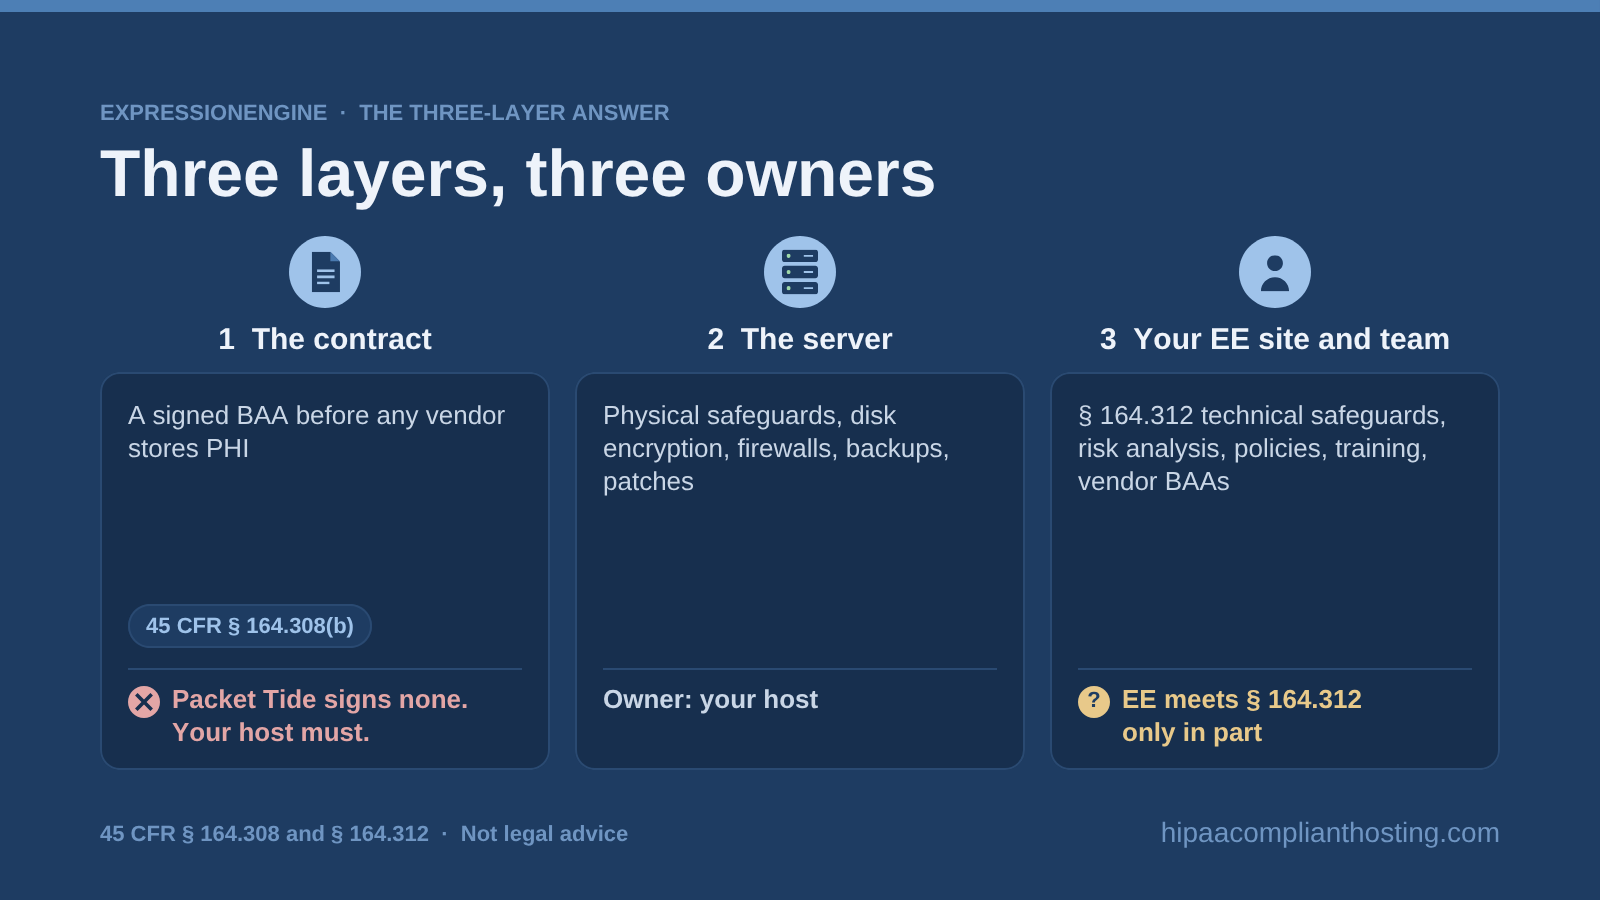
An ExpressionEngine HIPAA compliant system has three layers, and each needs an owner. The first is the contract. Under 45 CFR § 164.308(b), any vendor that stores protected health information (PHI) for you must sign a BAA first. See our HIPAA business associate agreement guide. The second layer is the server: physical safeguards, disk encryption, firewalls, backups, and patches. The third layer is your EE site and team. It covers the 45 CFR § 164.312 technical safeguards, which EE meets only in part. It also covers the risk analysis under 45 CFR § 164.308(a)(1), policies, training, and vendor BAAs. Our HIPAA risk analysis guide shows what the analysis must cover.
Packet Tide, LLC owns and develops ExpressionEngine, which most users call EE. EllisLab released version 1.0 in 2004, and Packet Tide has run it since October 2019. The core uses the Apache License 2.0, not MIT, and Pro is a separate paid license. EE runs on a bundled legacy CodeIgniter core, so our CodeIgniter HIPAA compliant guide covers the framework underneath. So the ExpressionEngine HIPAA compliant answer turns on your host.
What ExpressionEngine 7 gives you for the HIPAA technical safeguards
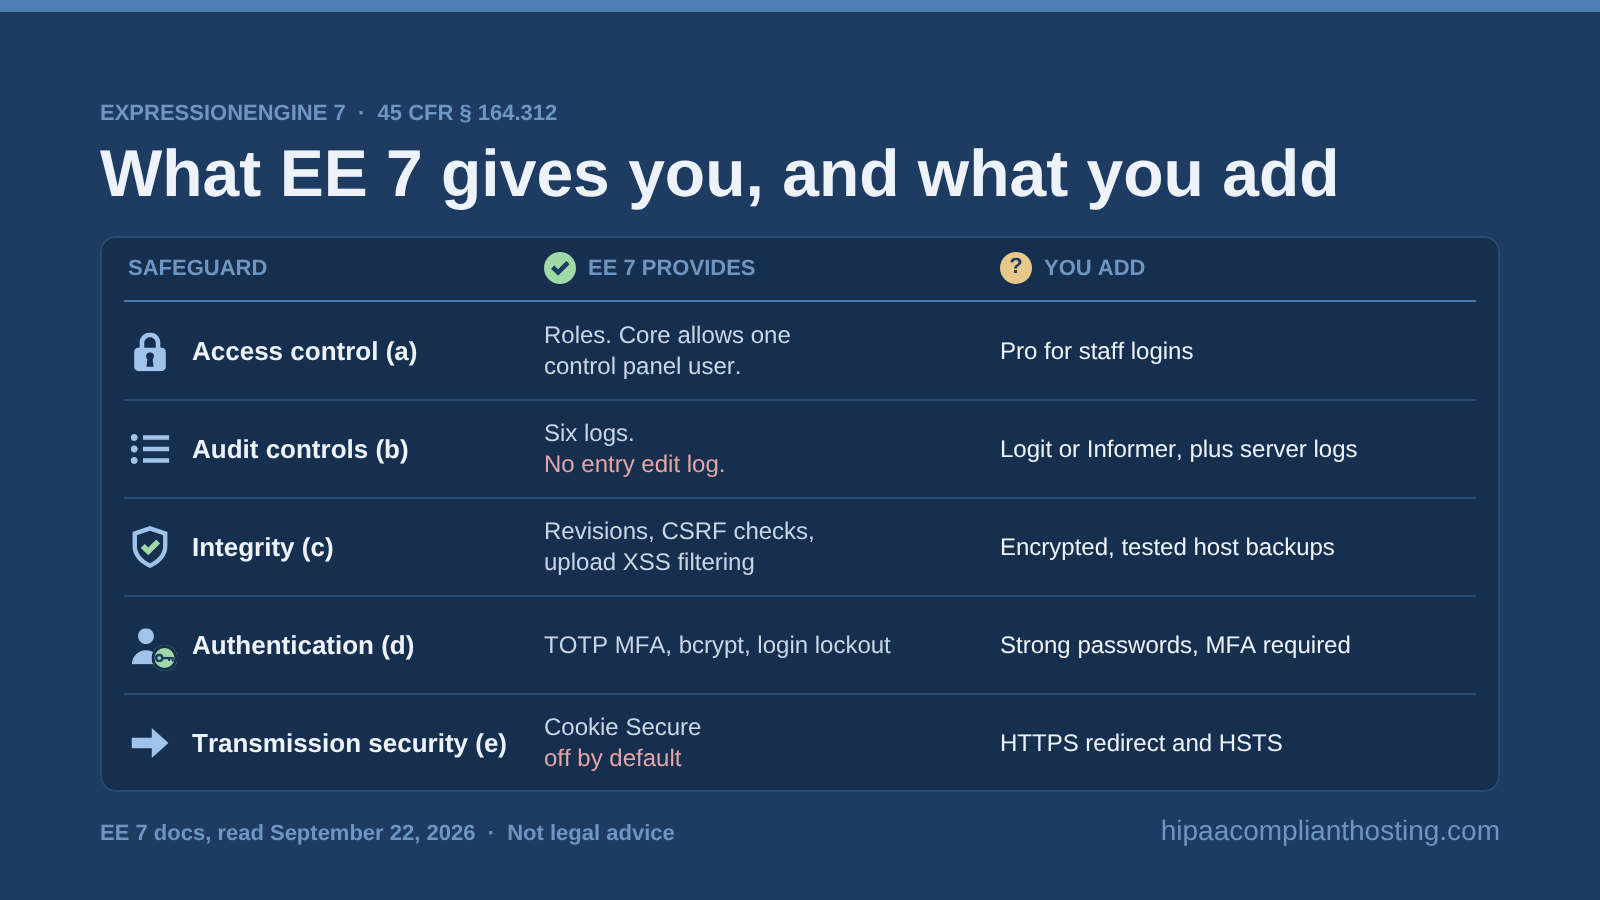
Here is how EE 7 maps to 45 CFR § 164.312. The last column is what an ExpressionEngine HIPAA compliant site adds.
Safeguard (45 CFR § 164.312) | What ExpressionEngine 7 provides | What you still add |
|---|---|---|
Access control, (a) | Member roles, per-channel and per-template access, and Role Groups. Core allows one control panel user. | ExpressionEngine Pro for separate staff logins, and private file storage outside EE |
Audit controls, (b) | Six logs, including CP Access, plus entry versioning. No log of who edited an entry. | Logit ($45) or Informer ($15), plus server logs shipped off the server |
Integrity, (c) | Entry revisions, CSRF checks on all requests, XSS filtering of uploads, and Strip image metadata | Encrypted, tested backups at the host |
Person or entity authentication, (d) | TOTP MFA, optional or required per role, bcrypt hashing, and lockout after more than four failed logins | A Strong password policy and MFA required on every role with control panel access |
Transmission security, (e) | Cookie Secure (off by default), Cookie HttpOnly (on), SameSite Lax, and the HTTP Header add-on | An HTTPS redirect and HSTS at the web server, and SMTP over TLS |
Three gaps decide the ExpressionEngine HIPAA compliant question. First, EE has no field, column, or database encryption for entries, members, or form data. Disk and database encryption at rest and in transit is the host's job. Second, no built-in log records which user viewed or edited which entry. Audit logging here means an add-on plus server logs kept under a BAA. Logit and Informer were last updated about two years ago, so test them on 7.5.x. Third, a shared Core login breaks unique user identification, so a clinic with staff editors needs Pro.
Does Packet Tide, Liquid Web, or Nexcess sign a BAA?
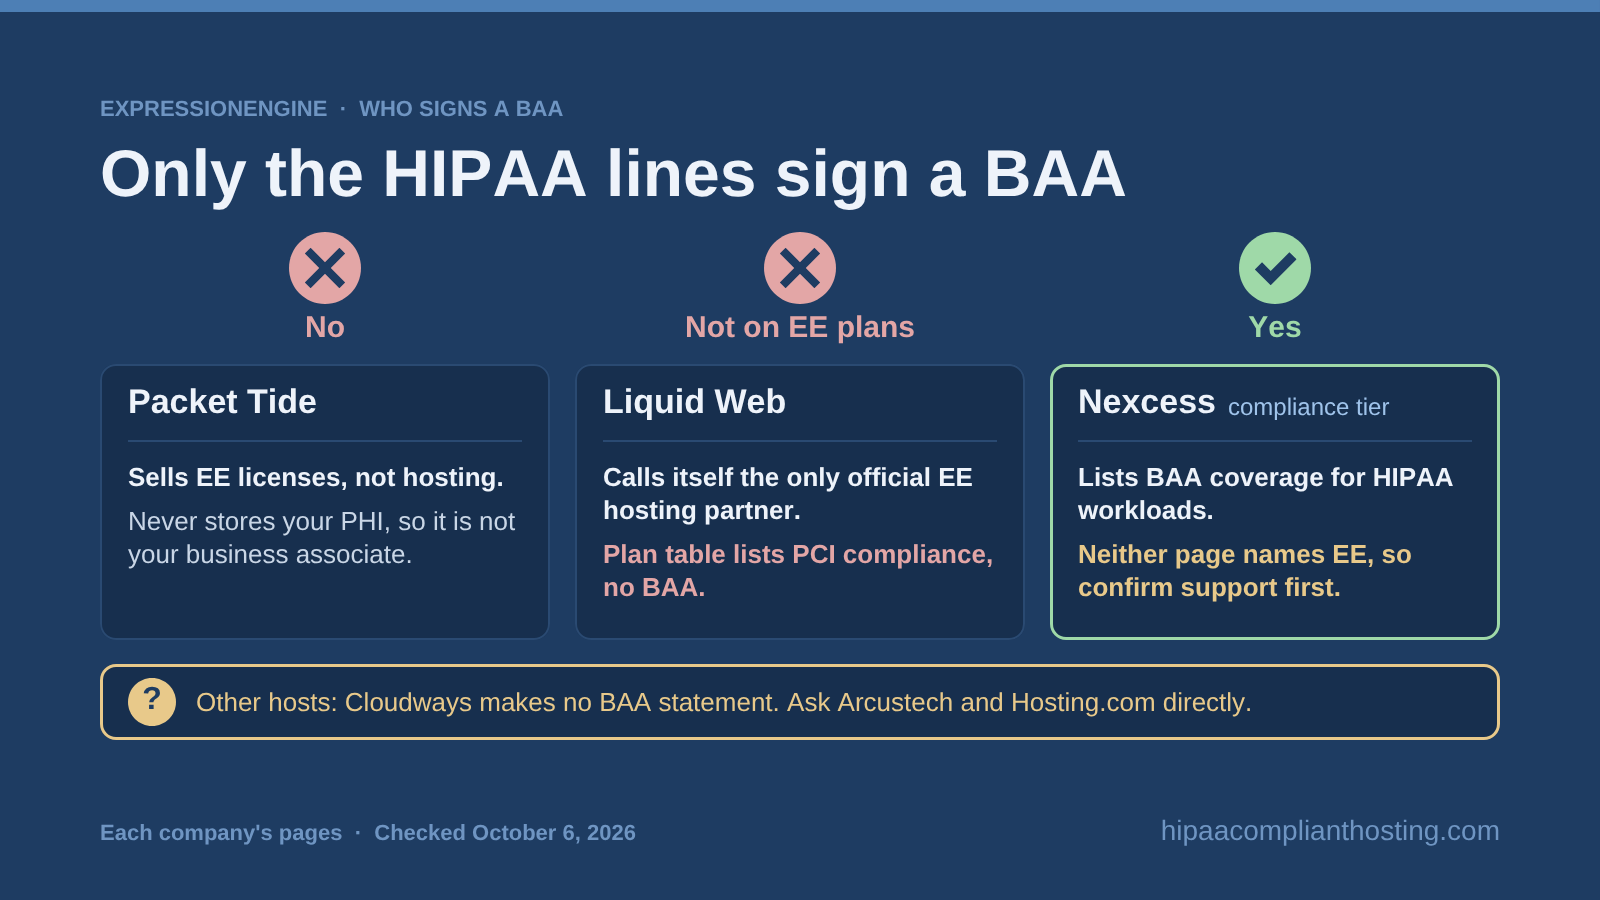
Of the hosts below, only the Liquid Web and Nexcess HIPAA lines say they sign one, per each company's pages on October 20, 2026. An ExpressionEngine HIPAA compliant build settles this first.
Packet Tide: no. Packet Tide sells EE licenses, not hosting. The pages we checked on October 20, 2026 had no HIPAA or BAA text. It never stores your PHI, so it is not your business associate.
Liquid Web: not on its EE plans. Liquid Web calls itself the only official ExpressionEngine hosting partner. Its EE plans run from $64 to $1,128 per month, as checked October 20, 2026. The plan table lists PCI compliance but no BAA. Its HIPAA hosting is a separate dedicated-server line with a signed BAA. Liquid Web says those servers are billed monthly from $229 a month for Linux.
Nexcess: yes, on its compliance tier. Nexcess and Liquid Web are one company. Nexcess lists BAA coverage for HIPAA workloads on its compliance tier, which its page shows starting at $199 a month. An April 22, 2026 press release says Nexcess "executes BAAs with qualifying healthcare clients." Neither page names EE, so confirm support before you sign.
Other hosts. Cloudways sells EE hosting through a Composer install, but its Trust Center lists HIPAA only for partner clouds and makes no BAA statement. On October 20, 2026, Hosting.com's help center said it does not support HIPAA compliant hosting. Arcustech's site and service agreement mention no BAA, so ask it directly. Hosts that do sign one are ranked in our guide to the best HIPAA compliant hosting providers.
Which ExpressionEngine settings are off or missing by default?
These defaults come from the EE 7 docs and the 7.5.28 installer, re-checked October 20, 2026. An ExpressionEngine HIPAA compliant setup changes most of them.
Setting | Default | Change for PHI |
|---|---|---|
cookie_secure | n, off | y, so cookies travel only over HTTPS |
cp_session_length | 3600 seconds, 1 hour | Shorten to match your logoff policy |
website_session_length | 7200 seconds, 2 hours | Shorten for member and patient logins |
expire_session_on_browser_close | n | y |
allow_multi_logins | y on a fresh install | n, so each account has one session |
password_security_policy | Basic | Strong, with a minimum length |
Multi-factor authentication | Optional unless a role requires it | Required on every role with control panel access |
Force HTTPS | No such setting | Redirect and HSTS at the web server |
Upload directories | Always public URLs | Keep PHI files out of EE uploads |
Control panel Backup Utility | Plaintext .sql file in system/user/cache | Do not use for PHI; back up at the host |
disable_csrf_protection | n, so CSRF protection is on | Leave it unset |
The session keys are the ExpressionEngine HIPAA compliant fix that is easiest to miss. EE has no idle-logout screen, so the only timeout controls are cp_session_length and website_session_length in system/user/config/config.php. Set cookie_secure to y there too, once the whole site runs on HTTPS. Never set disable_csrf_protection, which turns off CSRF checks. Those checks guard against cross-site request forgery (CSRF), where another site tricks a signed-in browser into sending a request its user never intended.
Which ExpressionEngine versions are safe to run?
As of October 20, 2026, the newest release is ExpressionEngine 7.5.28, published that day. The changelog flags it for important security updates. EE 8.0 is not out yet. In August 2026, Packet Tide said it aimed to release 8.0 around EEConf, October 7 to 8, 2026. GitHub still lists no 8.x release, and the Version Support page has no EE 8 row. On October 21, 2026, Packet Tide said EE 8 remains on track for release before the end of the year. Check the changelog for anything newer before you upgrade. For an ExpressionEngine HIPAA compliant site, these dates matter:
EE 6 reaches end of life on December 31, 2026. After that it gets no updates of any kind, security fixes included.
EE 7 has no published end-of-life date as of October 20, 2026.
A current Pro license covers the move to EE 8 at no extra fee, per Packet Tide's September 14, 2026 post.
Run PHP 8.2 or 8.3, which the EE 7 docs support, on a patched build. On October 21, 2026, the PHP project released 8.2.35 and 8.3.36 to fix two critical remote code execution flaws. Ask your host to confirm your site runs one of those or a later release in the same branch. A vendor build with both fixes backported also qualifies, whatever its version number. PHP 8.2 gets security fixes only until December 31, 2026, so plan a move to a newer branch.
Through October 20, 2026, the changelog flags six 2026 releases for important security updates:
Version and date | What the changelog says |
|---|---|
7.5.28, October 20, 2026 | Important security updates, plus improved SQL utility request handling |
7.5.27, September 21, 2026 | Important security updates; SQL queries and Search and Replace now require a Super Admin |
7.5.26, July 22, 2026 | Important security updates, with no details published |
7.5.25, June 23, 2026 | Important security updates, plus stronger encryption keys |
7.5.24, June 8, 2026 | Important security updates, plus stricter upload filename checks |
7.5.20, February 26, 2026 | Important security updates, with no details published |
As of October 20, 2026, Packet Tide publishes no CVE ids or severity scores, and GitHub lists no advisories. So your risk analysis should treat every "important security updates" release as required. An ExpressionEngine HIPAA compliant site applies each one within days.
The 8 settings that make an ExpressionEngine site HIPAA-ready
Start with these eight on any ExpressionEngine HIPAA compliant build.
Upgrade. Run 7.5.28 or later. Updating EE does not patch PHP, so confirm PHP is on 8.2.35, 8.3.36, 8.4.27, 8.5.12, or a build with the same fixes. Get it in writing whether you or your host applies PHP updates. Sites on EE 6 must move before December 31, 2026.
Give every user a login, then require MFA. Buy Pro so each staff member has their own account. Then require MFA on every role with control panel access, Super Admin first.
Secure the cookies and force HTTPS. Set
cookie_secureto y and keepcookie_httponlyon. Force HTTPS at the web server, with HSTS.Shorten sessions. Lower
cp_session_lengthandwebsite_session_length, setexpire_session_on_browser_closeto y, and setallow_multi_loginsto n.Tighten passwords. Set
password_security_policyto Strong, raisepw_min_len, turn off dictionary words, and keeppassword_lockouton.Keep PHI out of entries, or protect it at the host. Avoid storing PHI in Channel Form or Freeform entries. Where you must, encrypt at the disk layer and purge old entries on a schedule.
Log who changed what. Review the CP Access log, add Logit or Informer for entry changes, and ship logs to a store under a BAA.
Back up at the host, not in EE. Never run the Backup Utility on a PHI database. Use encrypted backups at the server layer instead.
Item 2 is covered in HIPAA MFA requirements. Item 4 is the automatic logoff rule in 45 CFR § 164.312(a)(2)(iii), explained in HIPAA automatic logoff. Item 7 is the audit controls standard in 45 CFR § 164.312(b); see HIPAA audit logs for what to record and keep. With these eight done, the ExpressionEngine HIPAA compliant work inside your site is mostly done.
Where ExpressionEngine sites leak PHI
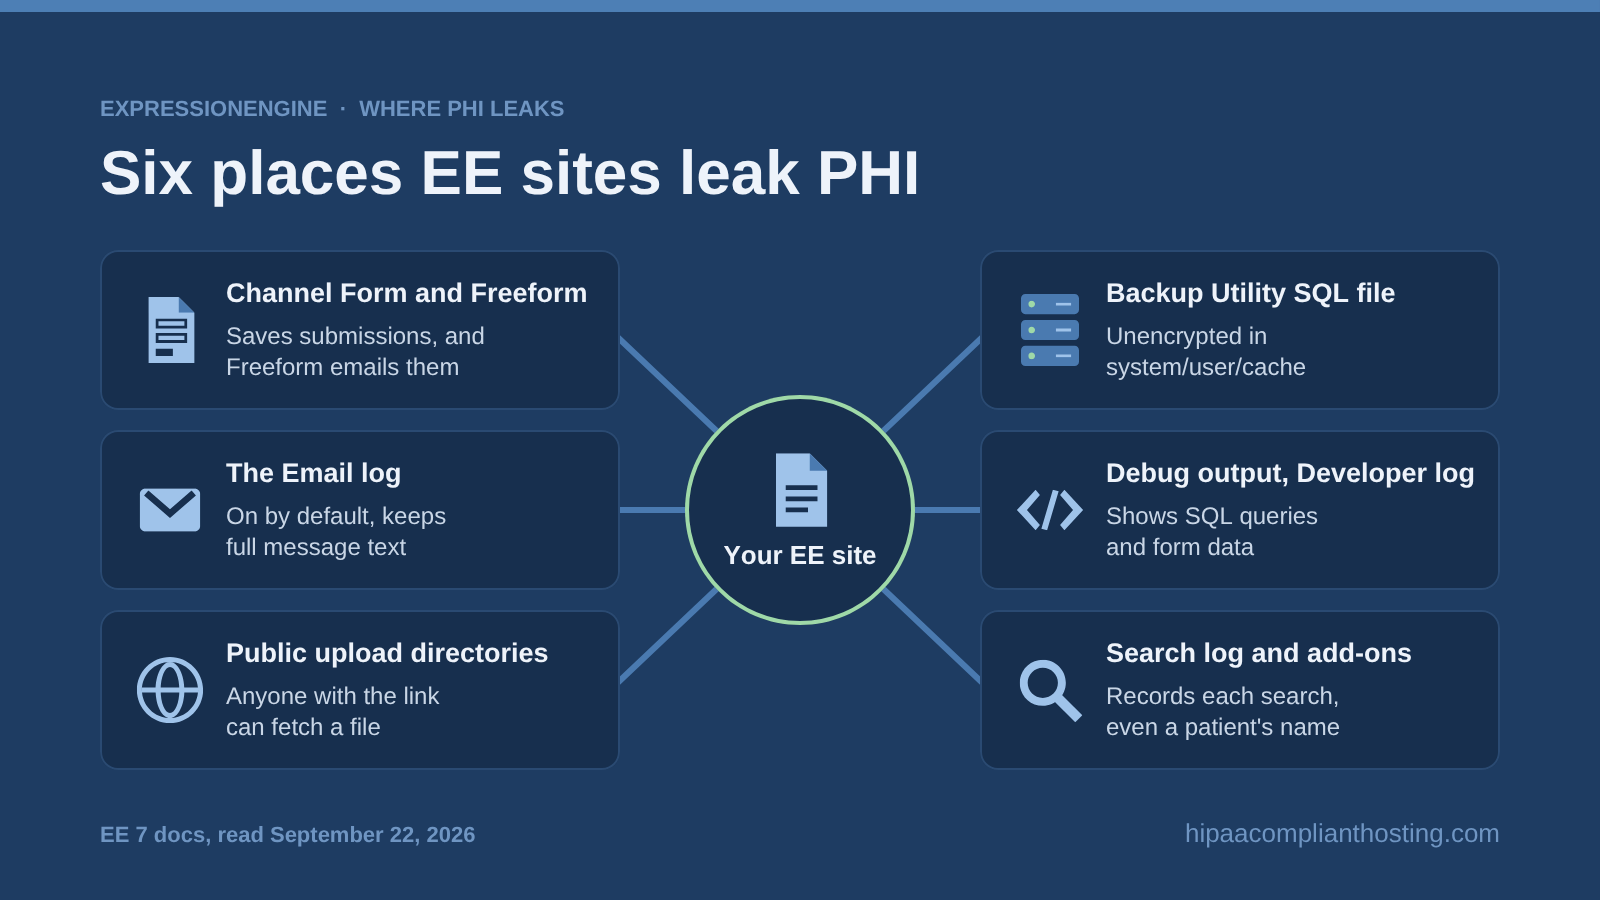
An ExpressionEngine HIPAA compliant review should check forms, logs, files, and backups first.
Channel Form and Freeform submissions. Channel Form saves every front-end submission as an entry, guests included. Freeform stores submissions and emails them, in plain text unless SMTP uses TLS.
The Email log.
log_email_console_msgsis on by default and keeps the full text of Email Console messages.Public upload directories. Every upload directory has a public URL, so a patient document can be fetched by anyone with the link.
The Backup Utility's SQL file. It lands unencrypted in system/user/cache, which may sit inside the web root.
Debug output and the Developer log. Debug output shows SQL queries and submitted form data, and
debugset to 2 shows errors to all users.The Search log and add-ons.
enable_search_logis on by default and records each search term, even a patient's name. Add-ons that send data out need their own BAA.
One example: a clinic's Freeform intake form puts each submission in the database and a staff inbox. An ExpressionEngine HIPAA compliant fix splits the work by layer. Form and log settings are your layer. Disk encryption, the log store, and backups are the host layer, which you can hand off. A mail relay or SMS service outside your host needs its own BAA. Intake form rules are in HIPAA compliant forms. Backups copy every leak above, so see HIPAA backup and disaster recovery.
Who signs the BAA for an ExpressionEngine site, and what does it cost?
An ExpressionEngine HIPAA compliant budget starts with the host that signs the BAA. Figures are as published on October 20, 2026.
Route | Published price | Who signs the BAA | What you still own |
|---|---|---|---|
Liquid Web EE plans | $64 to $1,128 per month | No one; no BAA on the plan page | Not a PHI route as listed |
Liquid Web HIPAA dedicated, or the Nexcess compliance tier | Liquid Web from $229 per month for Linux; Nexcess from $199 per month | Liquid Web or Nexcess | EE settings, add-ons, updates, and your policies |
DIY on AWS or DigitalOcean | Cloud usage | AWS in AWS Artifact, or DigitalOcean through Sales or Support | Server, PHP, MySQL, EE patching, TLS, backups, logs, and encryption |
HIPAA compliant ExpressionEngine hosting from us | From $229 per month; 4 hours of migration and configuration included in the first month | Us, within 24 hours | Your EE site and its updates, add-ons, roles, content, your policies, BAAs with outside services such as a mail relay, and confirming in writing who applies PHP and MySQL updates |
We sell the last row, so weigh it as a disclosure. Any ExpressionEngine HIPAA compliant route with more than one editor also needs Pro. On AWS, PHI belongs only in HIPAA-eligible services.
If you would rather not harden the server yourself
If your team would rather build templates than run servers, our HIPAA compliant ExpressionEngine hosting runs EE on a single-tenant AWS server. Every plan includes a web application firewall, CloudFront CDN, encryption at rest and in transit, and six-year audit logging. It also includes tested encrypted backups and EBS storage with 7-day snapshot retention. You run EE updates, add-ons, roles, forms, content, and your policies. Confirm in writing who applies PHP and MySQL updates, so the ExpressionEngine HIPAA compliant duties stay clear on both sides.
Our BAA covers the servers and services we run, and we sign it within 24 hours of signup, before any patient data moves. An outside service, such as a mail relay, needs its own BAA. Managed plans start at $229 a month, and monthly plans have no long-term contract. The first month includes 4 hours of migration and configuration. After that, work is $175 an hour, quoted before work starts. Each plan is one server in one AWS availability zone, and a multi-zone design is quoted separately. We sell this, so weigh it as a disclosure.
Here is the honest inverse. If your EE site is an association site with no member health data, it needs none of this. If your team already runs on the Nexcess compliance tier with a signed BAA, you do not need us. Thinking of leaving EE before the EE 8 upgrade? See is WordPress HIPAA compliant first. Moving to Drupal instead? Its core ships no MFA, but Acquia and Upsun sign a BAA. The Drupal HIPAA compliant guide names the module that fills the MFA gap.
For everyone else, our HIPAA compliant hosting plans are public. You can request a quote or tell us what your EE site collects.
Frequently asked questions
Is ExpressionEngine HIPAA compliant?
Not by itself, and no CMS is. An ExpressionEngine HIPAA compliant site needs a host that signs a BAA, Pro for staff logins, and MFA on every role. It also needs an audit add-on, host encryption, and a risk analysis.
Does ExpressionEngine have two-factor authentication?
Yes. EE 7 has included TOTP multi-factor authentication since version 7.0.0 in August 2022, in the free Core edition too. Users turn it on in their profile, and you can require it for any member role.
Does Packet Tide sign a BAA?
No. Packet Tide sells ExpressionEngine licenses and does not host sites, so it never stores your PHI. Your host is the business associate. As of October 20, 2026, Nexcess offers a BAA on its compliance tier, and Liquid Web's EE plans do not.
Can ExpressionEngine encrypt patient data?
Not in the database. EE 7 has no field or database encryption for entries, members, or form submissions. On an ExpressionEngine HIPAA compliant site, encryption at rest comes from the host's disk and database layer.
Is ExpressionEngine 6 still supported?
Only until December 31, 2026. After that date EE 6 gets no updates, including security fixes. Plan the move to EE 7 now, or to EE 8 once it ships.
Is ExpressionEngine 8 out yet?
Not as of October 20, 2026. Packet Tide aimed to release 8.0 around EEConf on October 7 to 8, 2026, but GitHub lists no 8.x release yet. On October 21, 2026, Packet Tide said EE 8 remains on track for release before the end of the year. The newest release is 7.5.28, a security release from October 20, 2026. Packet Tide says a current Pro license covers EE 8 at no extra fee.
Recap: ExpressionEngine HIPAA compliant
An ExpressionEngine HIPAA compliant site is EE on a host that signs a BAA, plus Pro, add-ons, and your policies. Packet Tide and Liquid Web's EE plans offer no BAA; Nexcess does. EE 7 has MFA but lacks field encryption and an entry edit log. Turn on secure cookies, shorten sessions, force HTTPS, and leave EE 6 before December 31, 2026.
This article is general information, not legal advice. The details here reflect expressionengine.com, the EE 7 docs, GitHub, and vendor pages as read on September 22 and 23, 2026, and re-checked October 20, 2026. EE 8.0 had not been released as of October 20, 2026. Confirm current terms with each vendor, consult qualified counsel, and base your safeguards on a documented risk analysis. We sell HIPAA compliant hosting. Reviewed October 2026.
Sources
ExpressionEngine support: Version Support.
ExpressionEngine blog: Packet Tide ownership, 2019, EE 6 end of life, and EE 8 and EEConf 2026.
ExpressionEngine docs: Requirements, Changelog, and Security and privacy settings.
ExpressionEngine member docs: Member manager and Multi-factor authentication.
ExpressionEngine docs source (7.x): Configuration overrides, Logs, and Channel Form.
ExpressionEngine docs source (7.x), utilities and files: Backup Utility and Upload directories.
GitHub: LICENSE.txt, Releases, and Security advisories.
PHP: October 21, 2026 security advisory and Supported versions. ExpressionEngine blog: PHP security alert.
Add-ons: Logit, Informer, and Freeform for ExpressionEngine.
Liquid Web: ExpressionEngine hosting and HIPAA hosting.
Nexcess: Security and compliance hosting and April 22, 2026 press release.
Cloudways: Trust Center and ExpressionEngine hosting.
Hosting.com: Do you support HIPAA-compliant hosting? and Privacy Policy. Arcustech: Master Service Agreement.
Drupal hosts: Acquia compliance and Upsun HIPAA.
AWS: HIPAA compliance. DigitalOcean: HIPAA at DigitalOcean.
45 CFR § 164.308 and § 164.312: ecfr.gov.